Cheatsheets and Checklists
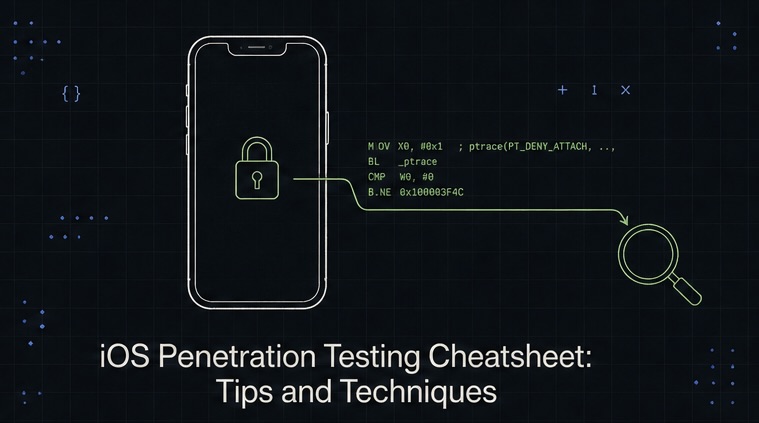
iOS Penetration Testing Cheatsheet
A hands-on guide to testing iOS app security using Frida, Objection, jailbreak detection bypass, SSL pinning, and runtime instrumentation—no fluff, just real techniques.
Practical write-ups on pentesting, tooling, CTFs, vulnerabilities and research. Written from real lab time, not copied from a manual.
Learn to test language models and AI agents, explore prompt injection, and build practical defenses with Python. Follow hands-on lessons in authorized labs, at your own pace.

Hand-picked reads. Drag, swipe or use the arrows.
A hands-on guide to testing iOS app security using Frida, Objection, jailbreak detection bypass, SSL pinning, and runtime instrumentation—no fluff, just real techniques.
A practical cheatsheet for reading, editing, debugging, and rebuilding Android apps at the Smali level, including Frida Gadget injection and Logcat printing.
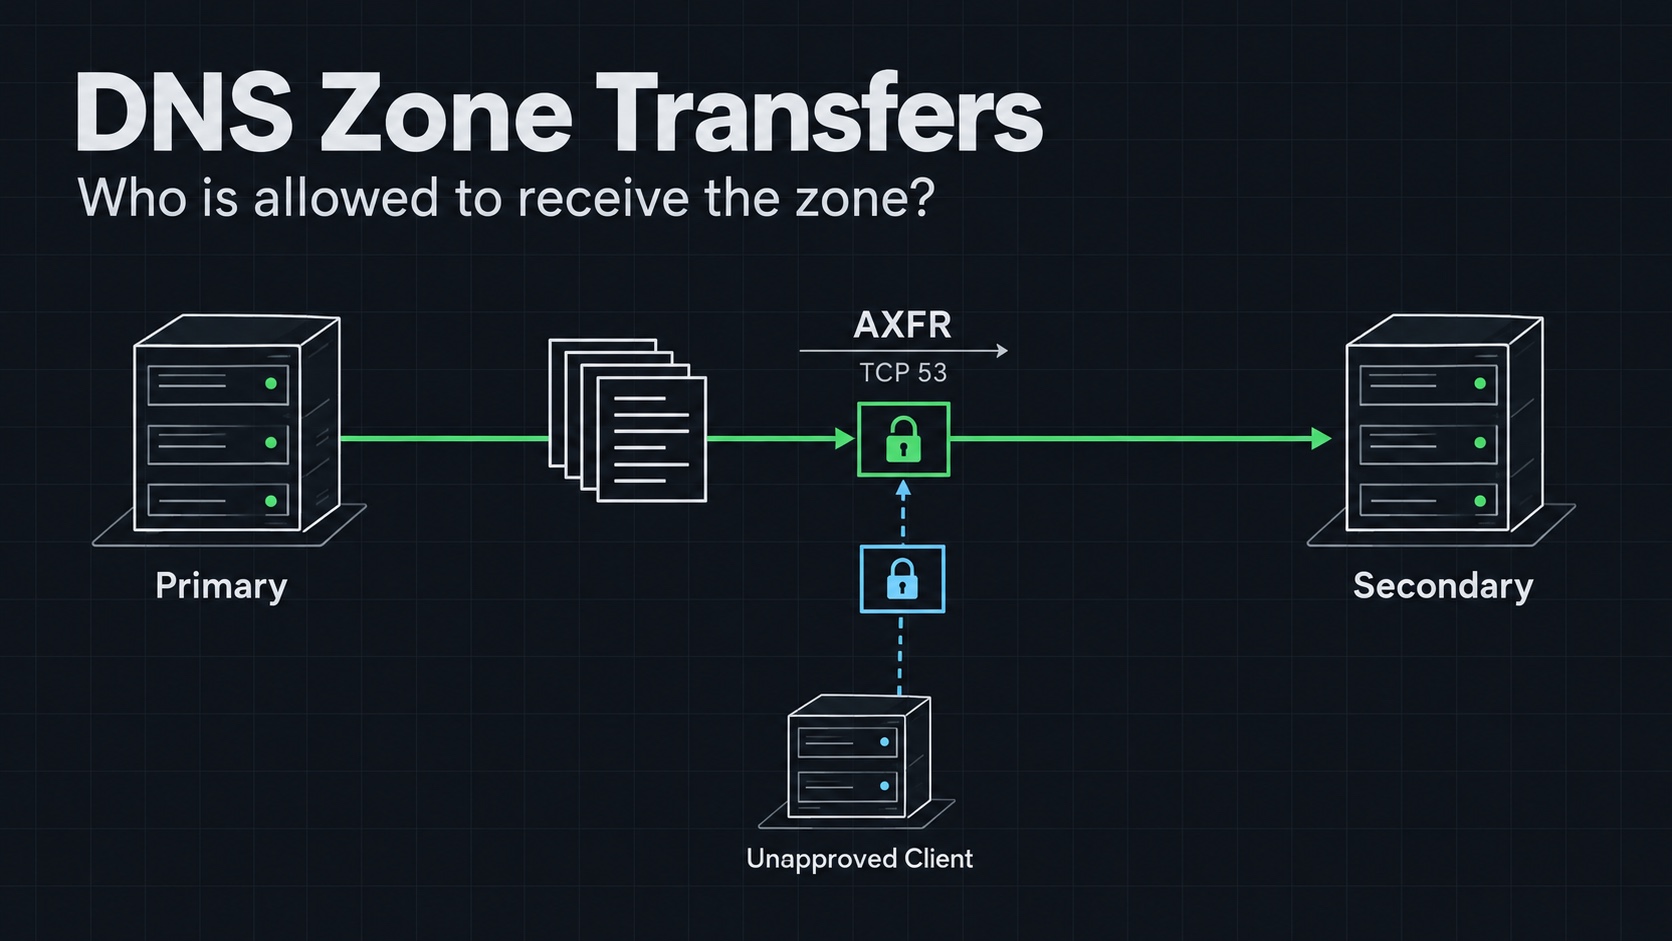
How I test DNS zone-transfer permissions, interpret the response, and restrict transfers without breaking secondary DNS servers.
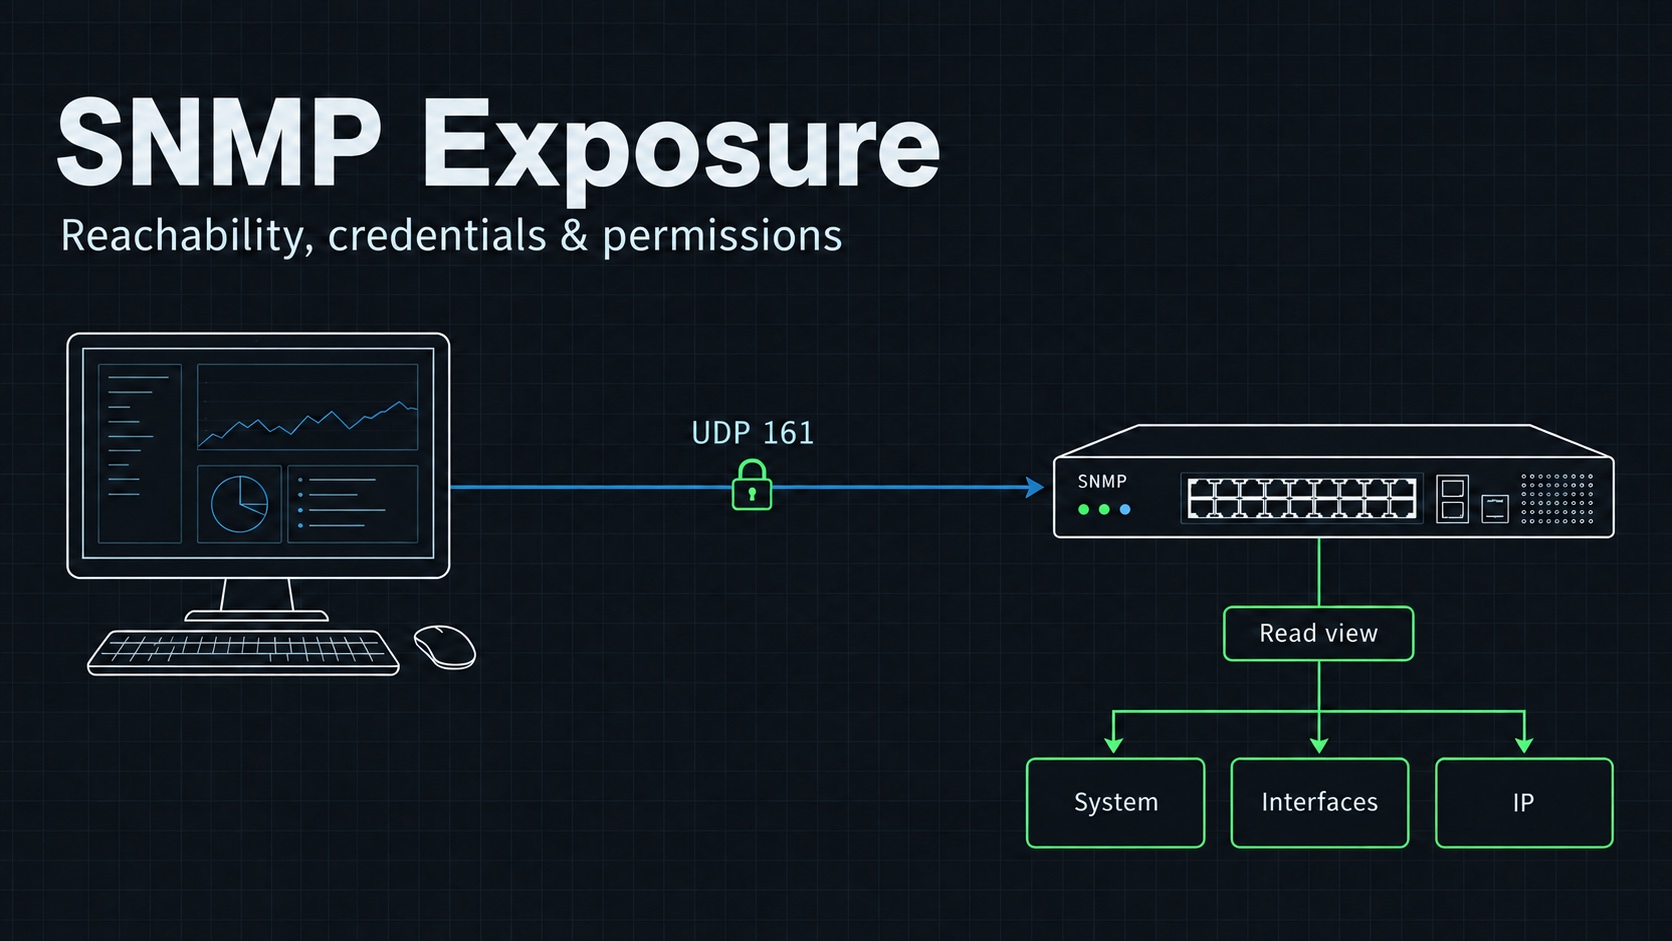
How I check SNMP exposure, interpret UDP scan results, and distinguish read access from dangerous management permissions.
How I separate Kerberoasting from Kerberos ticket forgery, check the prerequisites, and collect evidence that supports each finding.
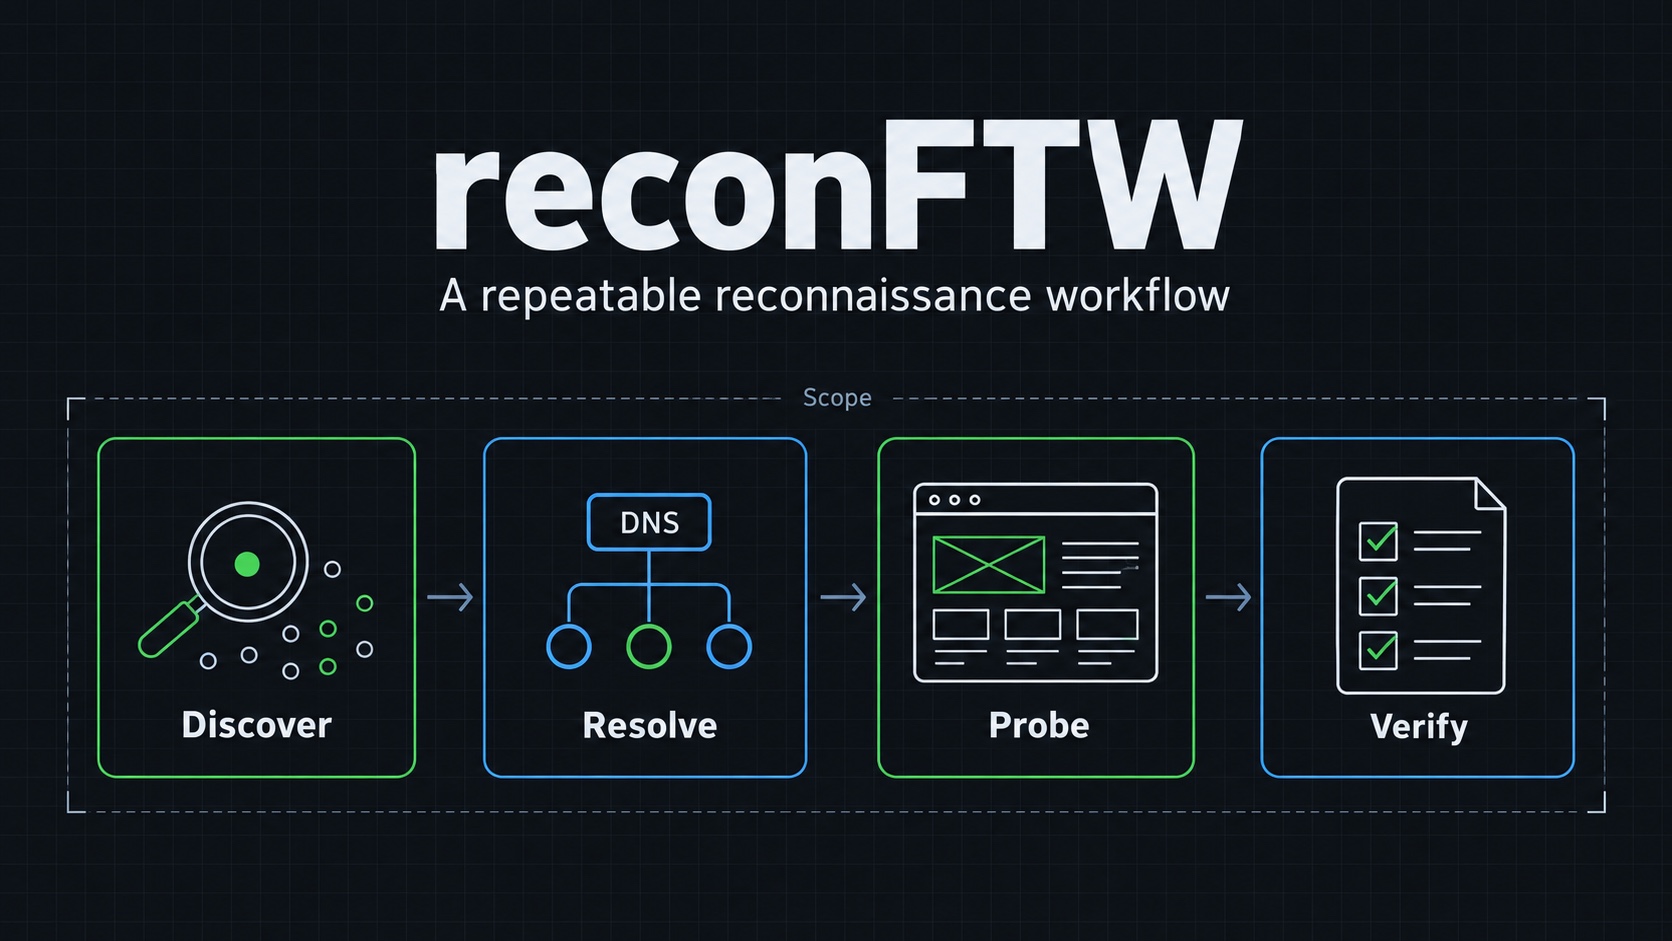
How I set up reconFTW, choose a bounded workflow, and turn collected reconnaissance data into findings I can verify.
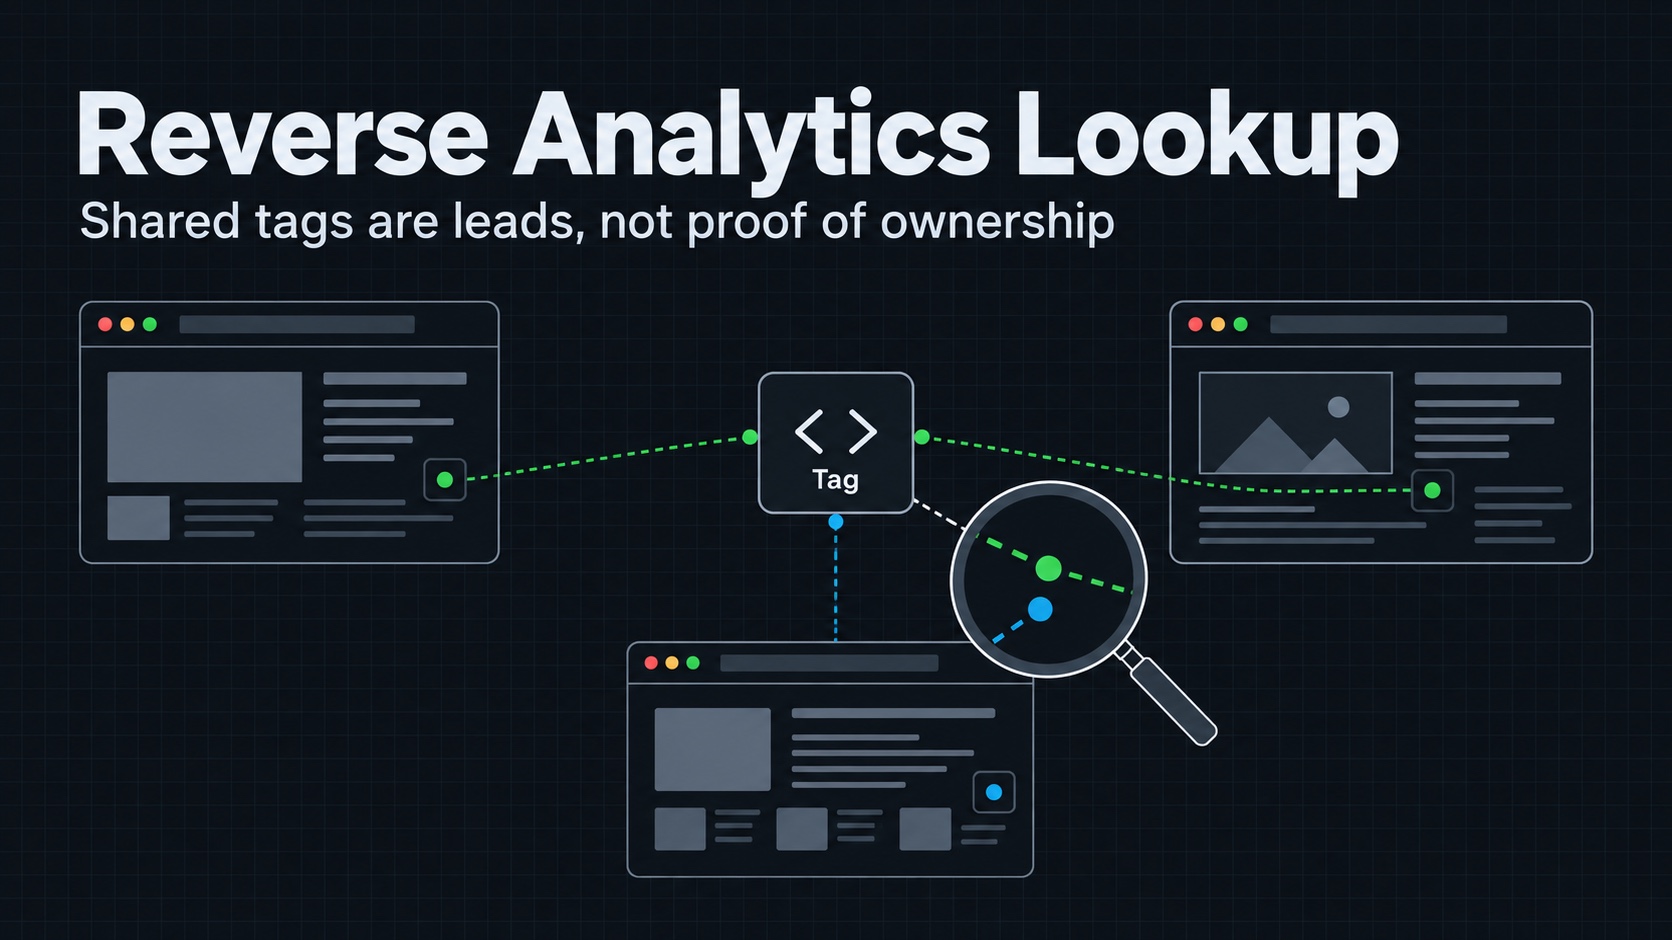
How I use shared analytics identifiers as OSINT leads, account for historical data, and avoid treating a common tag as proof of ownership.
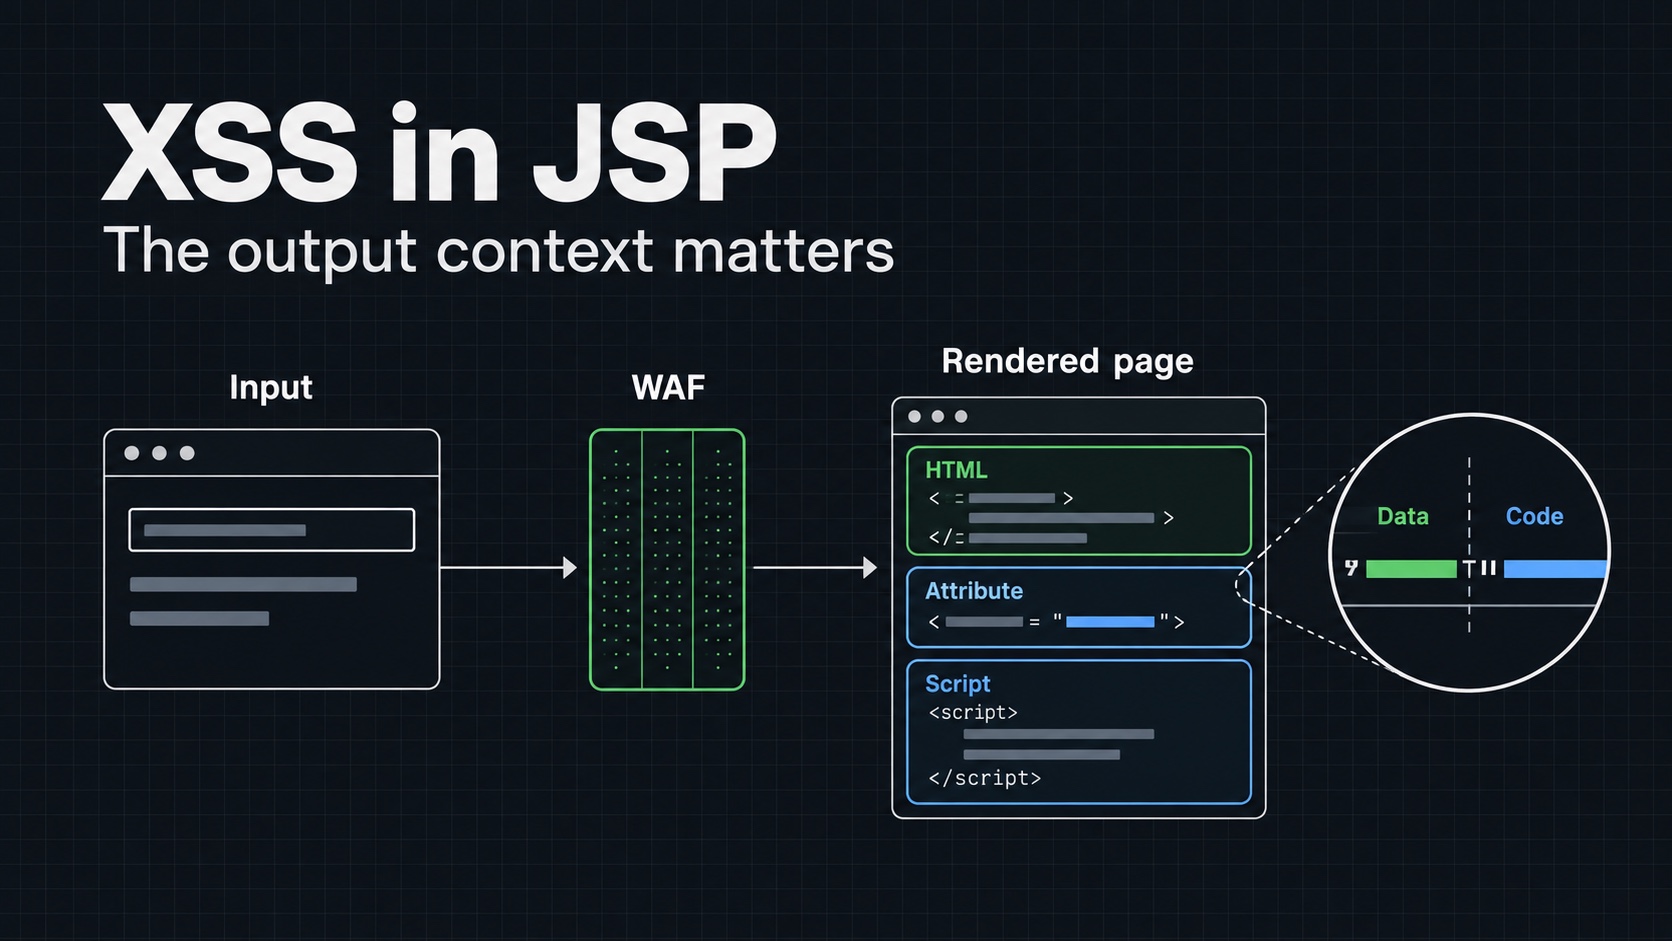
How I evaluate a small set of historical XSS probes and separate WAF behavior from a browser-confirmed application vulnerability.
One shelf per topic. Swipe sideways on each.
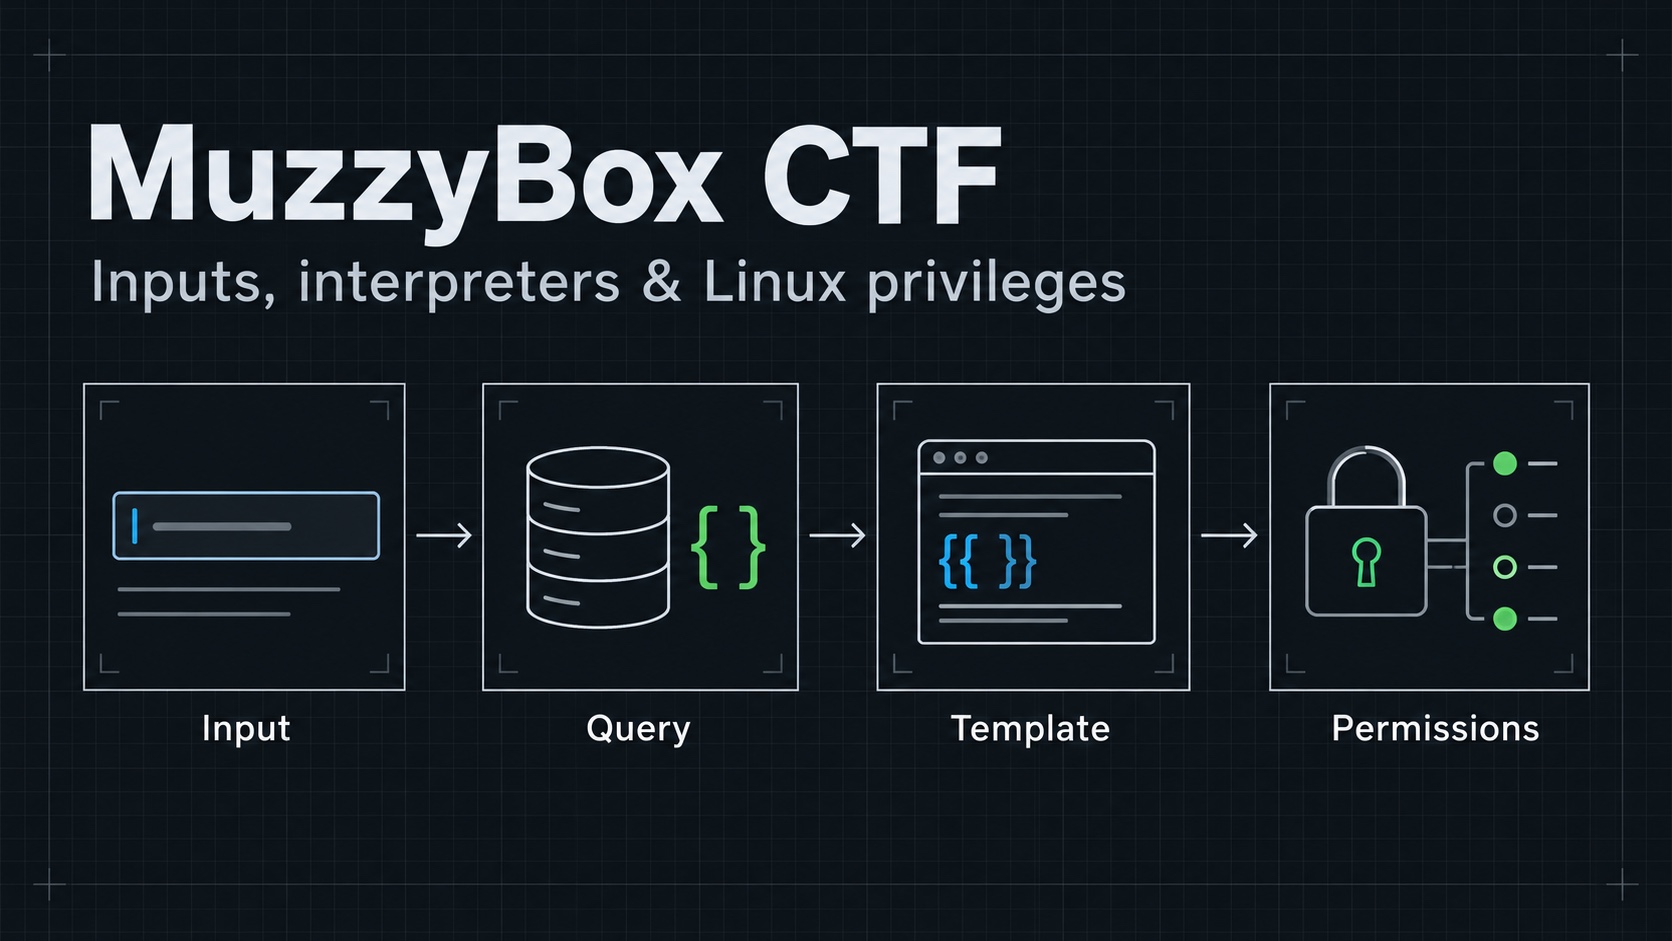
An introduction to my MuzzyBox CTF and the questions I use to investigate NoSQL injection, Python evaluation, SSTI, and Linux escalation.
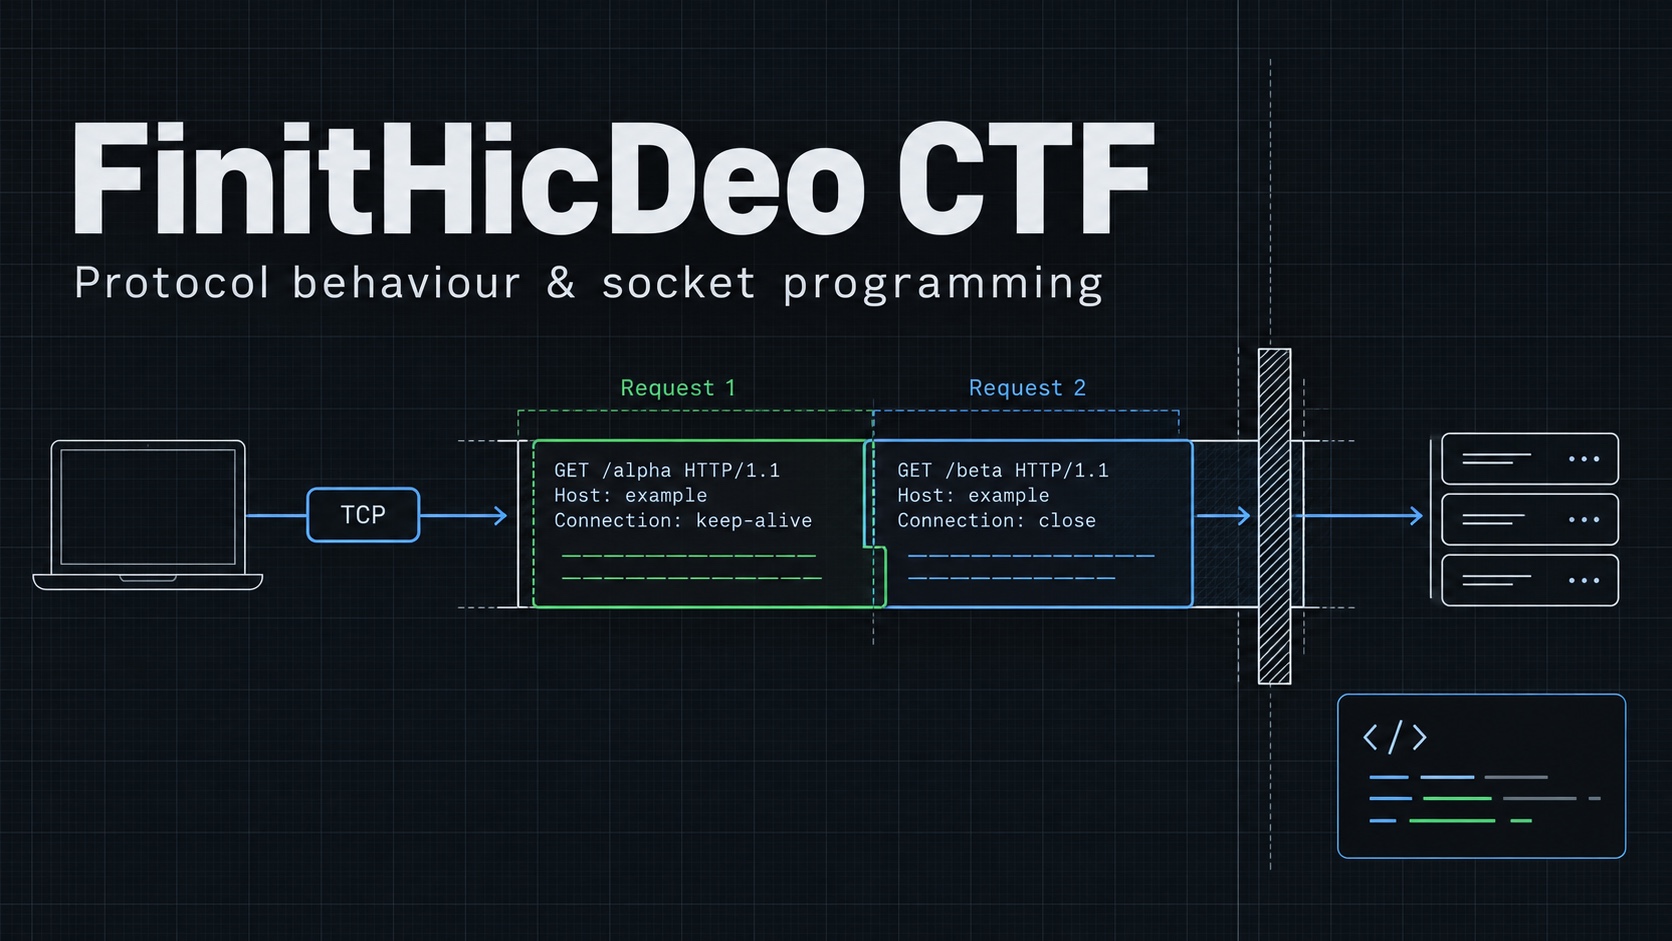
An introduction to FinitHicDeo, its programming and request-smuggling themes, and the evidence I would keep while solving the lab.
A hands-on guide to testing iOS app security using Frida, Objection, jailbreak detection bypass, SSL pinning, and runtime instrumentation—no fluff, just real techniques.
A practical cheatsheet for reading, editing, debugging, and rebuilding Android apps at the Smali level, including Frida Gadget injection and Logcat printing.
How I set up reconFTW, choose a bounded workflow, and turn collected reconnaissance data into findings I can verify.
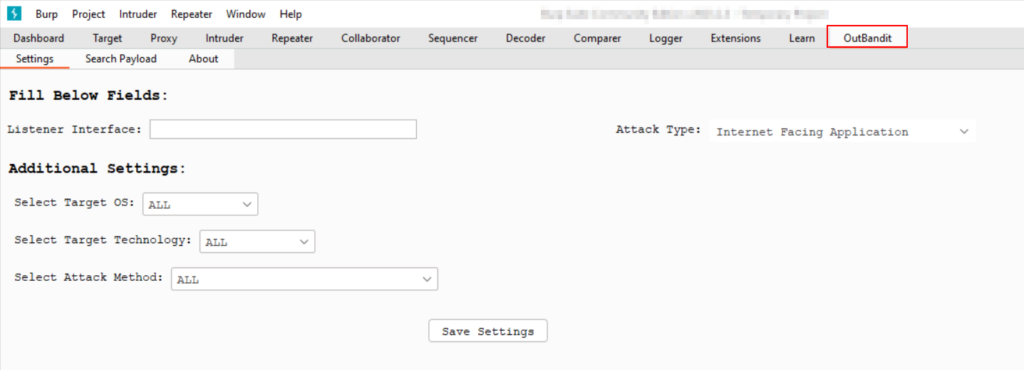
Why I built OutBandit for Burp Suite, how I approach callback testing, and what an HTTP or DNS interaction can actually prove.
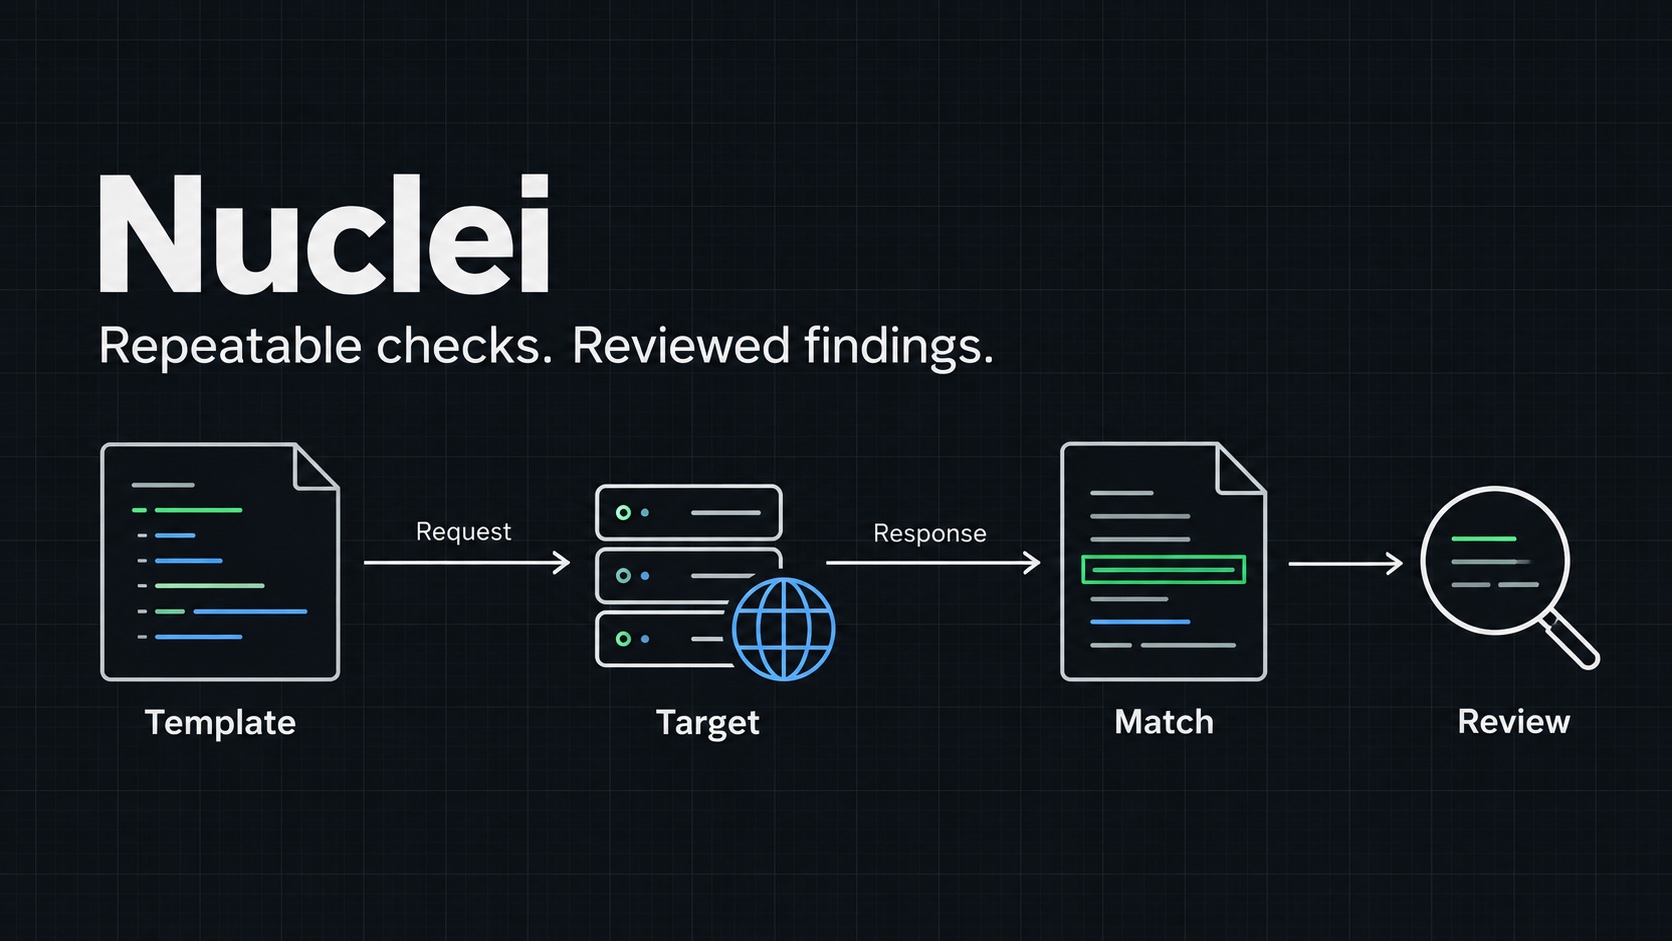
How I use Nuclei templates to run focused security checks, preserve evidence, and validate findings before reporting them.
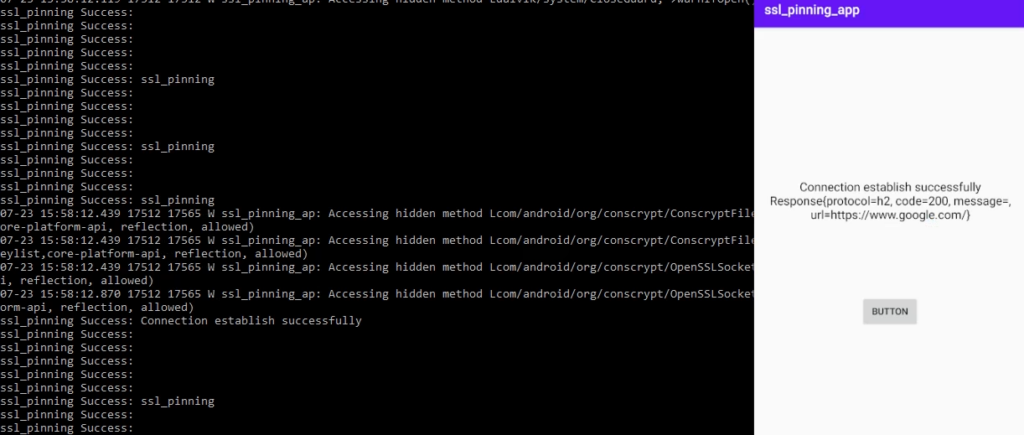
How I use Frida to inspect Android TLS behaviour, distinguish UI changes from real bypasses, and trace selected Windows API calls.
How I test DNS zone-transfer permissions, interpret the response, and restrict transfers without breaking secondary DNS servers.
How I check SNMP exposure, interpret UDP scan results, and distinguish read access from dangerous management permissions.
How I separate Kerberoasting from Kerberos ticket forgery, check the prerequisites, and collect evidence that supports each finding.
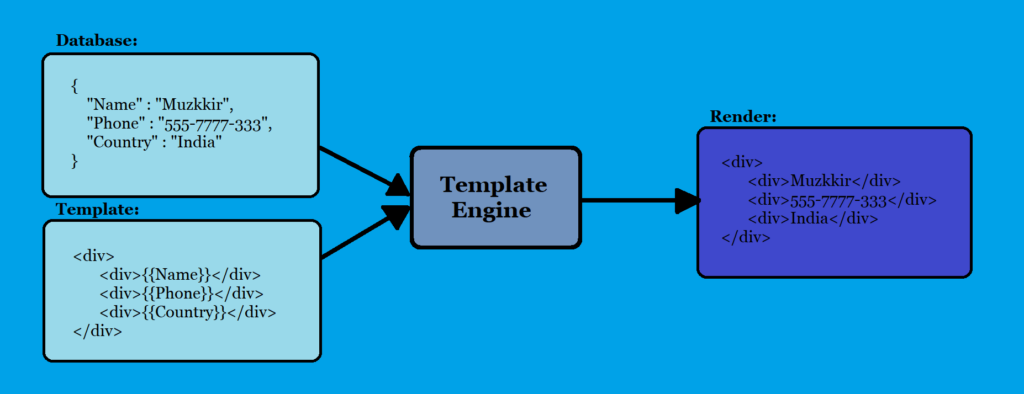
How I identify server-side template injection, reproduce it in a small Flask lab, and fix the separation between template source and data.
How I use shared analytics identifiers as OSINT leads, account for historical data, and avoid treating a common tag as proof of ownership.
How I evaluate a small set of historical XSS probes and separate WAF behavior from a browser-confirmed application vulnerability.
A practical directory for infrastructure research, threat intelligence, code search, and historical context, with corrections to older entries.
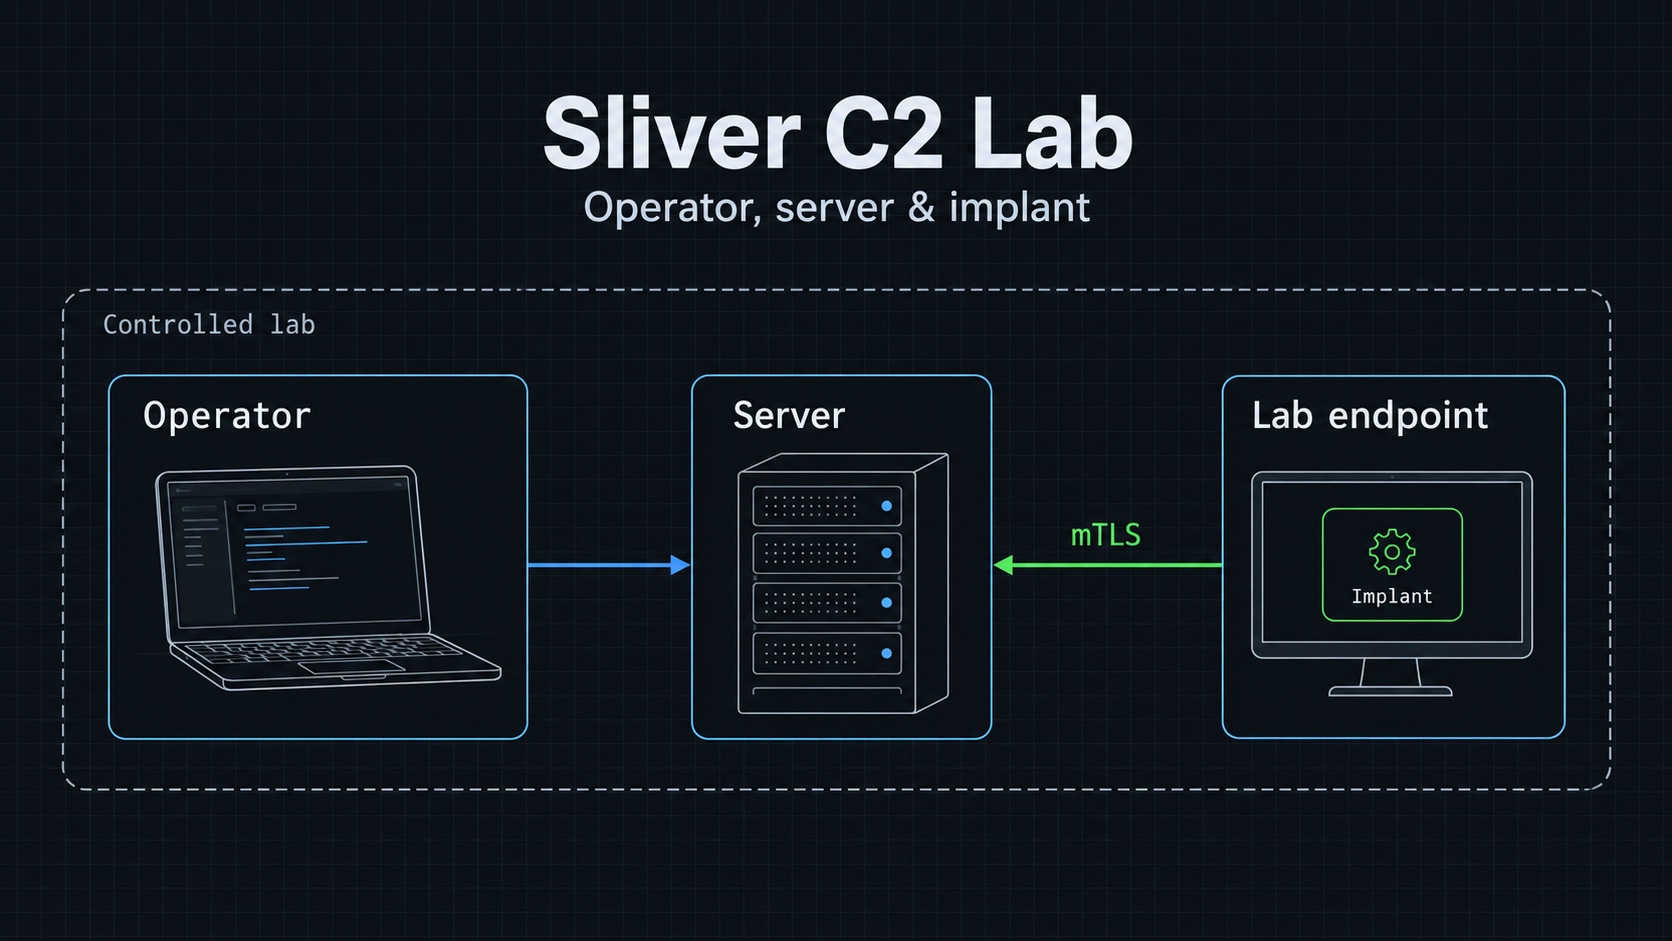
How I separate Sliver servers, operator clients, and implants, then build a bounded lab with evidence for each connection step.
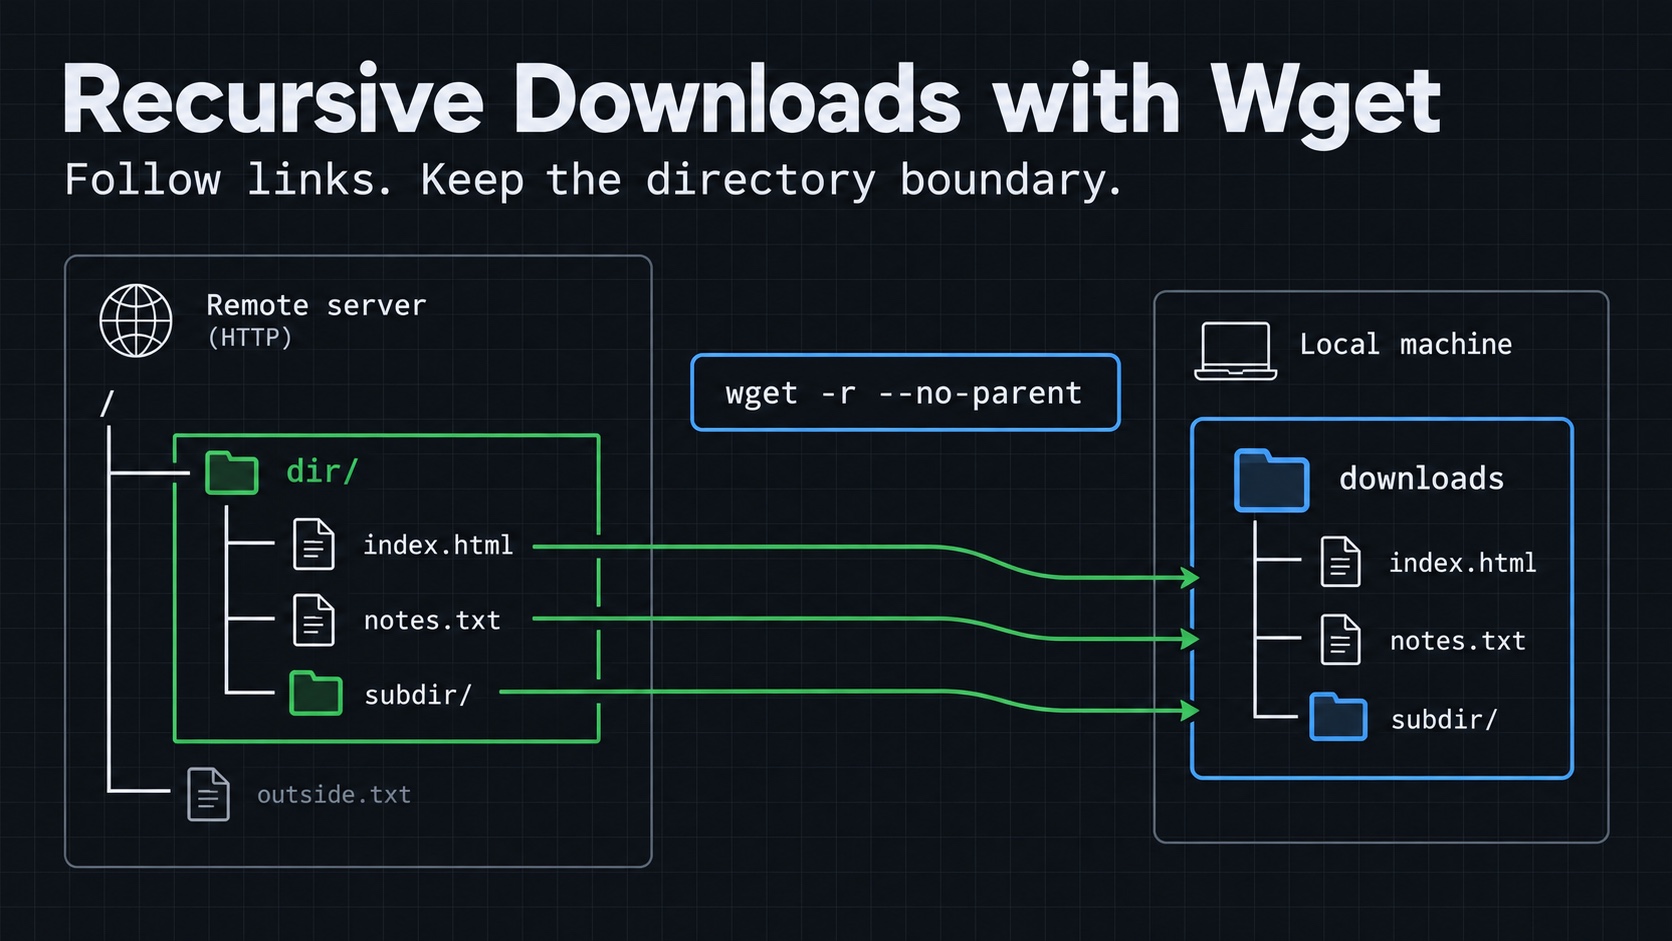
How I use Wget to download linked files under a web directory, control recursion, and check what was saved.
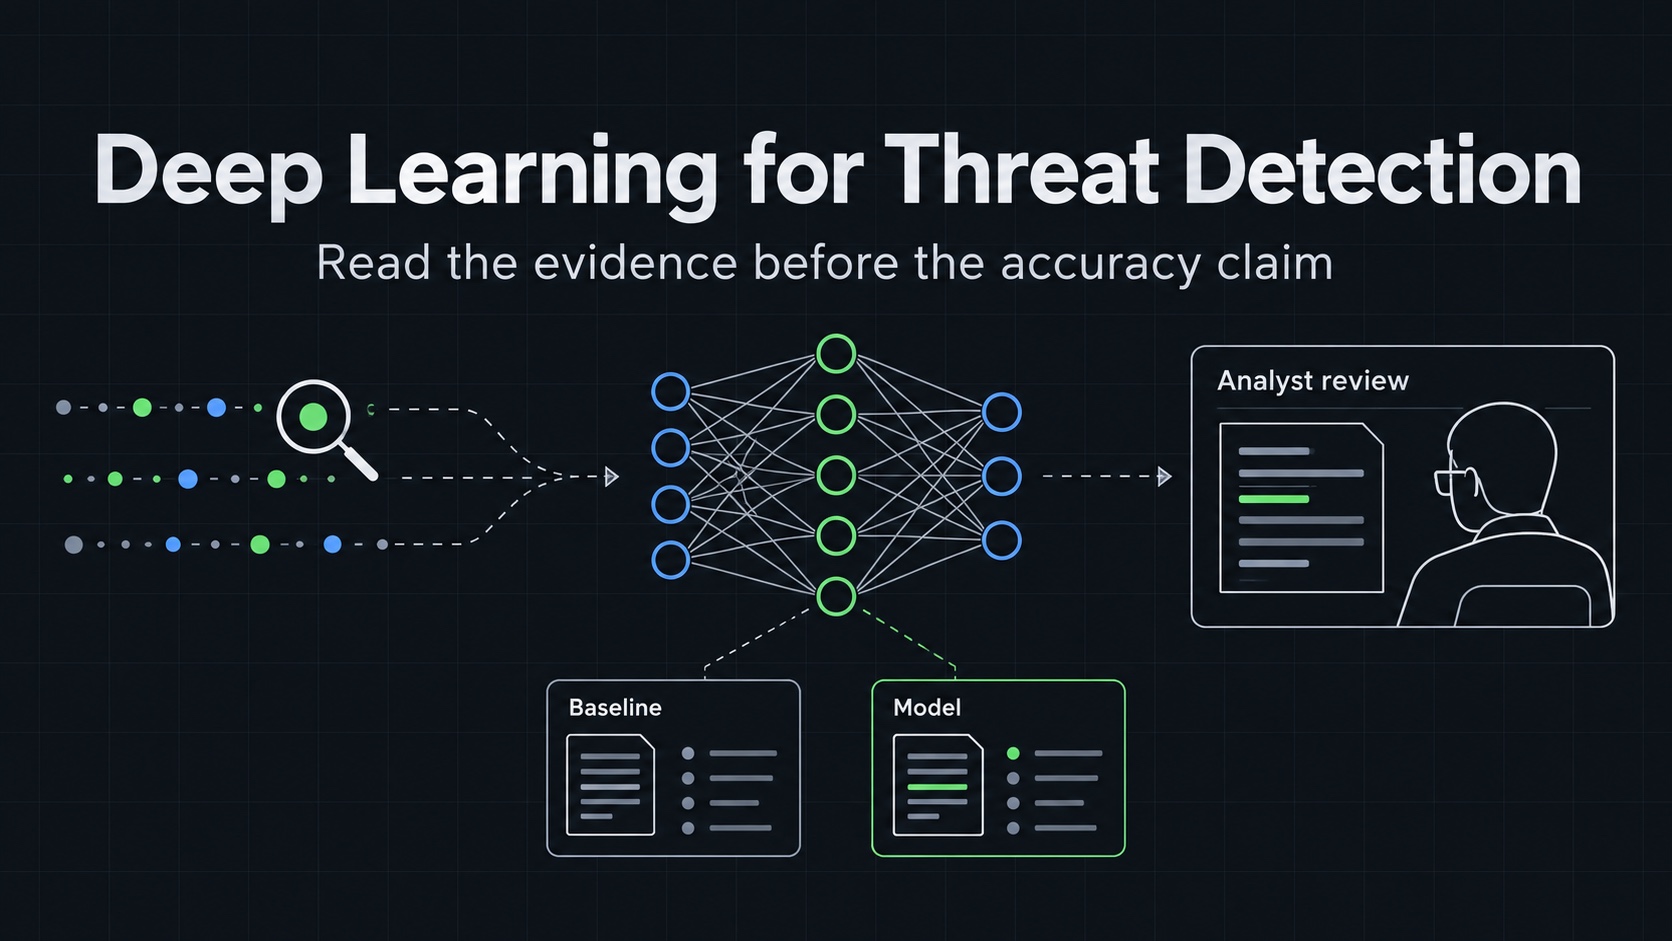
How I read a survey of deep learning for threat detection, distinguish research claims from deployment evidence, and evaluate practical tradeoffs.
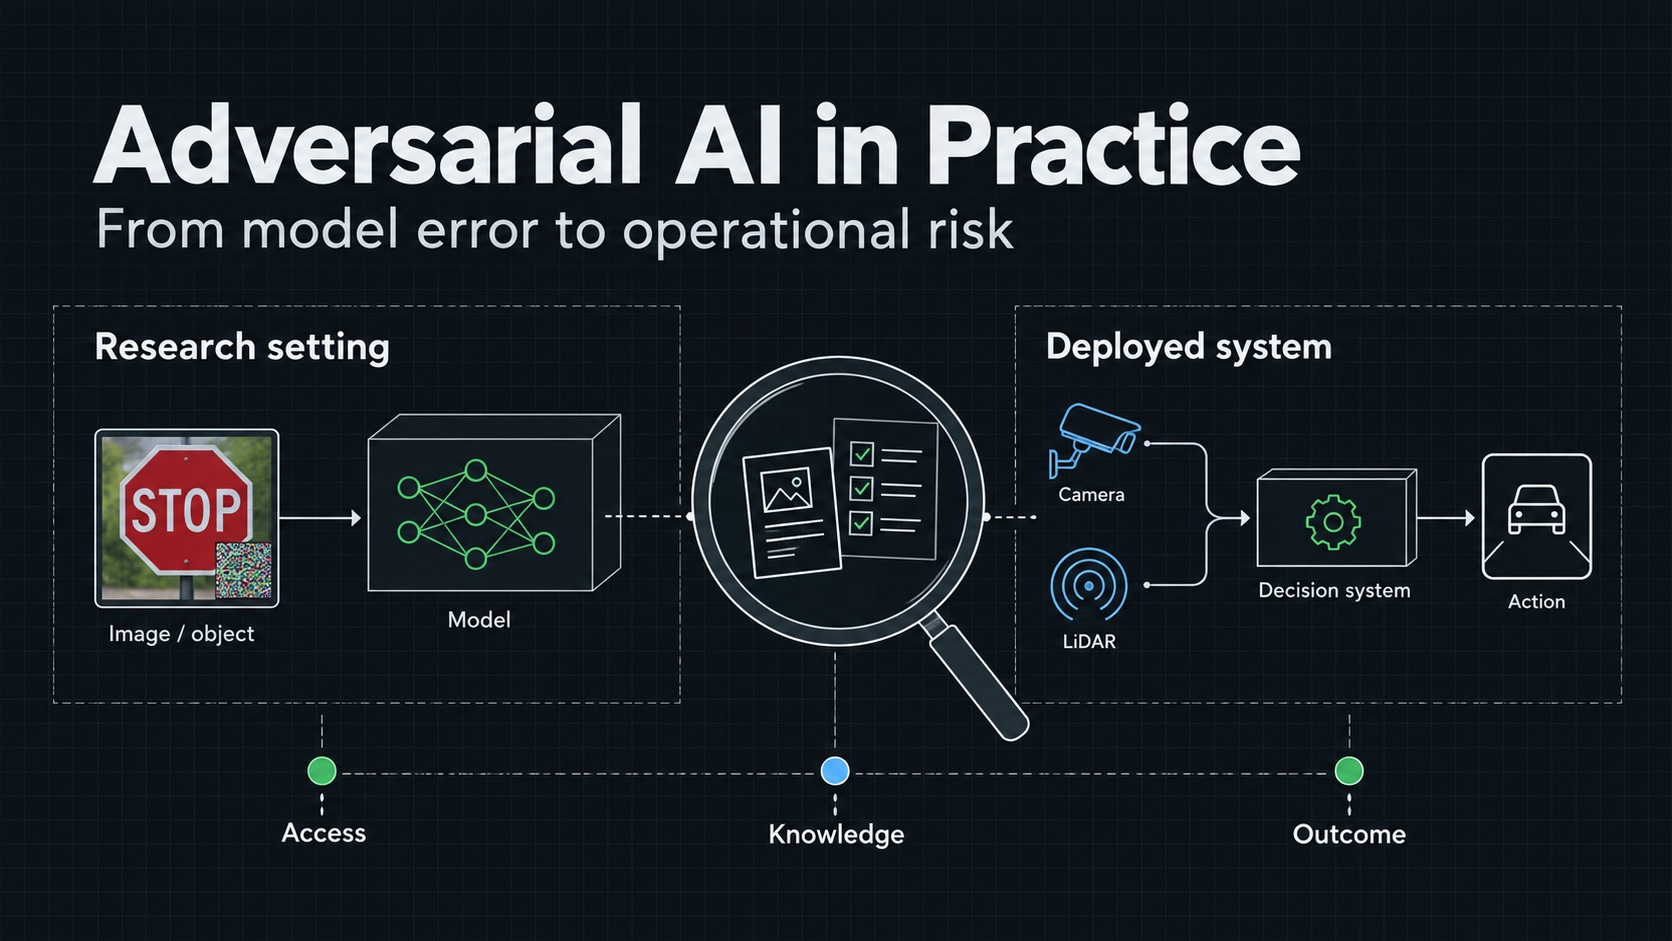
Why I separate an adversarial example in a paper from a feasible attack on a deployed system, and how that changes my risk assessment.
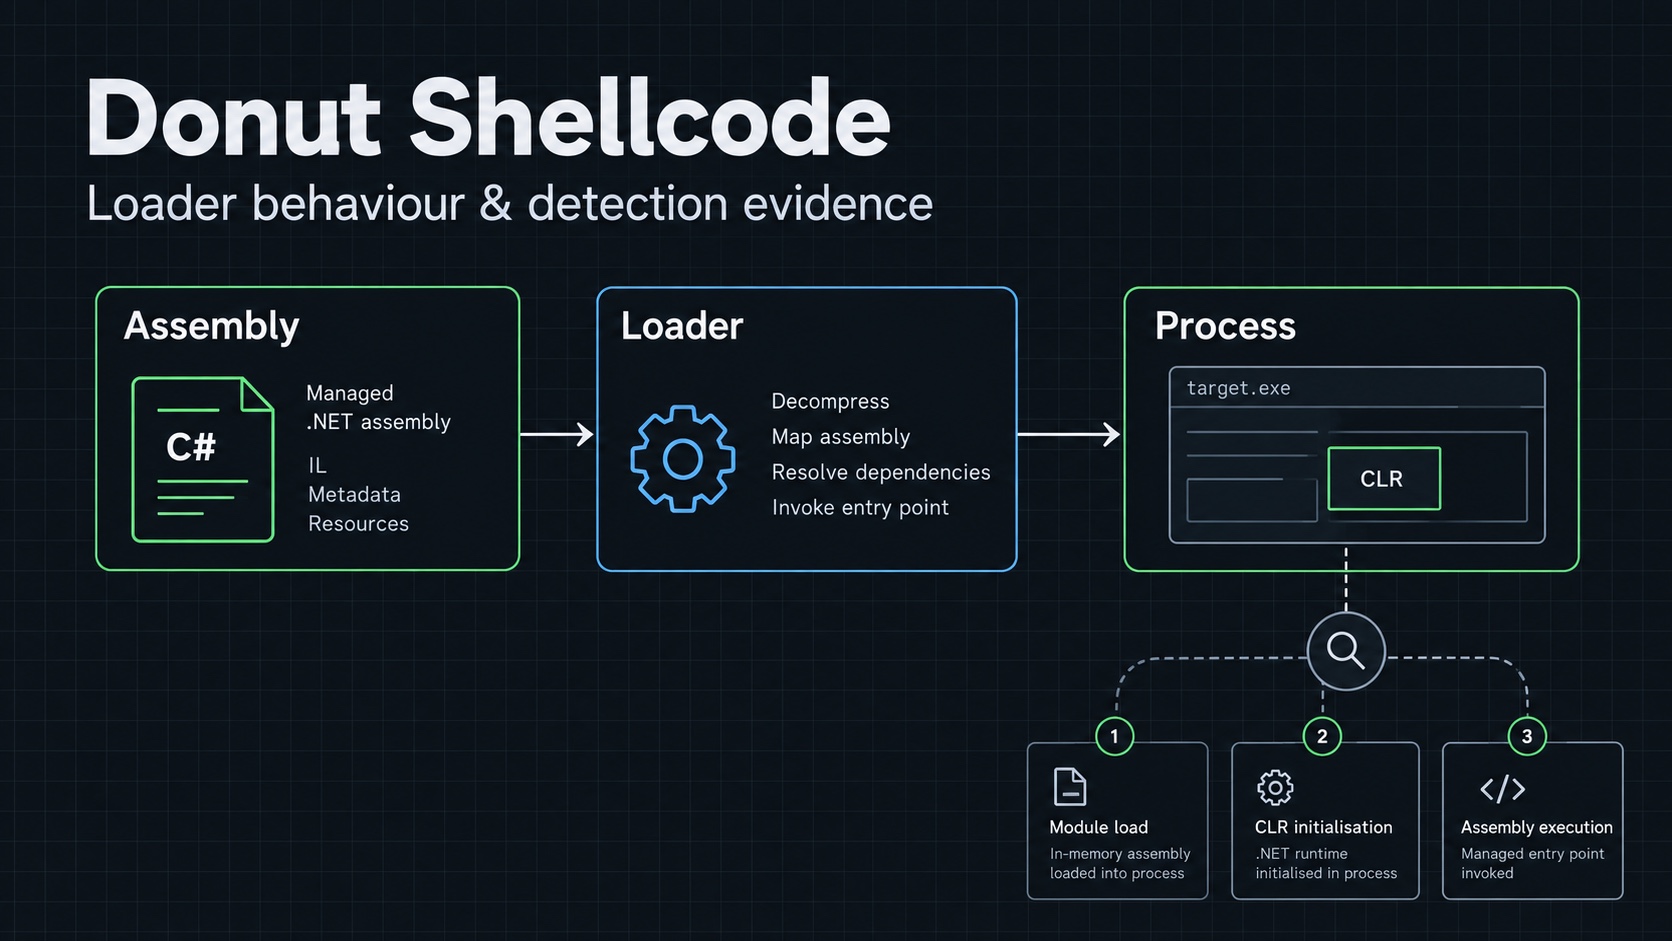
What Donut generates, how its managed-code loader works, and the evidence I need before describing any endpoint protection bypass.
Fresh from the lab notebook.
A hands-on guide to testing iOS app security using Frida, Objection, jailbreak detection bypass, SSL pinning, and runtime instrumentation—no fluff, just real techniques.
A practical cheatsheet for reading, editing, debugging, and rebuilding Android apps at the Smali level, including Frida Gadget injection and Logcat printing.
How I test DNS zone-transfer permissions, interpret the response, and restrict transfers without breaking secondary DNS servers.
How I check SNMP exposure, interpret UDP scan results, and distinguish read access from dangerous management permissions.
How I separate Kerberoasting from Kerberos ticket forgery, check the prerequisites, and collect evidence that supports each finding.
How I set up reconFTW, choose a bounded workflow, and turn collected reconnaissance data into findings I can verify.
I break things to learn how to protect them. This site is my lab notebook: recon workflows, C2 frameworks, WAF bypass experiments, CTF walkthroughs and cheatsheets.
Everything here is written in plain language and tested by hand. If a post saves you an hour, it did its job.
Your message goes straight to me. Email is optional. The form records your IP address and browser information.