Security Blogs
XSS Payloads in JSP: Why the Output Context Matters
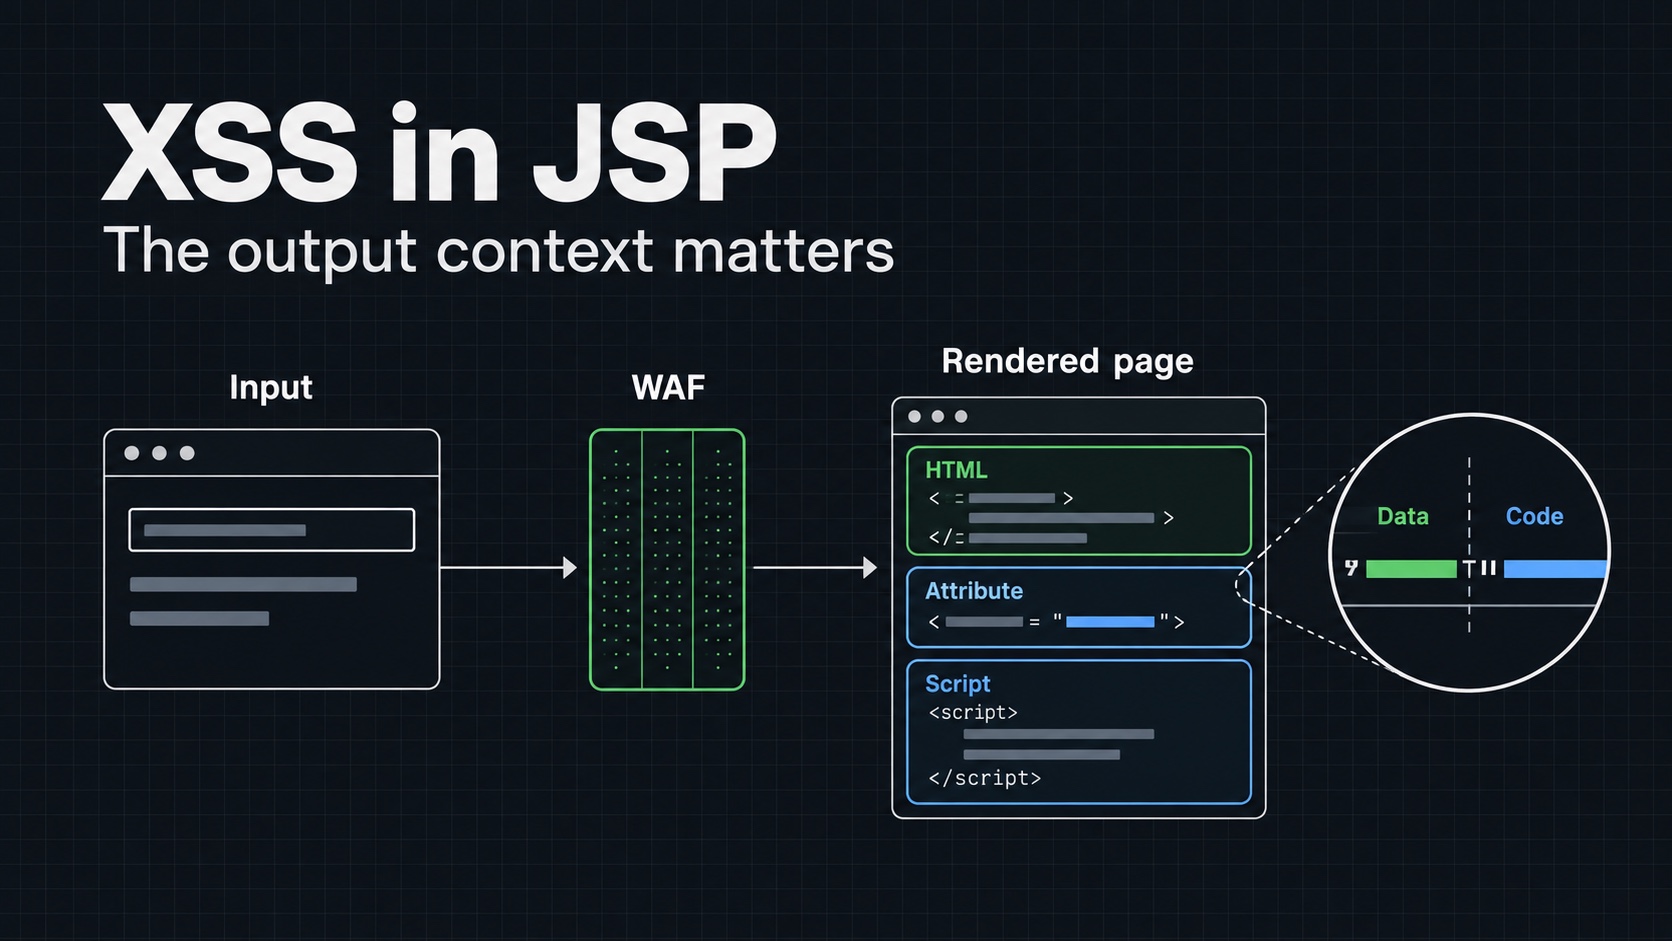
How I evaluate a small set of historical XSS probes and separate WAF behavior from a browser-confirmed application vulnerability.
How I evaluate a small set of historical XSS probes and separate WAF behavior from a browser-confirmed application vulnerability.