Security Blogs
Reverse Analytics Lookup: Connecting Domains Through Shared Tags
How I use shared analytics identifiers as OSINT leads, account for historical data, and avoid treating a common tag as proof of ownership.
Everyday security posts, research notes, and general write-ups.
How I use shared analytics identifiers as OSINT leads, account for historical data, and avoid treating a common tag as proof of ownership.
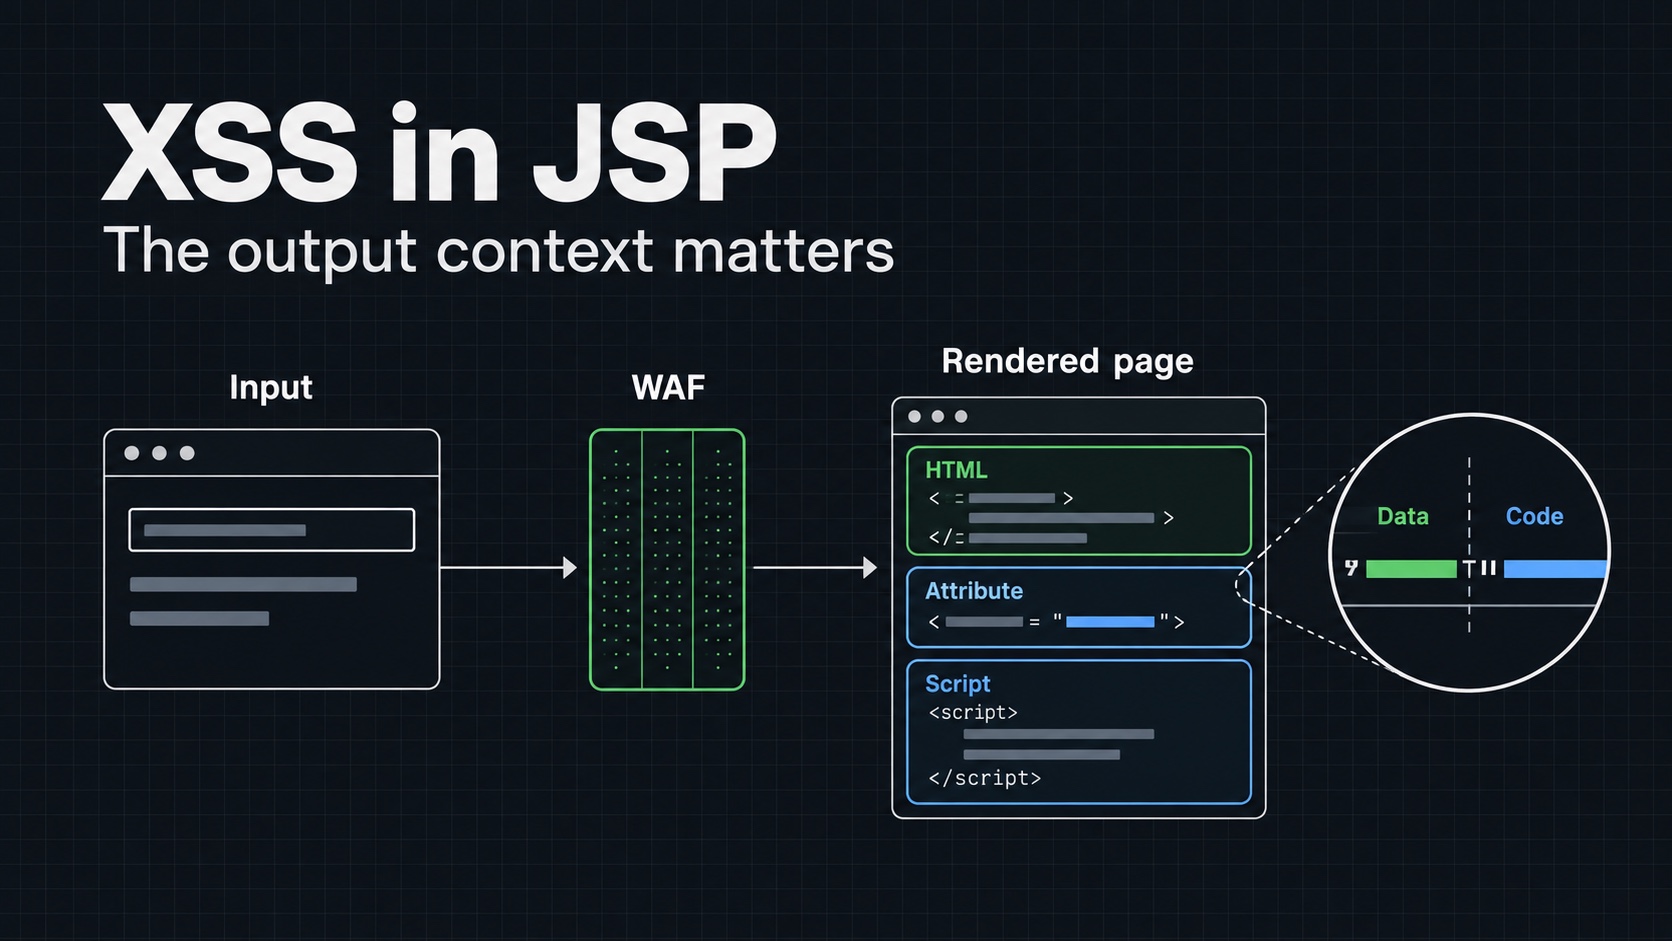
How I evaluate a small set of historical XSS probes and separate WAF behavior from a browser-confirmed application vulnerability.
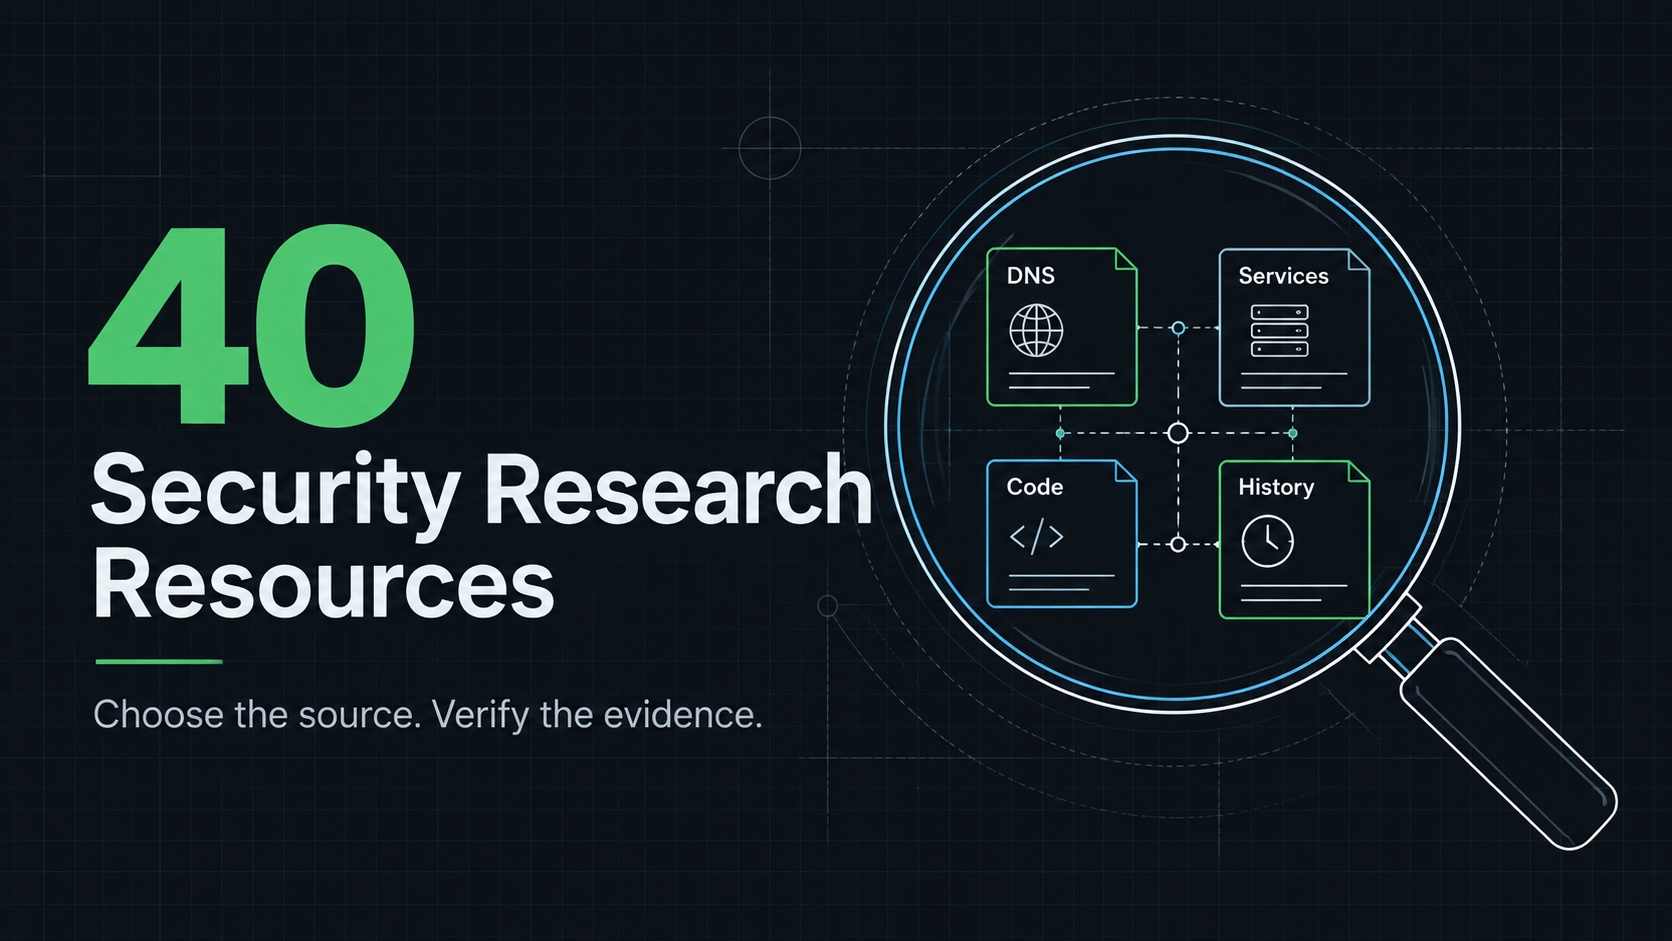
A practical directory for infrastructure research, threat intelligence, code search, and historical context, with corrections to older entries.
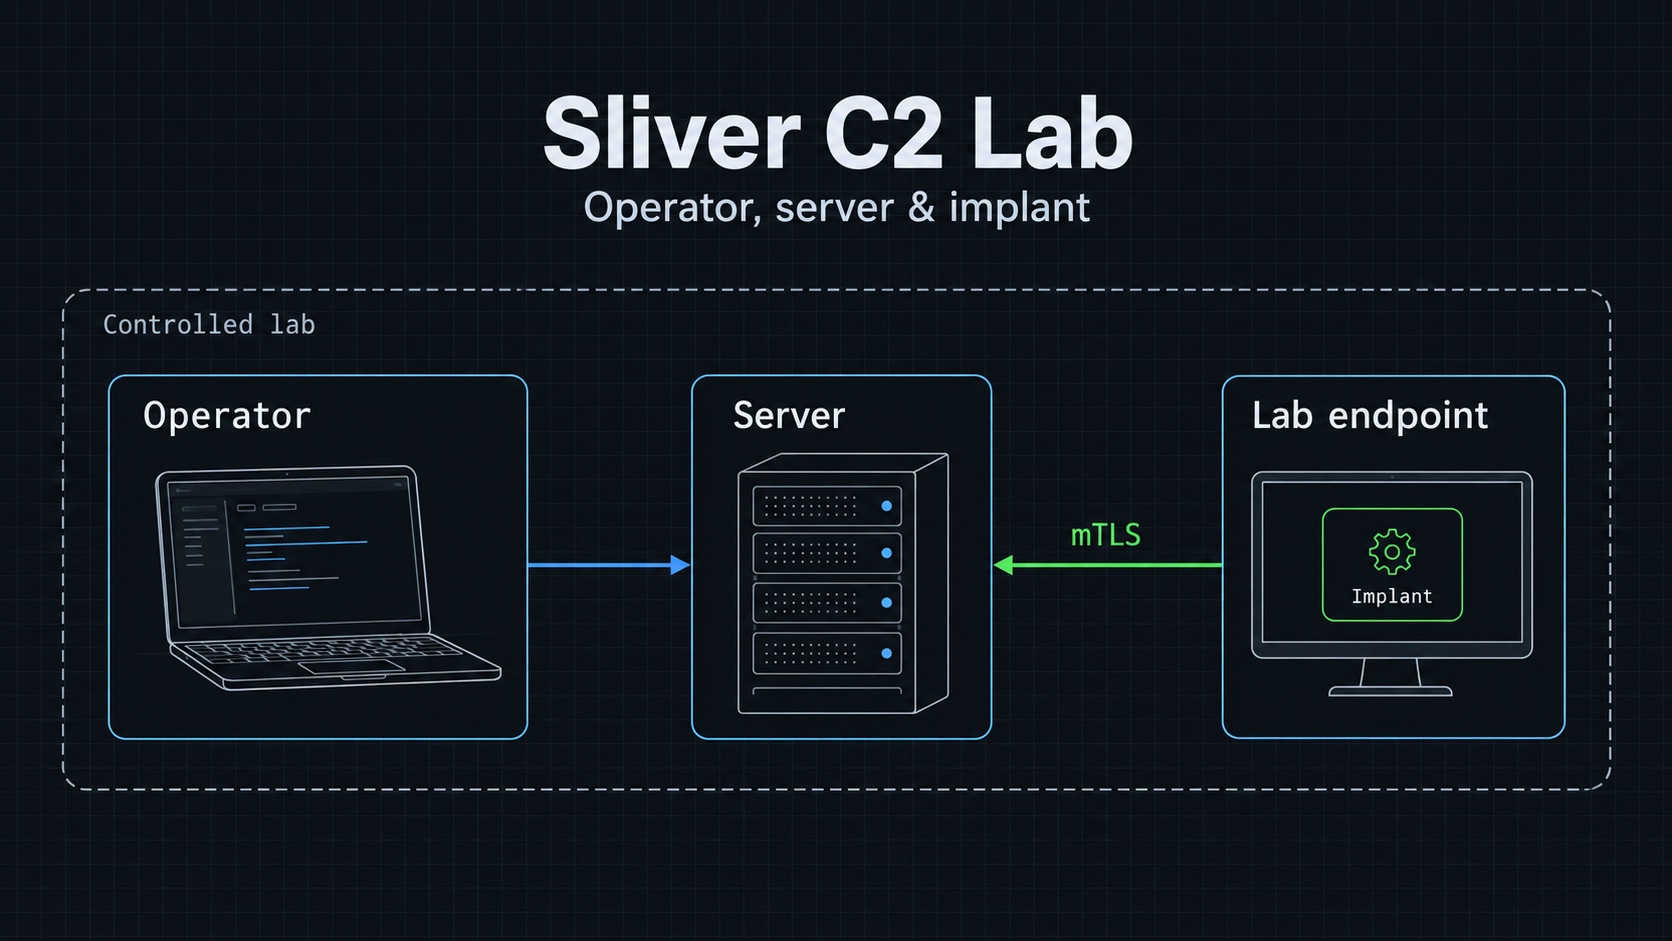
How I separate Sliver servers, operator clients, and implants, then build a bounded lab with evidence for each connection step.
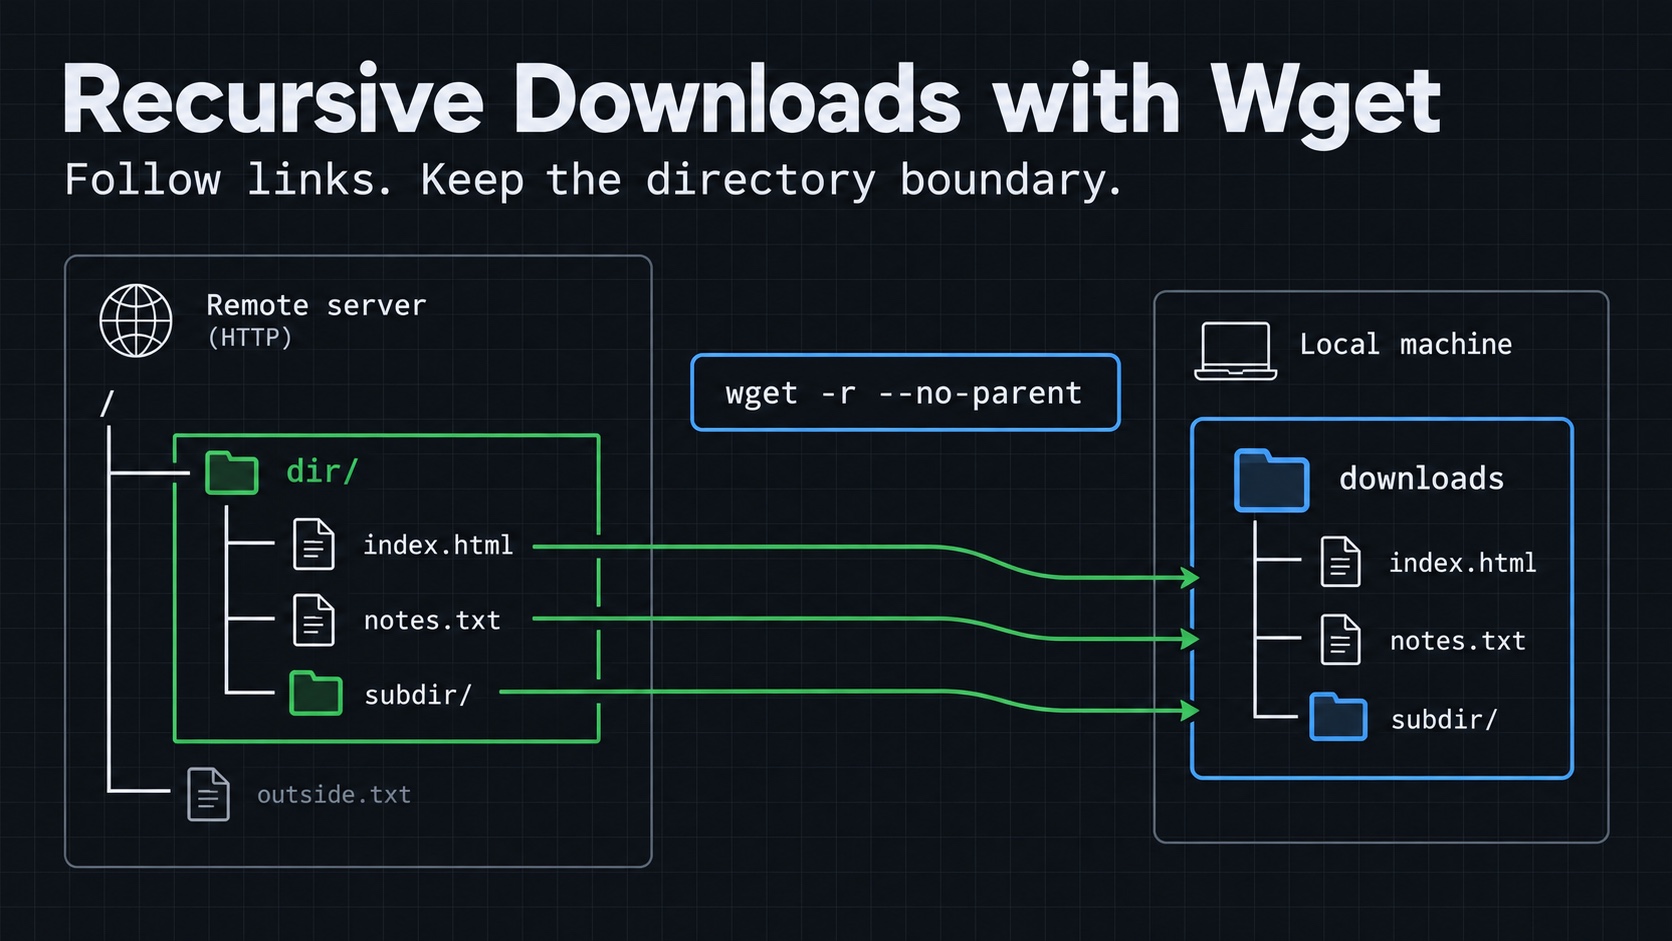
How I use Wget to download linked files under a web directory, control recursion, and check what was saved.
How I read a survey of deep learning for threat detection, distinguish research claims from deployment evidence, and evaluate practical tradeoffs.
Why I separate an adversarial example in a paper from a feasible attack on a deployed system, and how that changes my risk assessment.
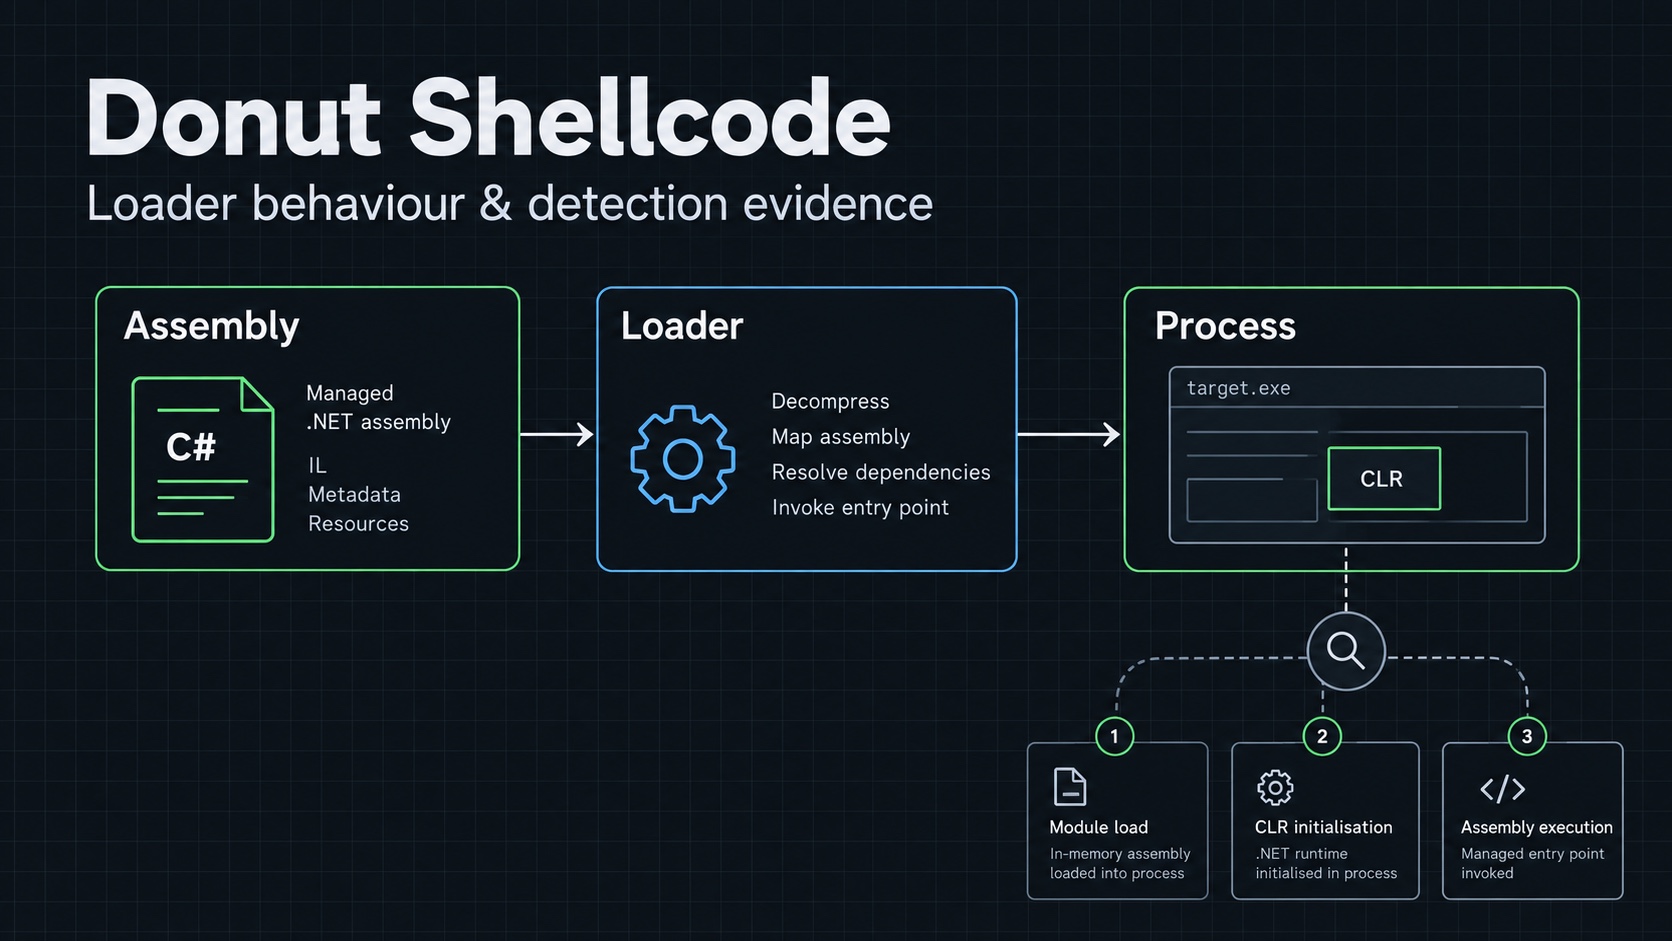
What Donut generates, how its managed-code loader works, and the evidence I need before describing any endpoint protection bypass.