Cheatsheets and Checklists
iOS Penetration Testing Cheatsheet
A hands-on guide to testing iOS app security using Frida, Objection, jailbreak detection bypass, SSL pinning, and runtime instrumentation—no fluff, just real techniques.
A hands-on guide to testing iOS app security using Frida, Objection, jailbreak detection bypass, SSL pinning, and runtime instrumentation—no fluff, just real techniques.
A practical cheatsheet for reading, editing, debugging, and rebuilding Android apps at the Smali level, including Frida Gadget injection and Logcat printing.
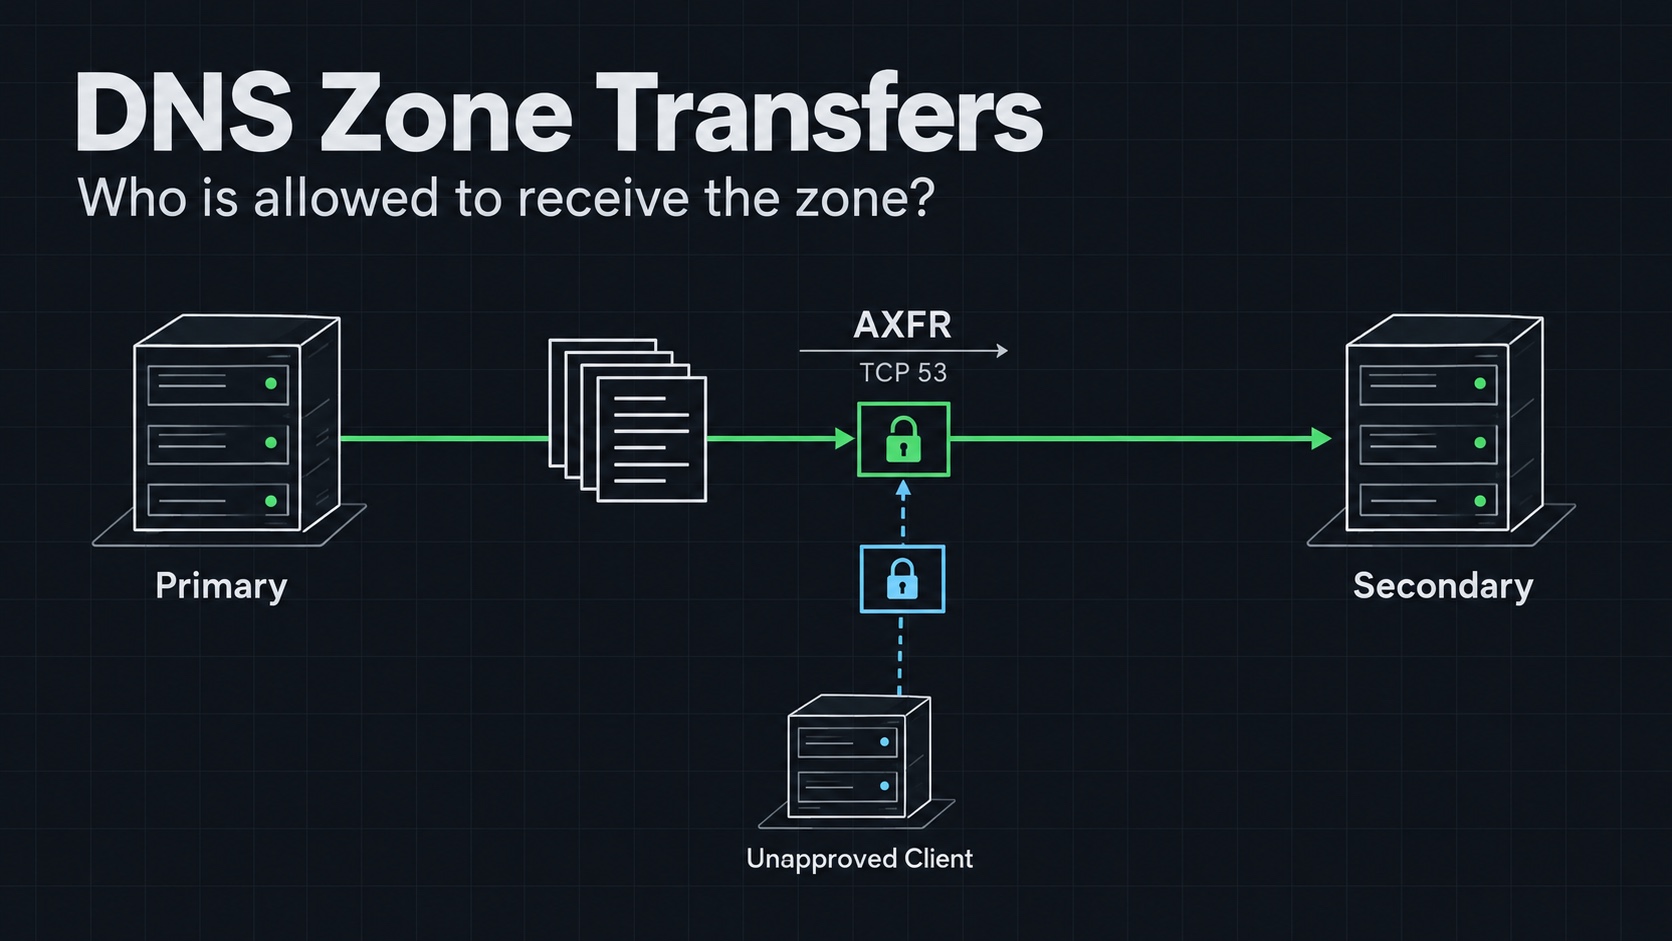
How I test DNS zone-transfer permissions, interpret the response, and restrict transfers without breaking secondary DNS servers.
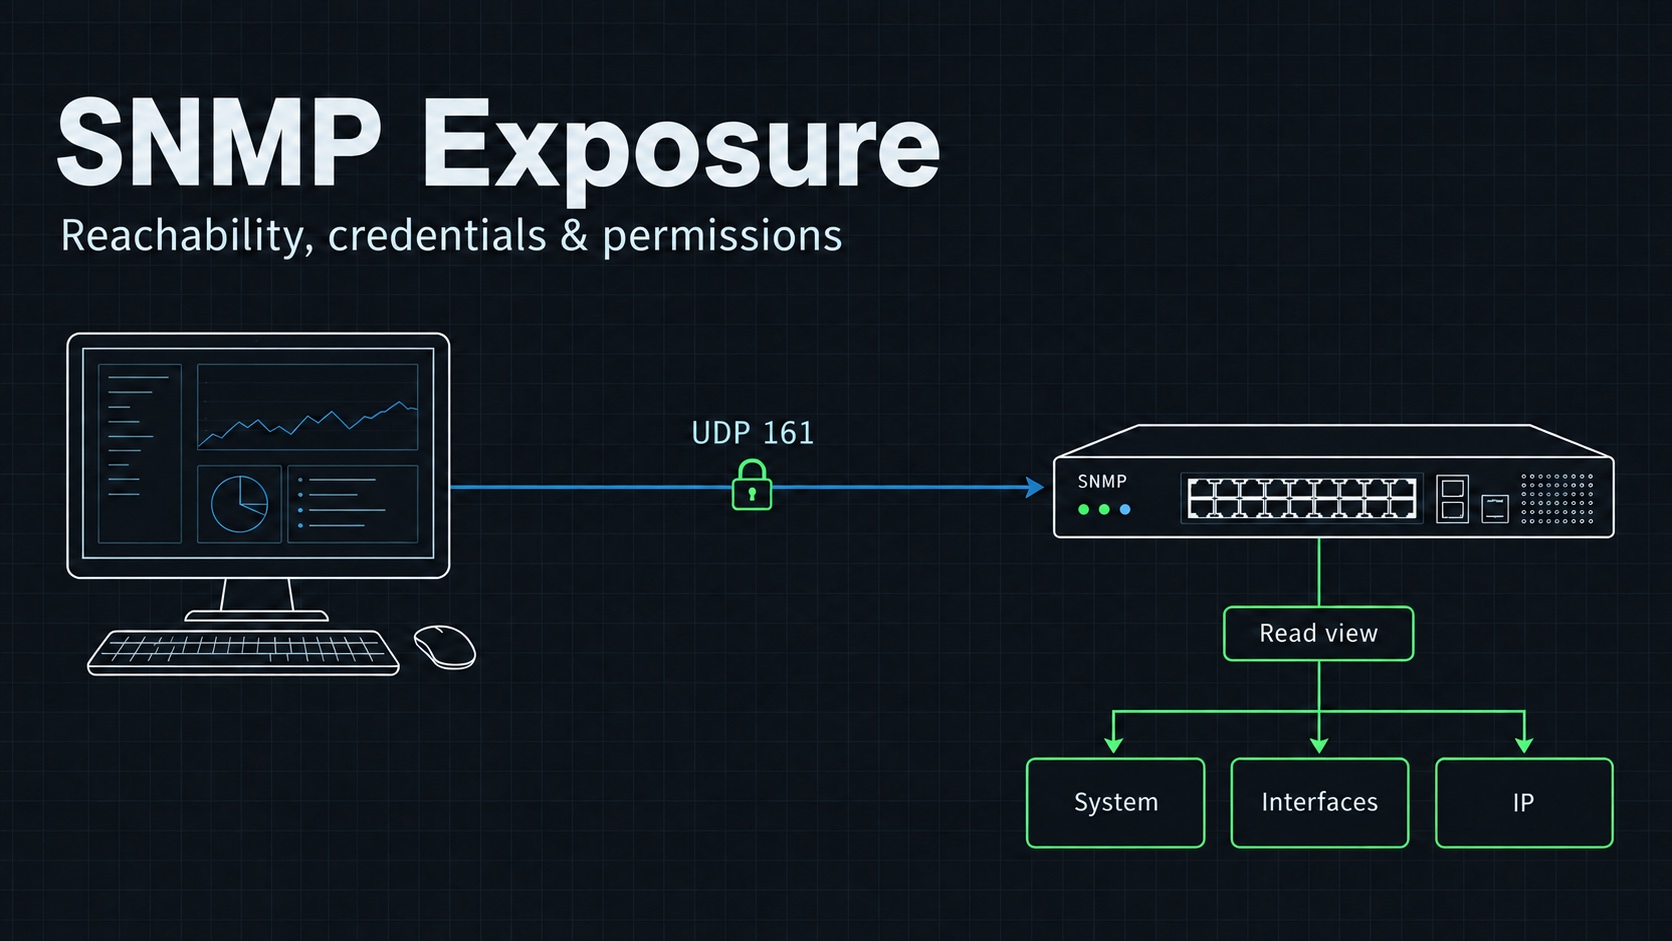
How I check SNMP exposure, interpret UDP scan results, and distinguish read access from dangerous management permissions.
How I separate Kerberoasting from Kerberos ticket forgery, check the prerequisites, and collect evidence that supports each finding.
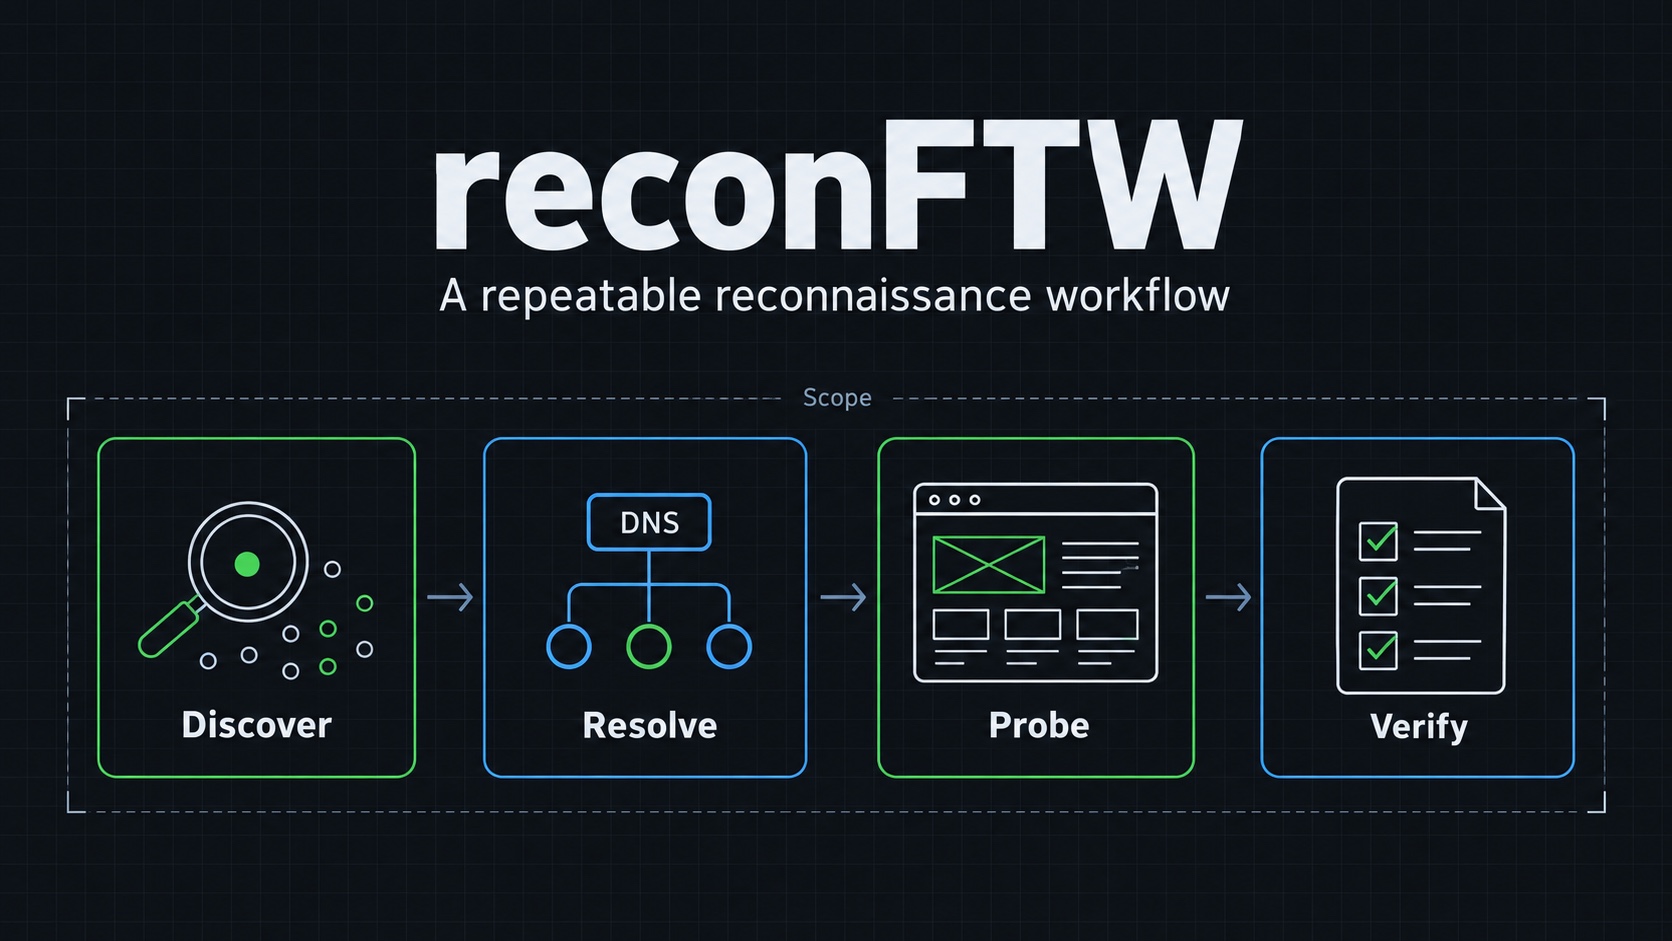
How I set up reconFTW, choose a bounded workflow, and turn collected reconnaissance data into findings I can verify.
How I use shared analytics identifiers as OSINT leads, account for historical data, and avoid treating a common tag as proof of ownership.
How I evaluate a small set of historical XSS probes and separate WAF behavior from a browser-confirmed application vulnerability.
A practical directory for infrastructure research, threat intelligence, code search, and historical context, with corrections to older entries.