Tools and Scripting
reconFTW: Building a Repeatable Reconnaissance Workflow
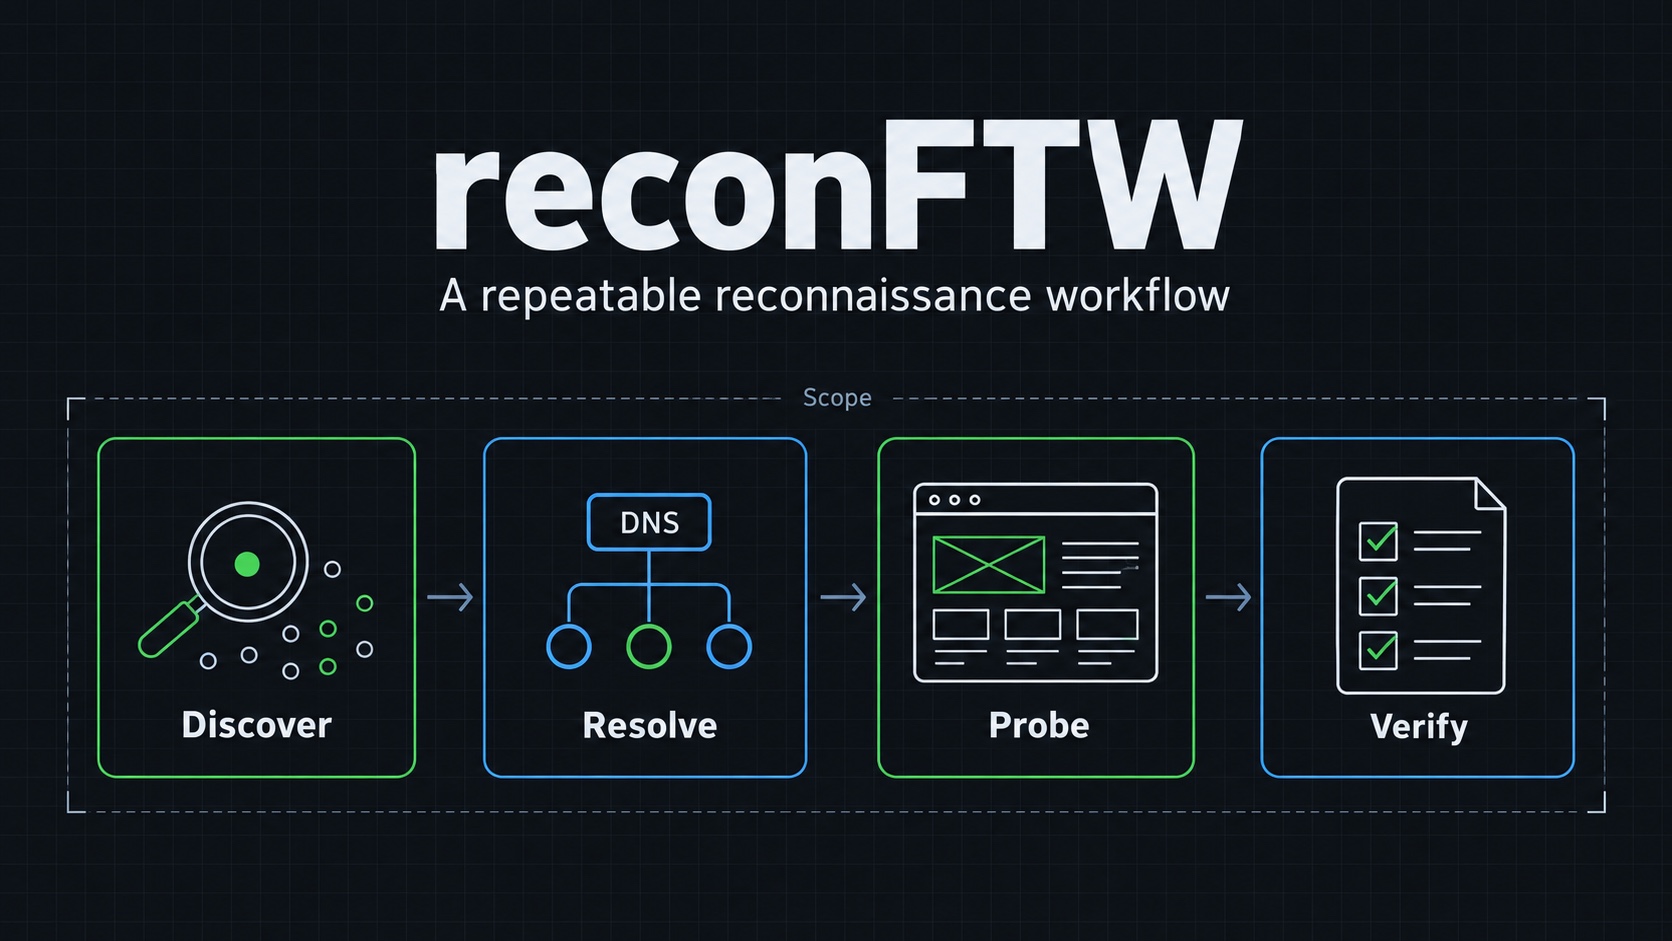
How I set up reconFTW, choose a bounded workflow, and turn collected reconnaissance data into findings I can verify.
Security tools, automation, scripts, and practical guides.
How I set up reconFTW, choose a bounded workflow, and turn collected reconnaissance data into findings I can verify.
Why I built OutBandit for Burp Suite, how I approach callback testing, and what an HTTP or DNS interaction can actually prove.
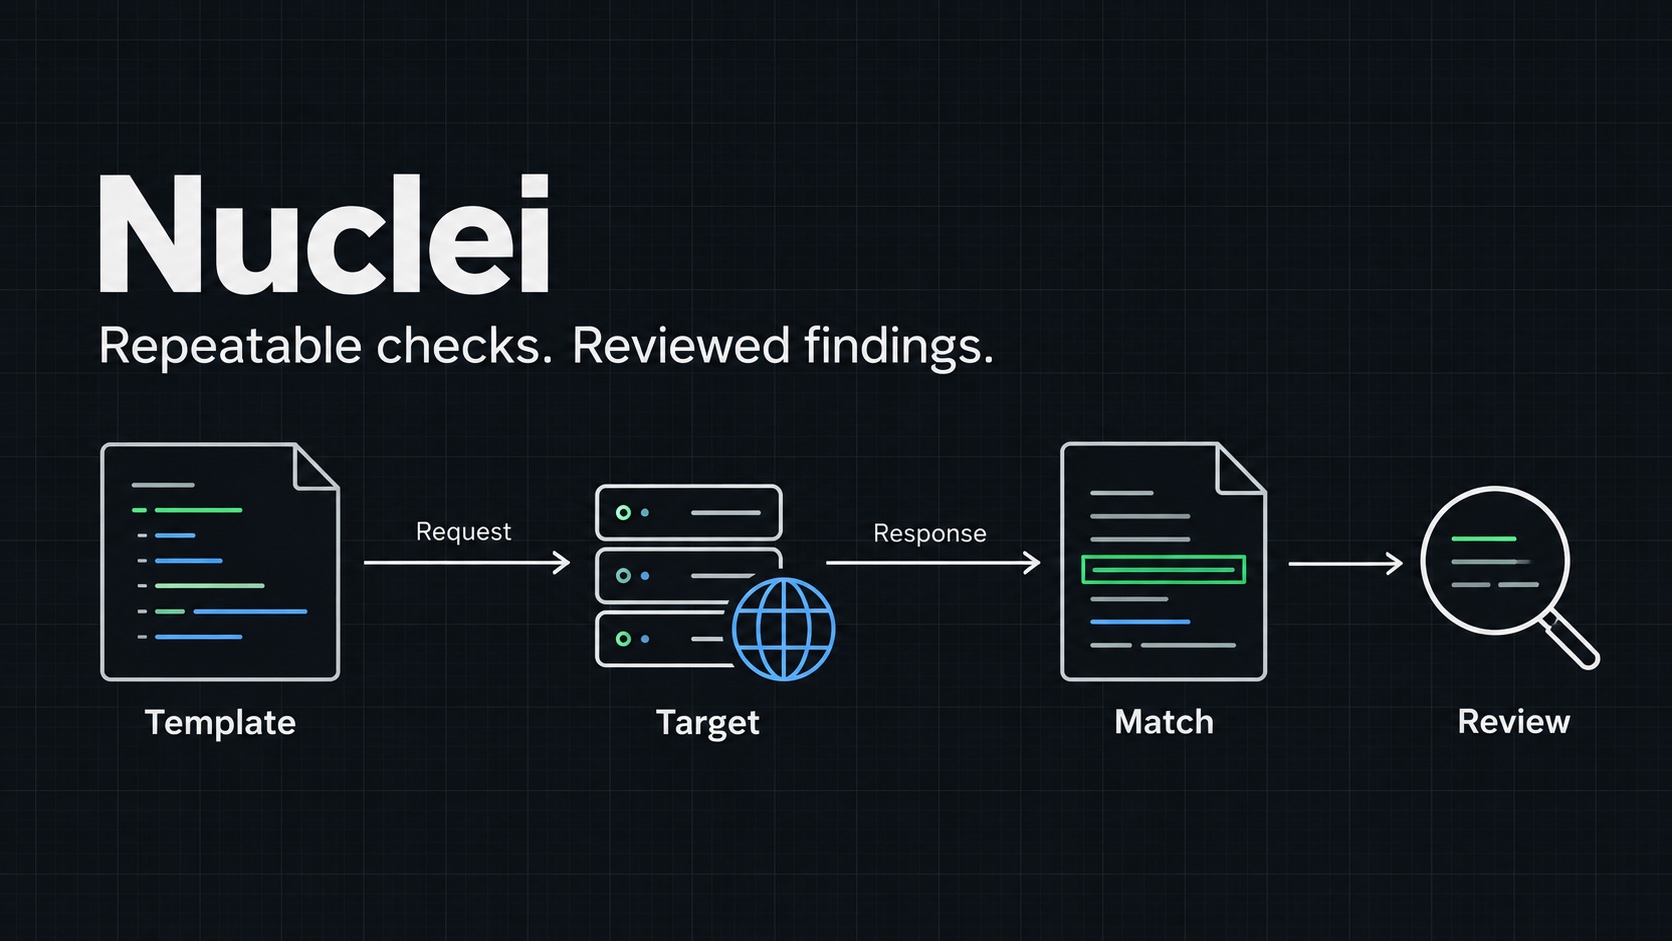
How I use Nuclei templates to run focused security checks, preserve evidence, and validate findings before reporting them.
How I use Frida to inspect Android TLS behaviour, distinguish UI changes from real bypasses, and trace selected Windows API calls.