Vulnerability
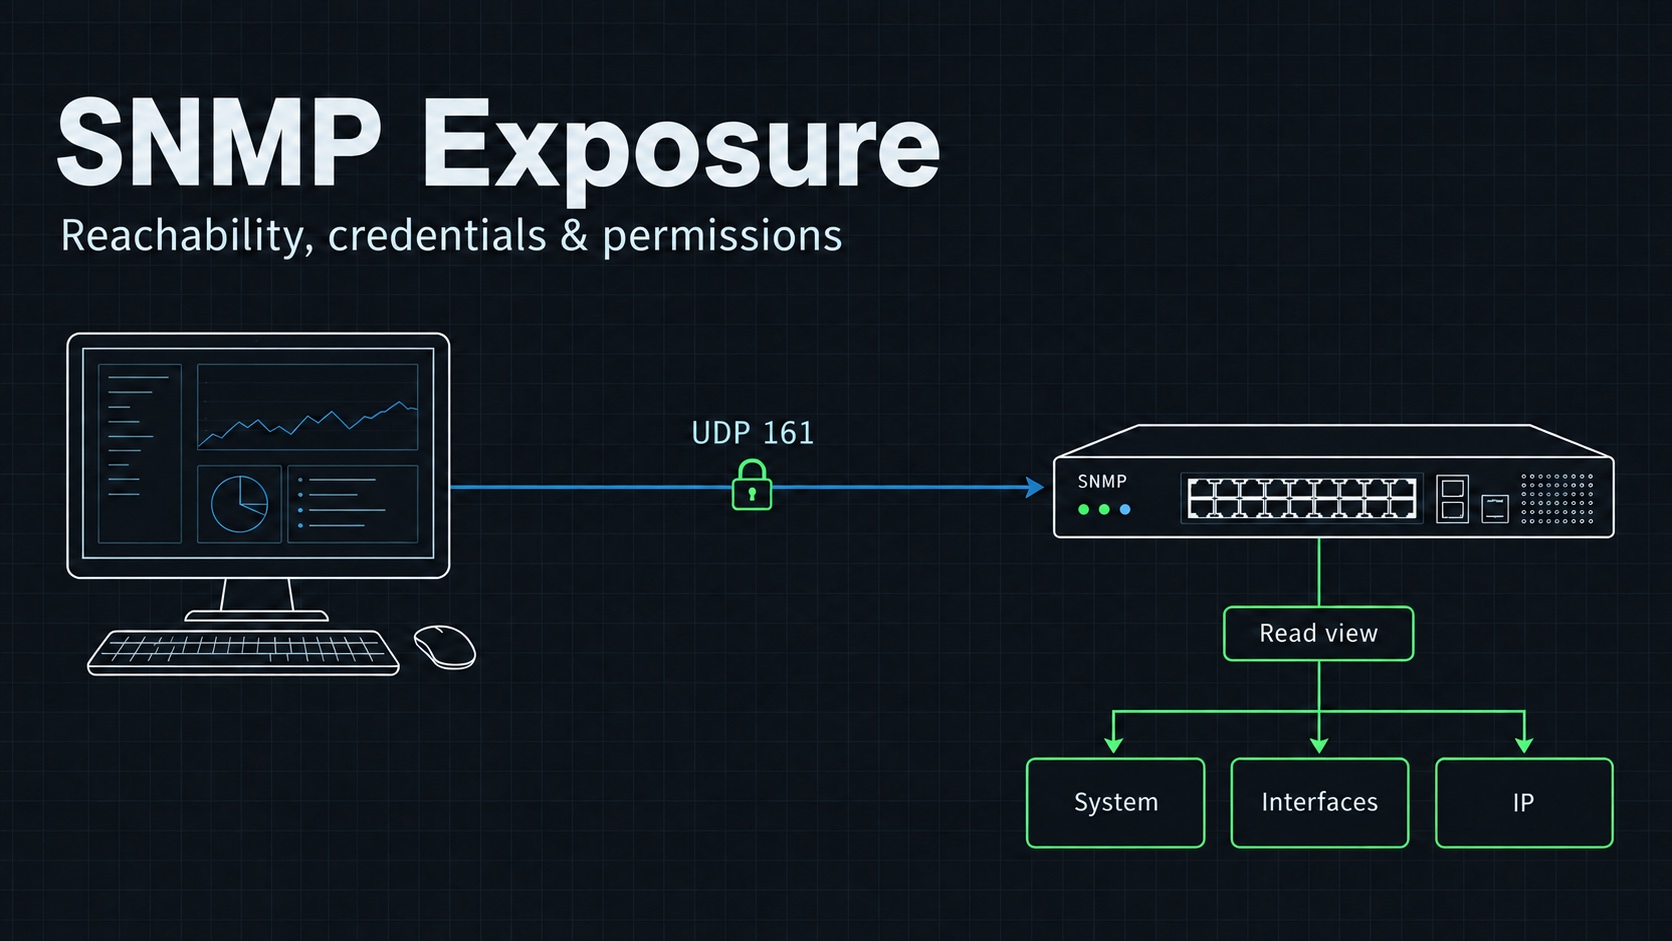
SNMP Exposure: Using Nmap and snmpwalk to Check Access
How I check SNMP exposure, interpret UDP scan results, and distinguish read access from dangerous management permissions.
How I check SNMP exposure, interpret UDP scan results, and distinguish read access from dangerous management permissions.
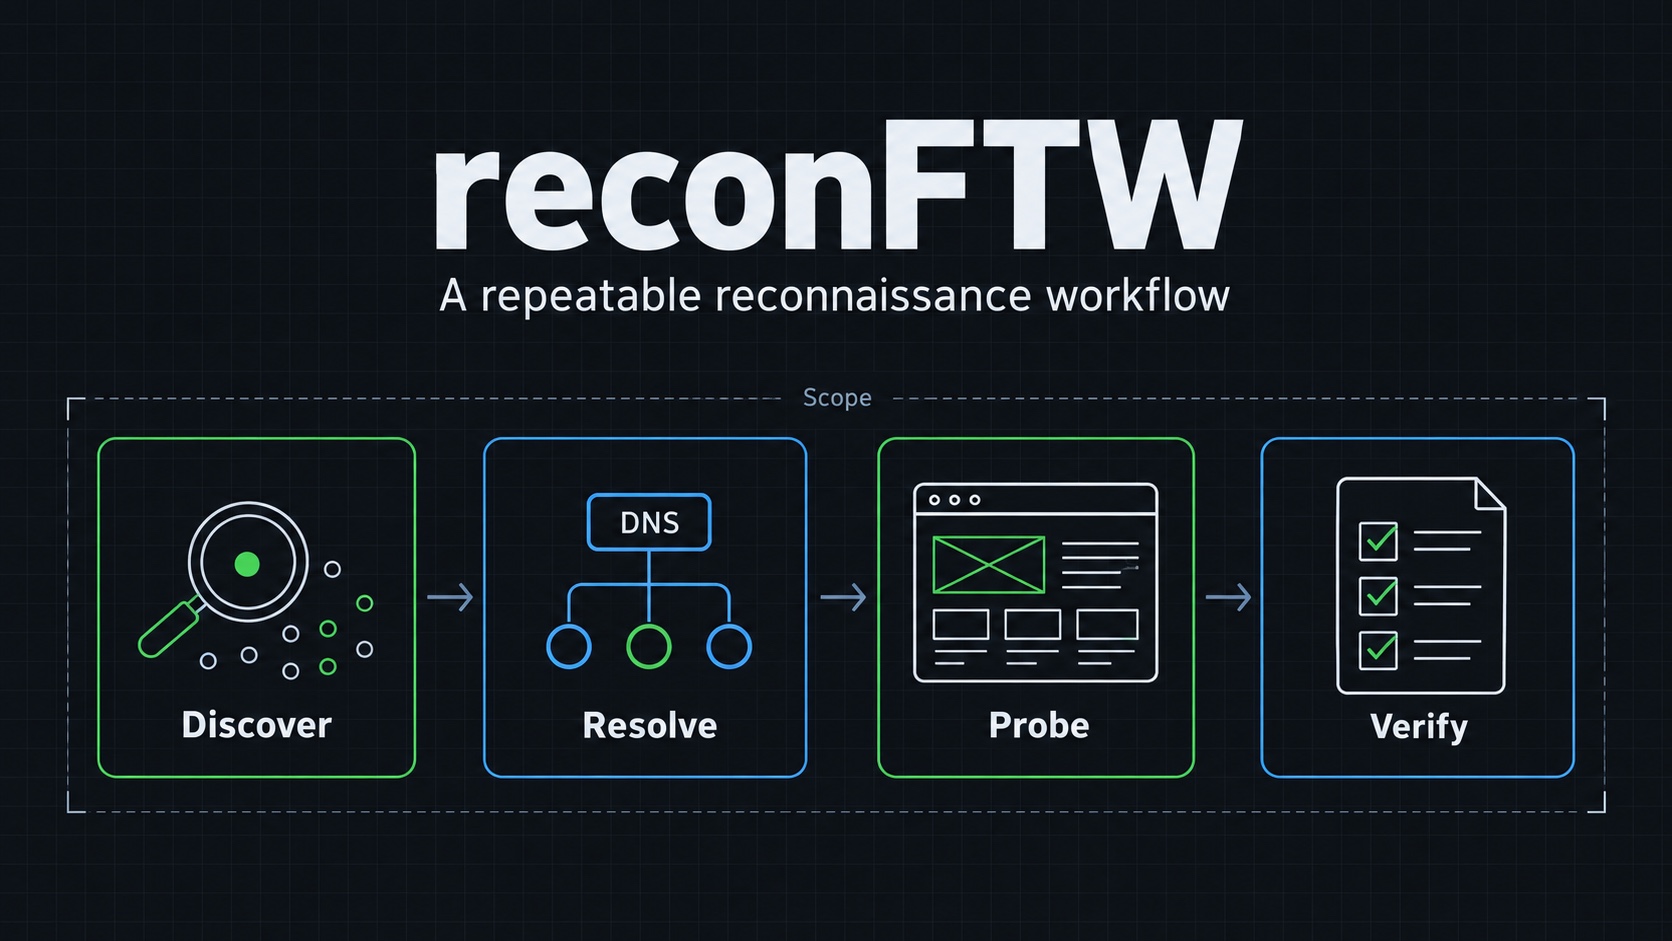
How I set up reconFTW, choose a bounded workflow, and turn collected reconnaissance data into findings I can verify.
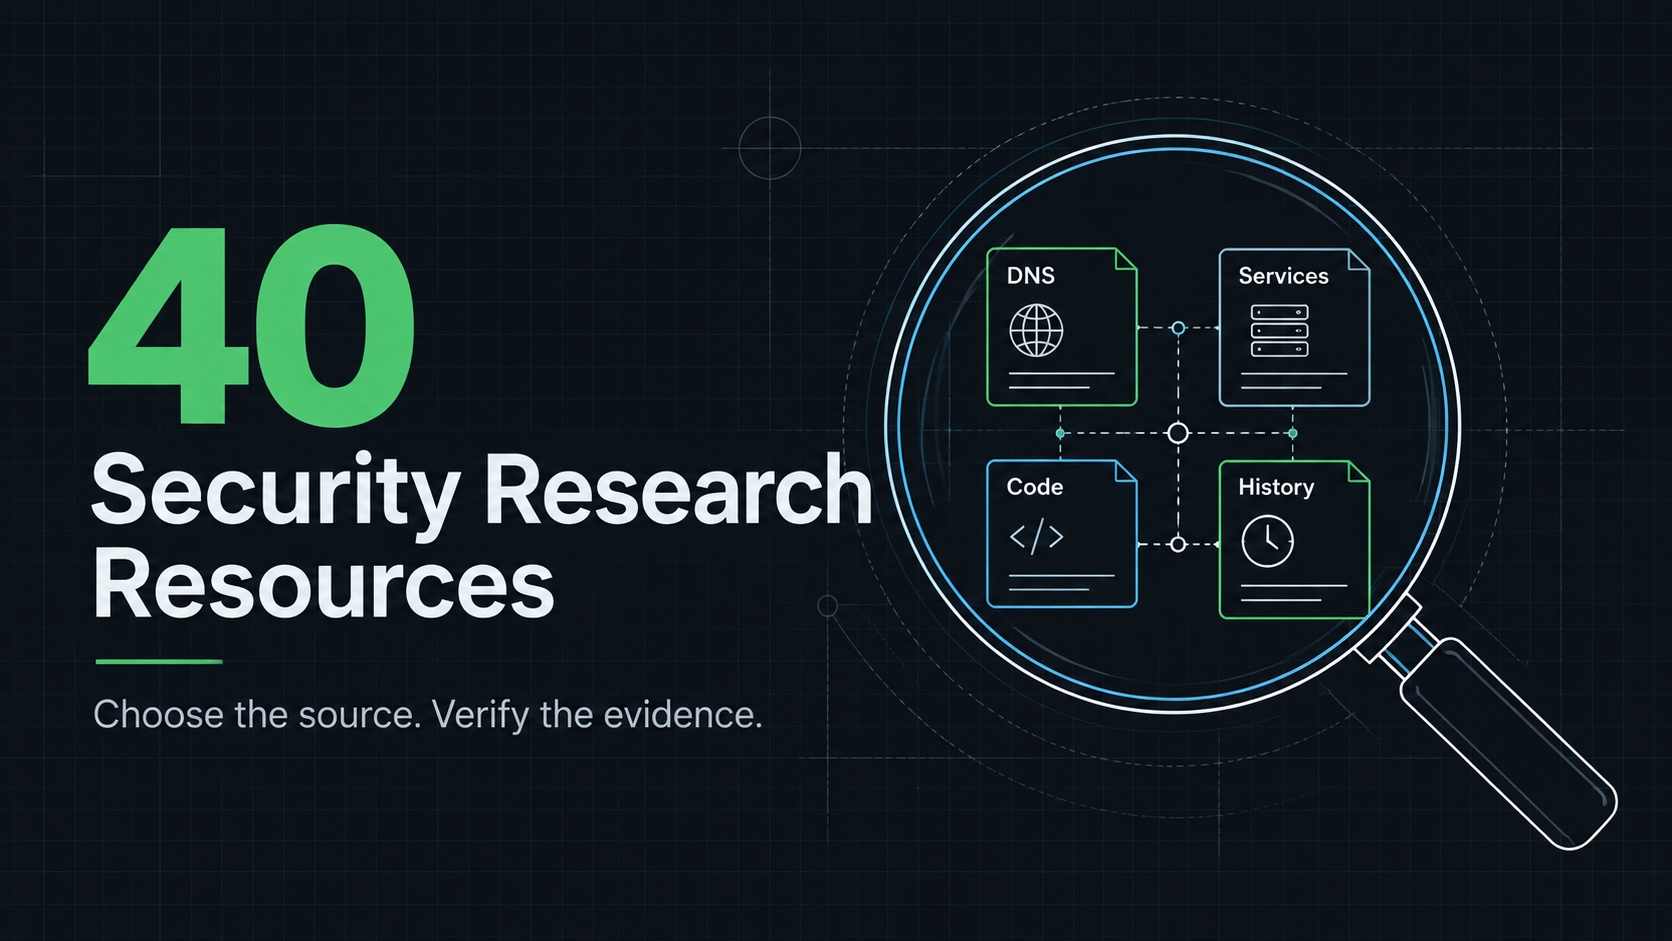
A practical directory for infrastructure research, threat intelligence, code search, and historical context, with corrections to older entries.
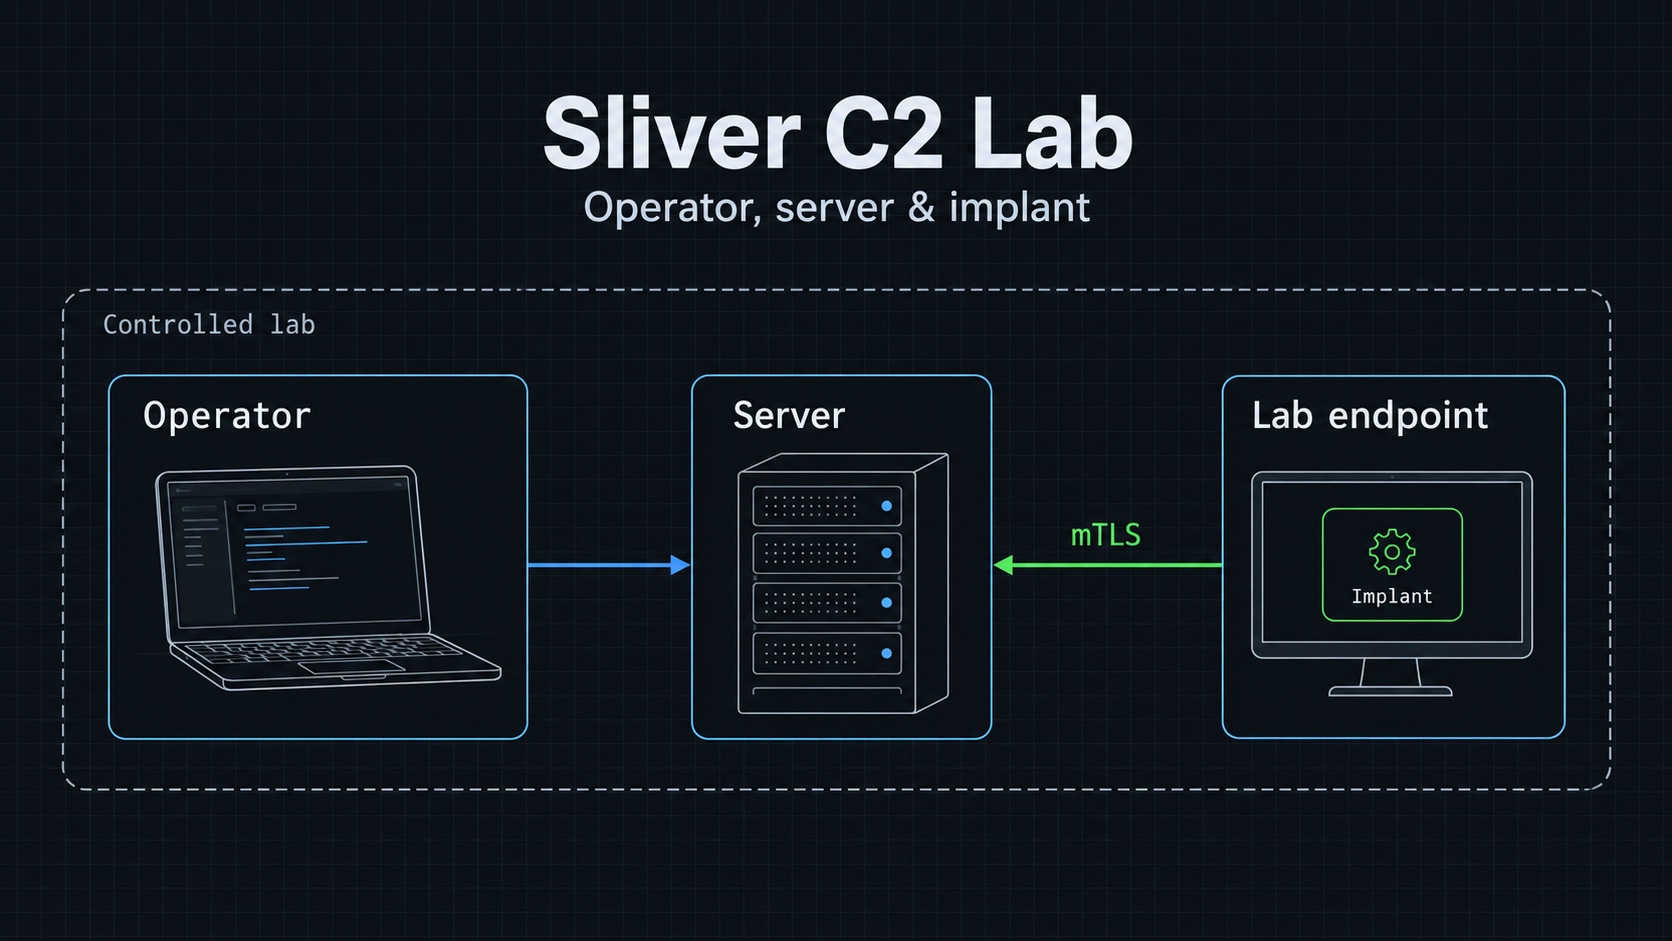
How I separate Sliver servers, operator clients, and implants, then build a bounded lab with evidence for each connection step.
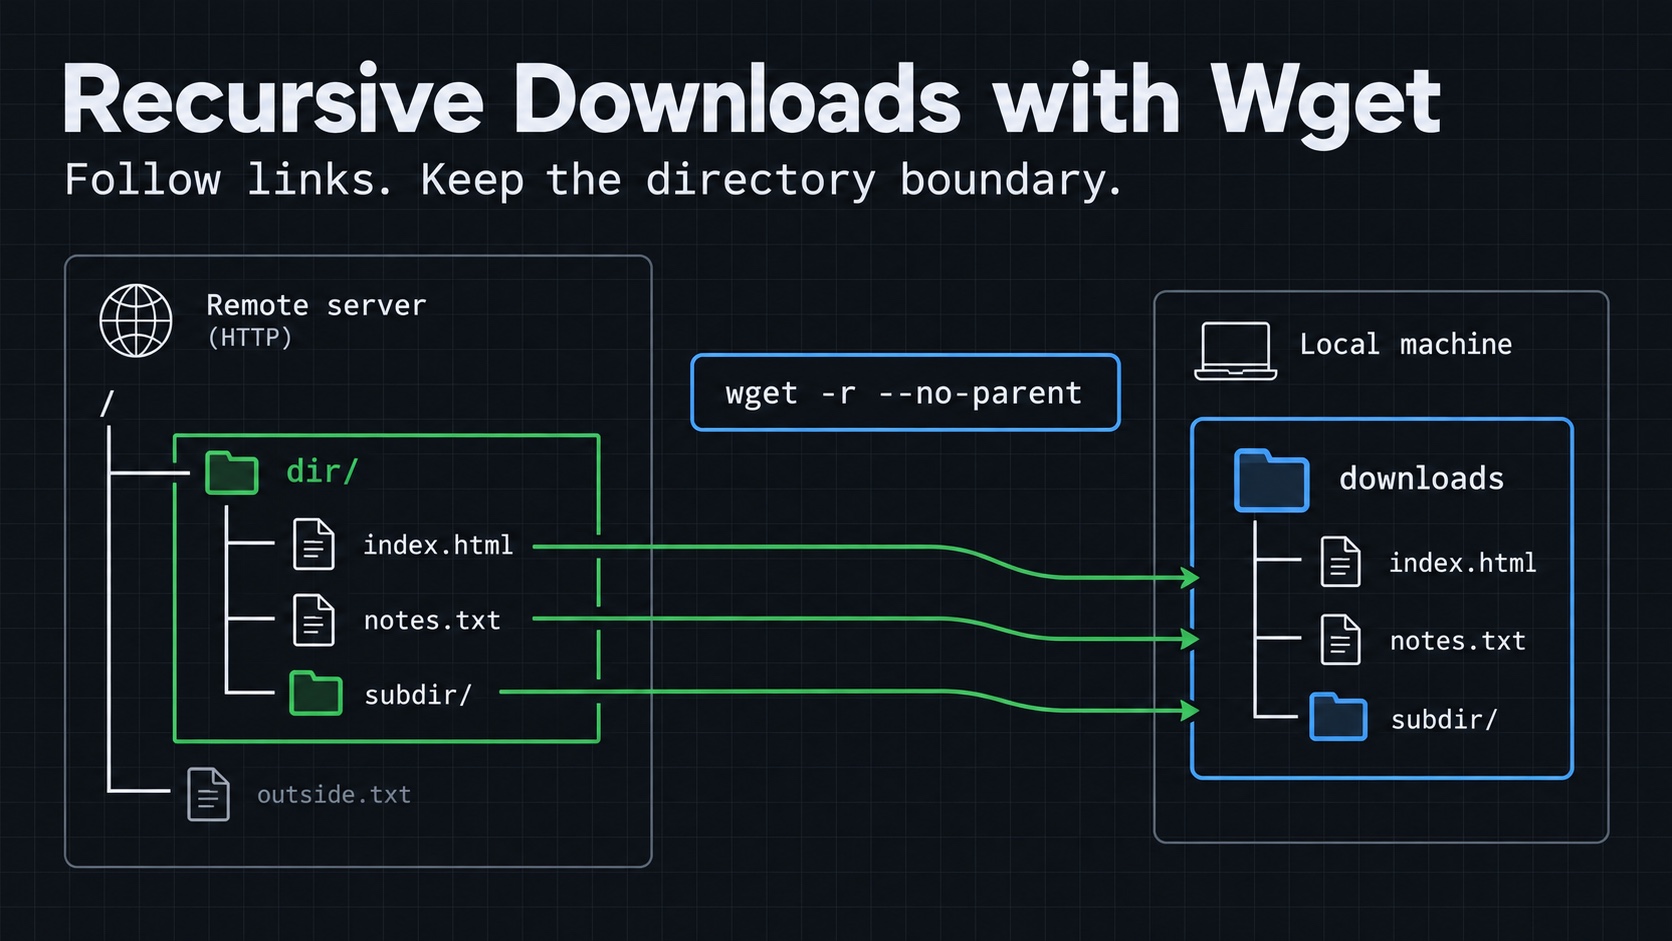
How I use Wget to download linked files under a web directory, control recursion, and check what was saved.
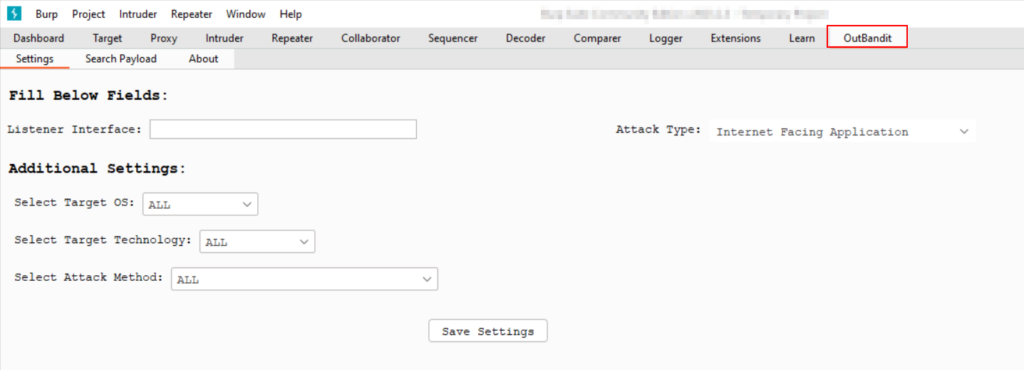
Why I built OutBandit for Burp Suite, how I approach callback testing, and what an HTTP or DNS interaction can actually prove.
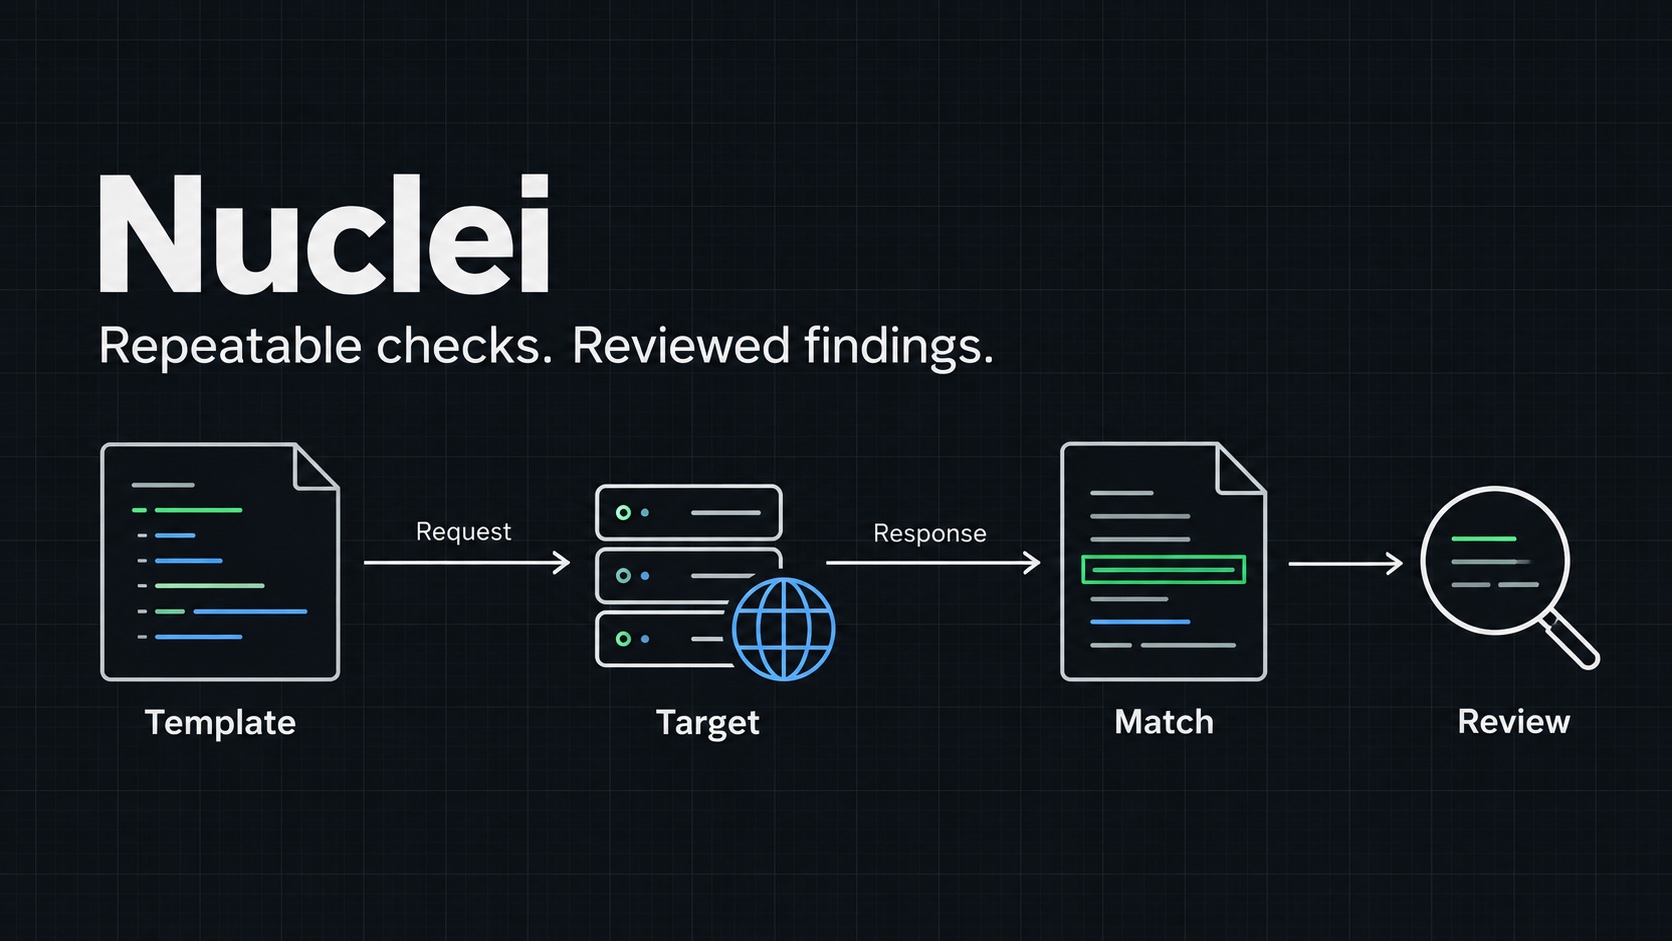
How I use Nuclei templates to run focused security checks, preserve evidence, and validate findings before reporting them.
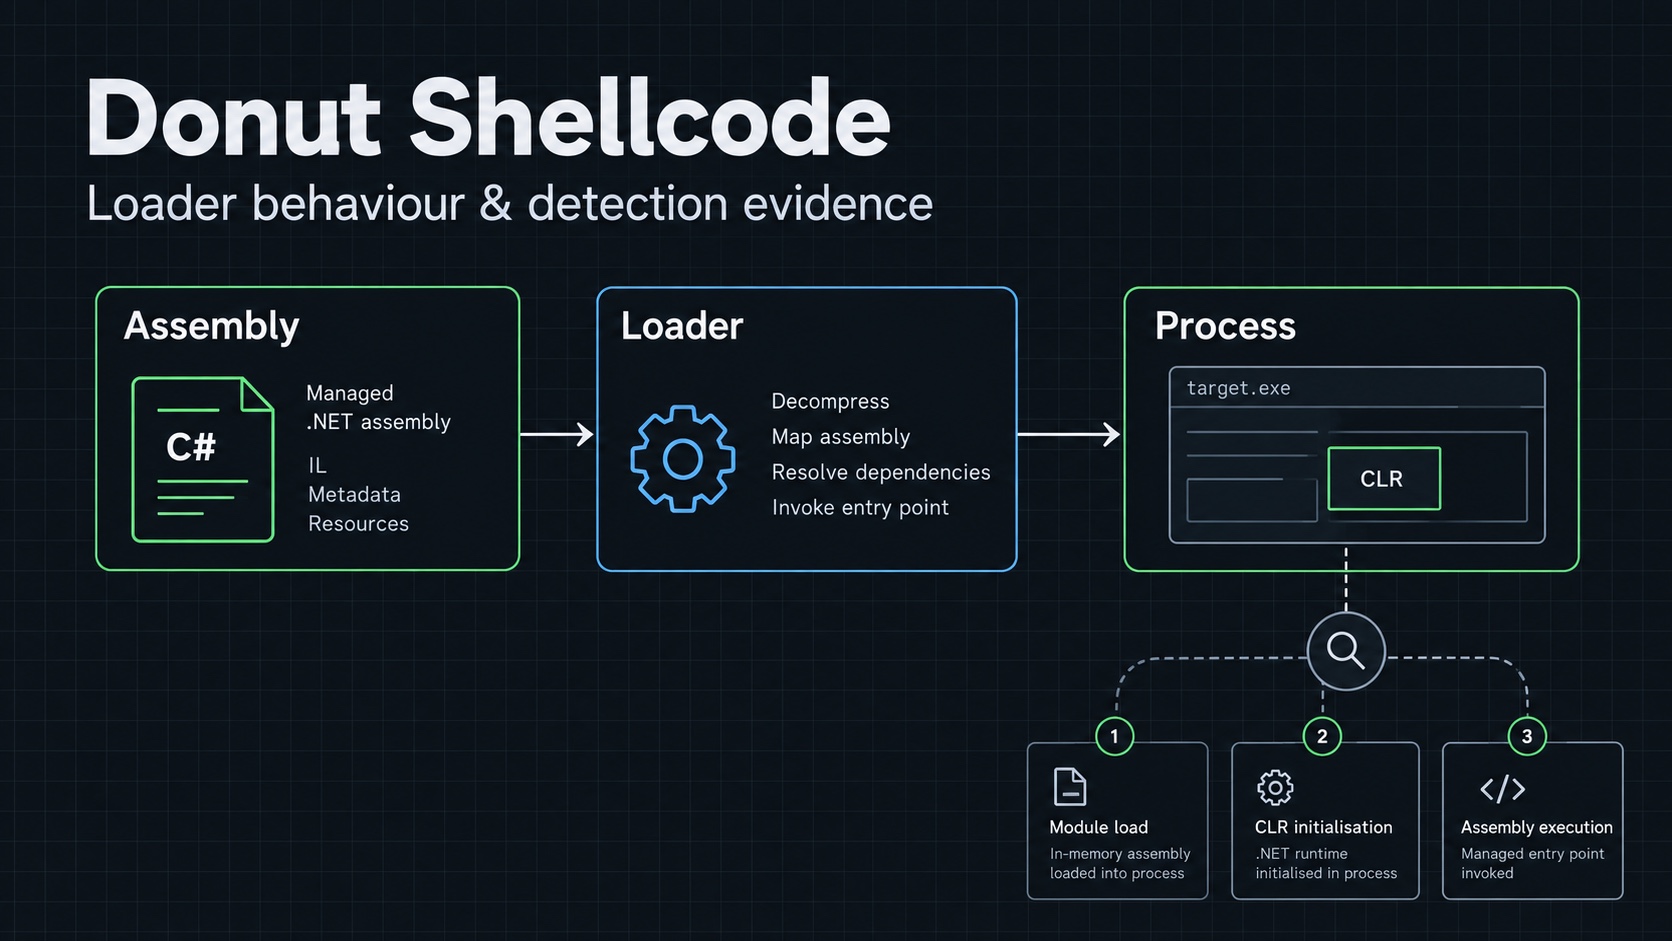
What Donut generates, how its managed-code loader works, and the evidence I need before describing any endpoint protection bypass.
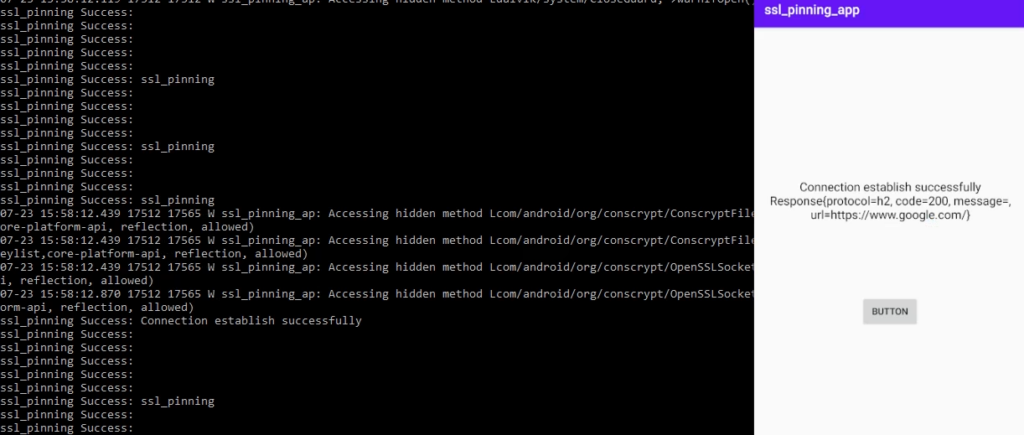
How I use Frida to inspect Android TLS behaviour, distinguish UI changes from real bypasses, and trace selected Windows API calls.