Tools and Scripting
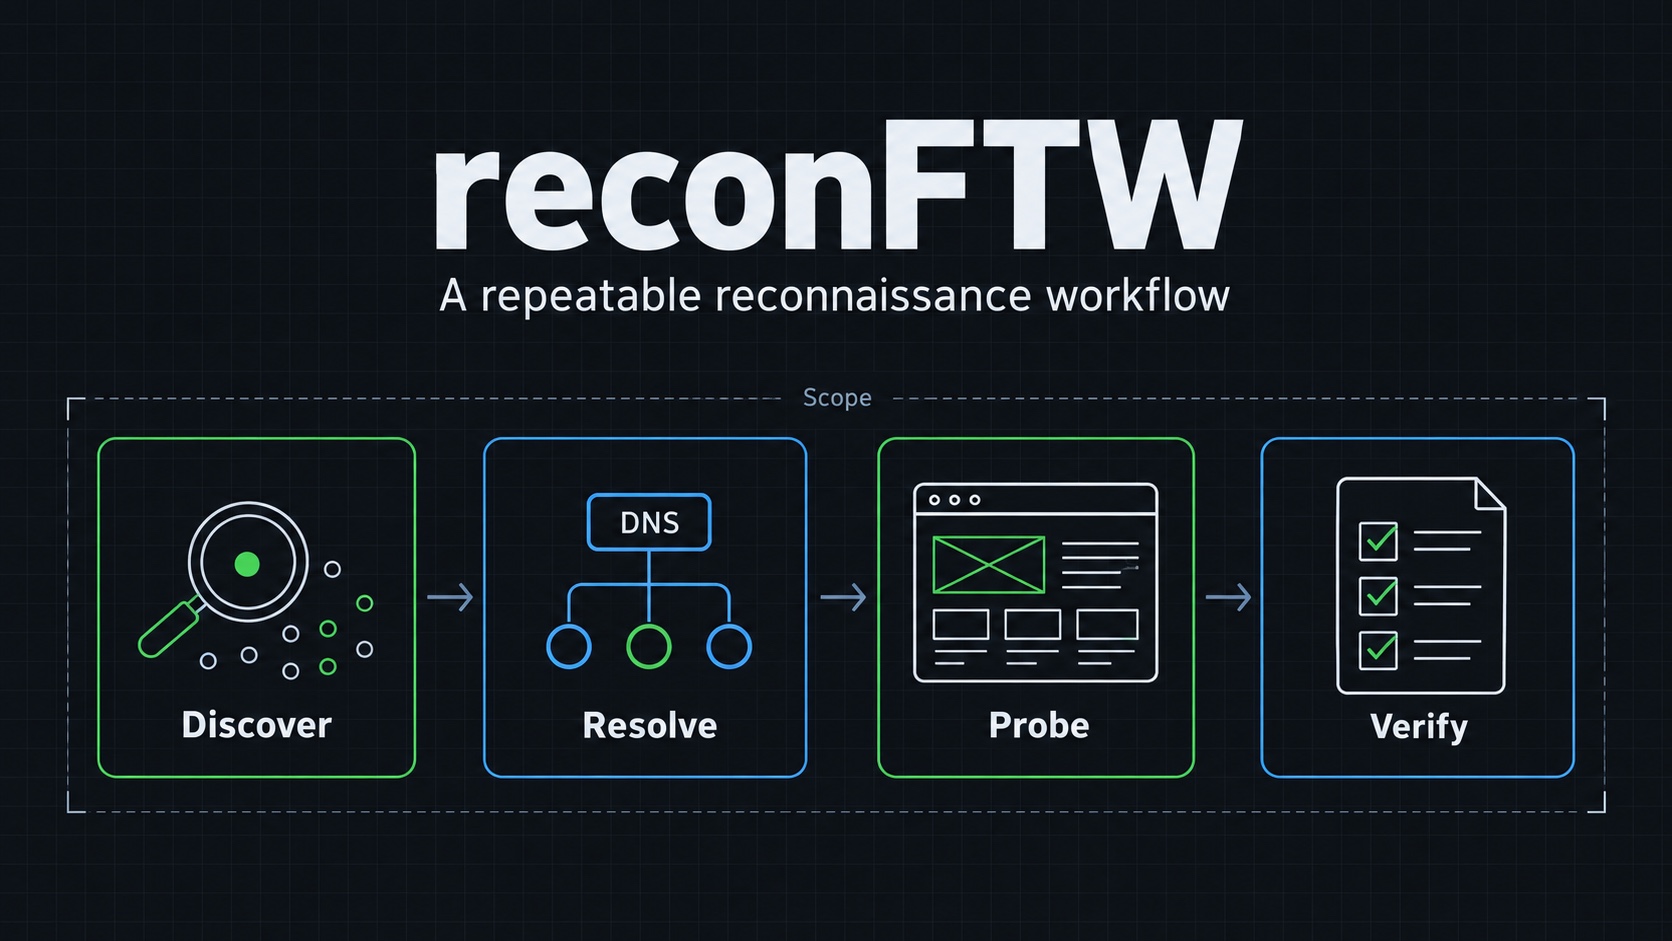
reconFTW: Building a Repeatable Reconnaissance Workflow
How I set up reconFTW, choose a bounded workflow, and turn collected reconnaissance data into findings I can verify.
How I set up reconFTW, choose a bounded workflow, and turn collected reconnaissance data into findings I can verify.
How I use shared analytics identifiers as OSINT leads, account for historical data, and avoid treating a common tag as proof of ownership.
A practical directory for infrastructure research, threat intelligence, code search, and historical context, with corrections to older entries.