Vulnerability
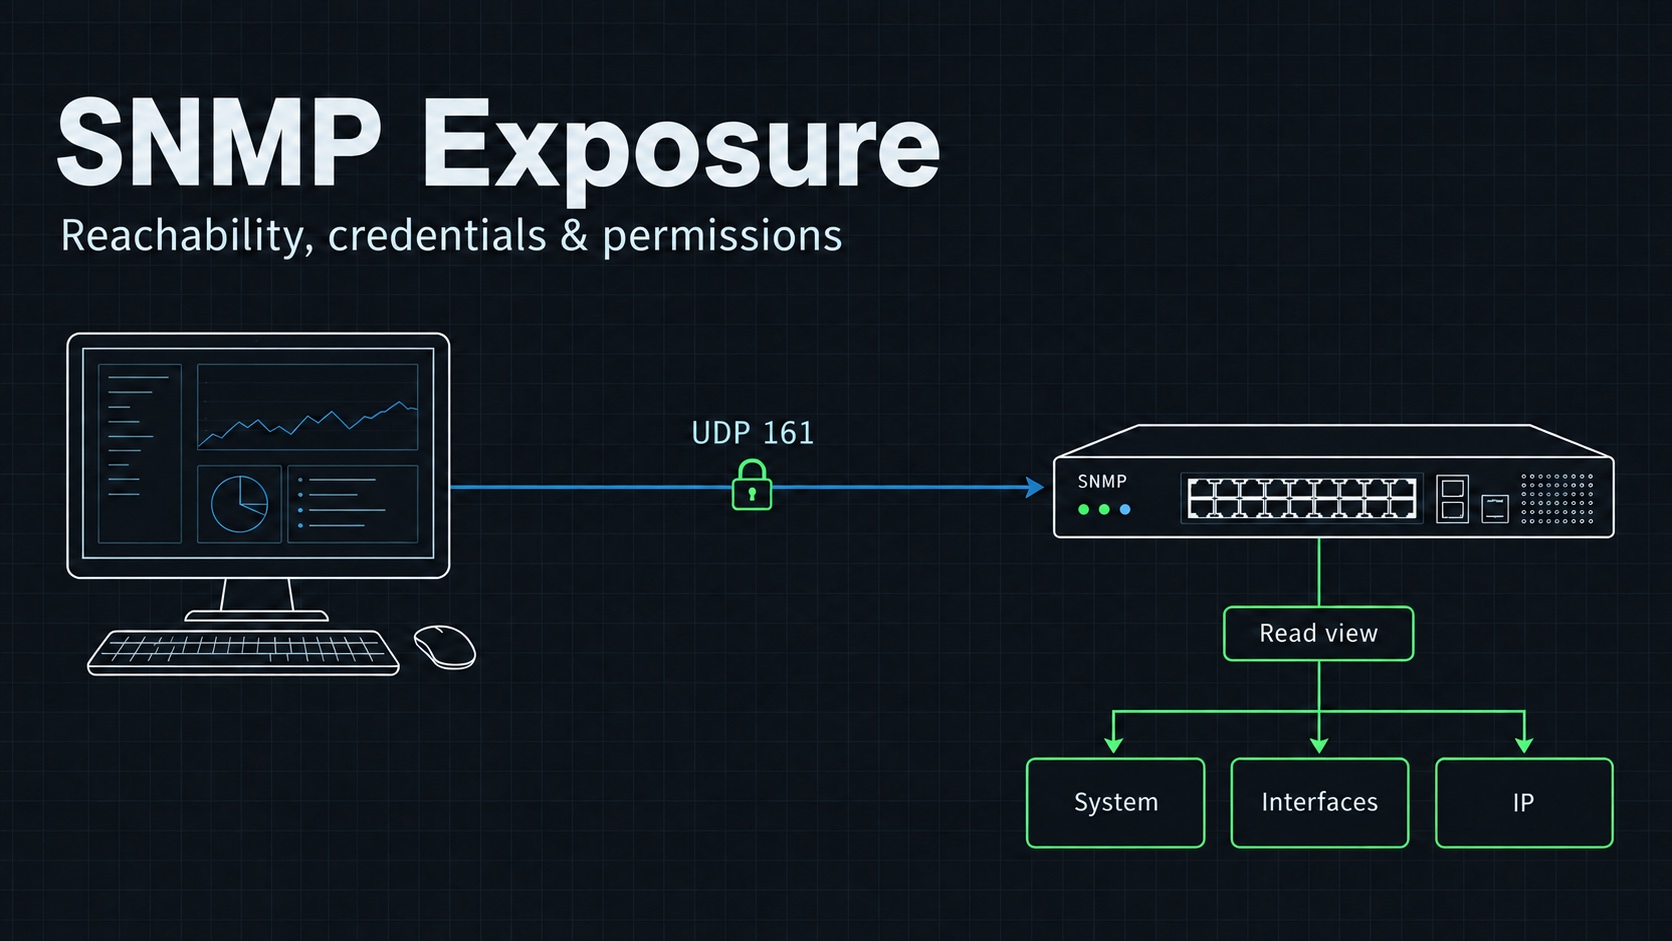
SNMP Exposure: Using Nmap and snmpwalk to Check Access
How I check SNMP exposure, interpret UDP scan results, and distinguish read access from dangerous management permissions.
How I check SNMP exposure, interpret UDP scan results, and distinguish read access from dangerous management permissions.
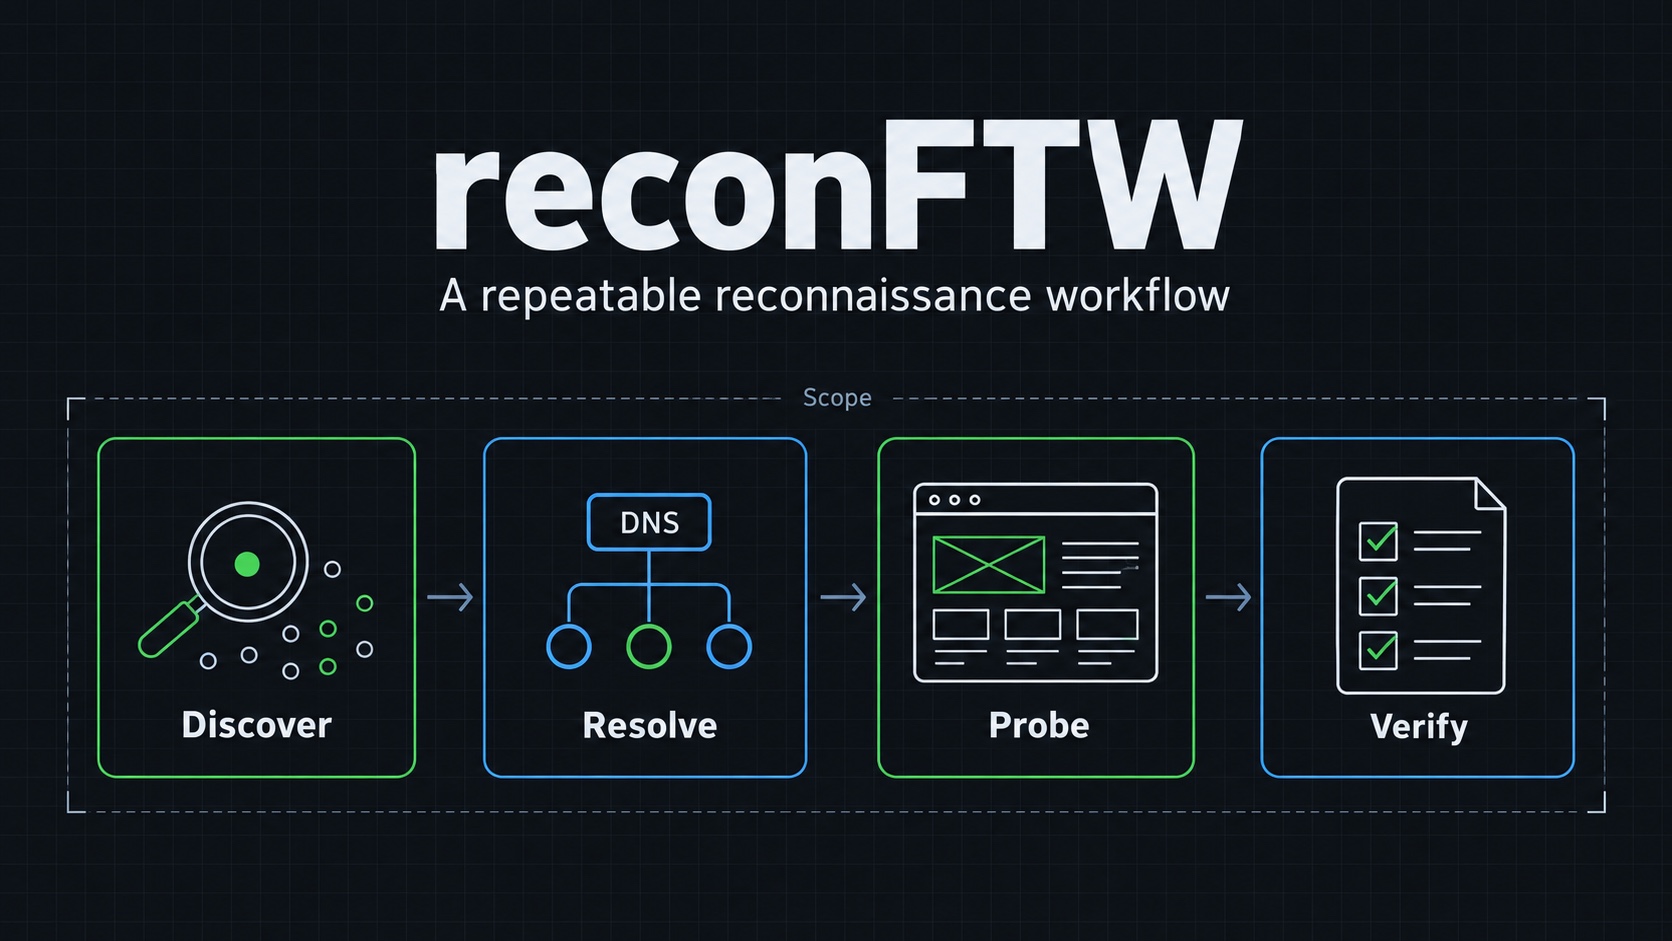
How I set up reconFTW, choose a bounded workflow, and turn collected reconnaissance data into findings I can verify.
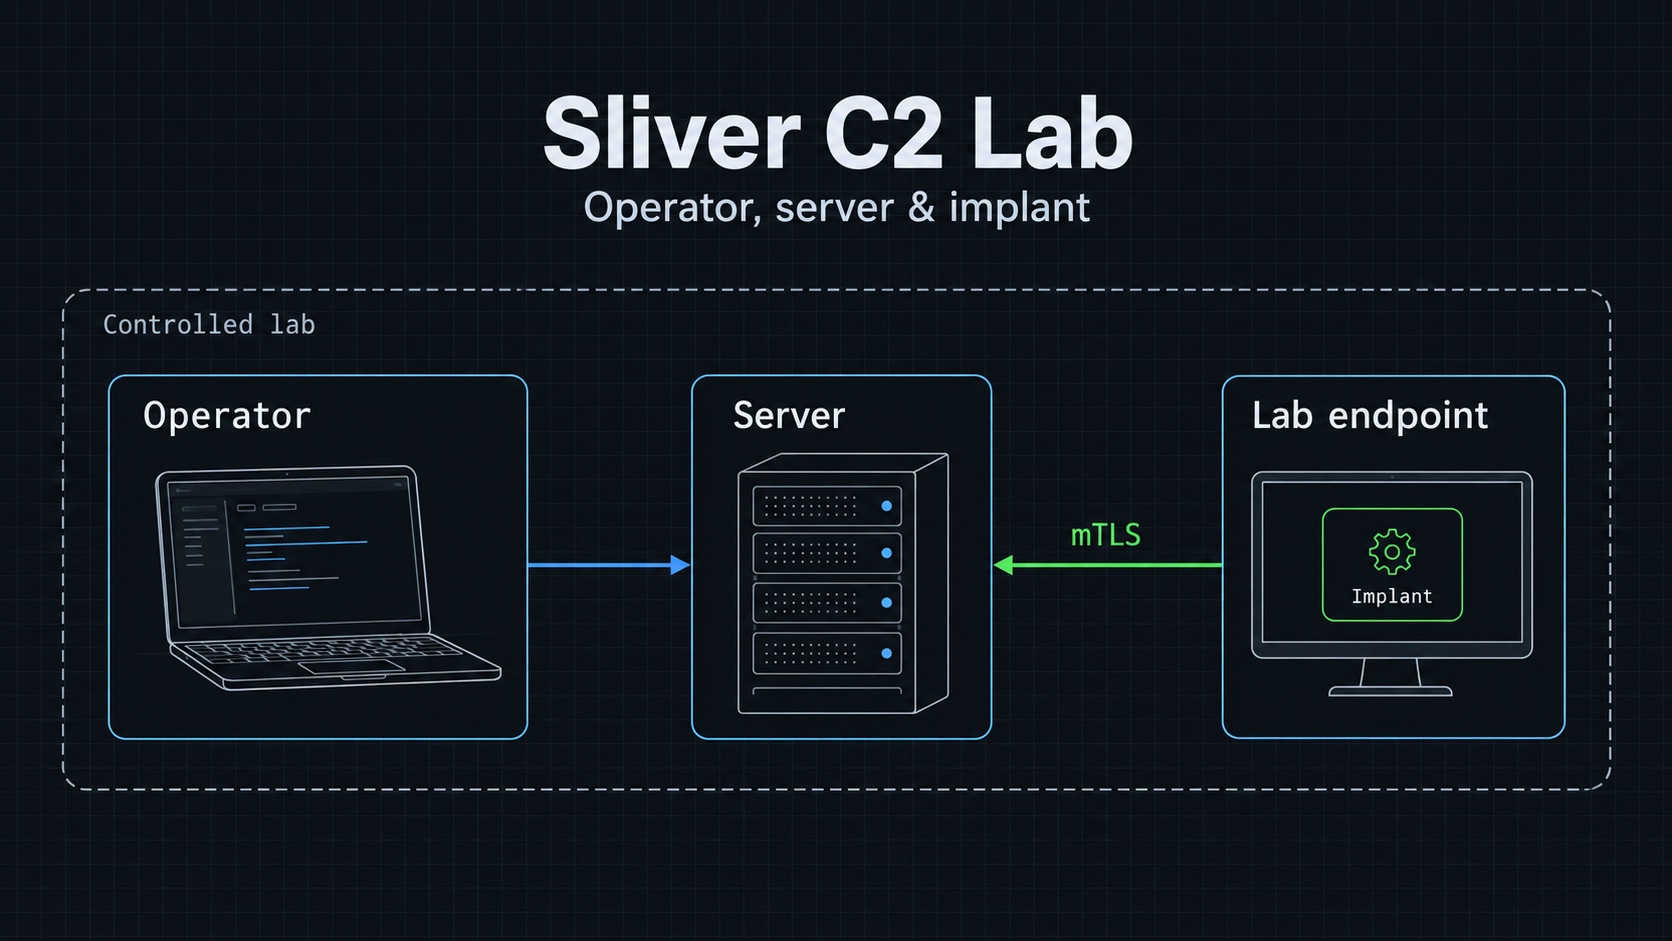
How I separate Sliver servers, operator clients, and implants, then build a bounded lab with evidence for each connection step.
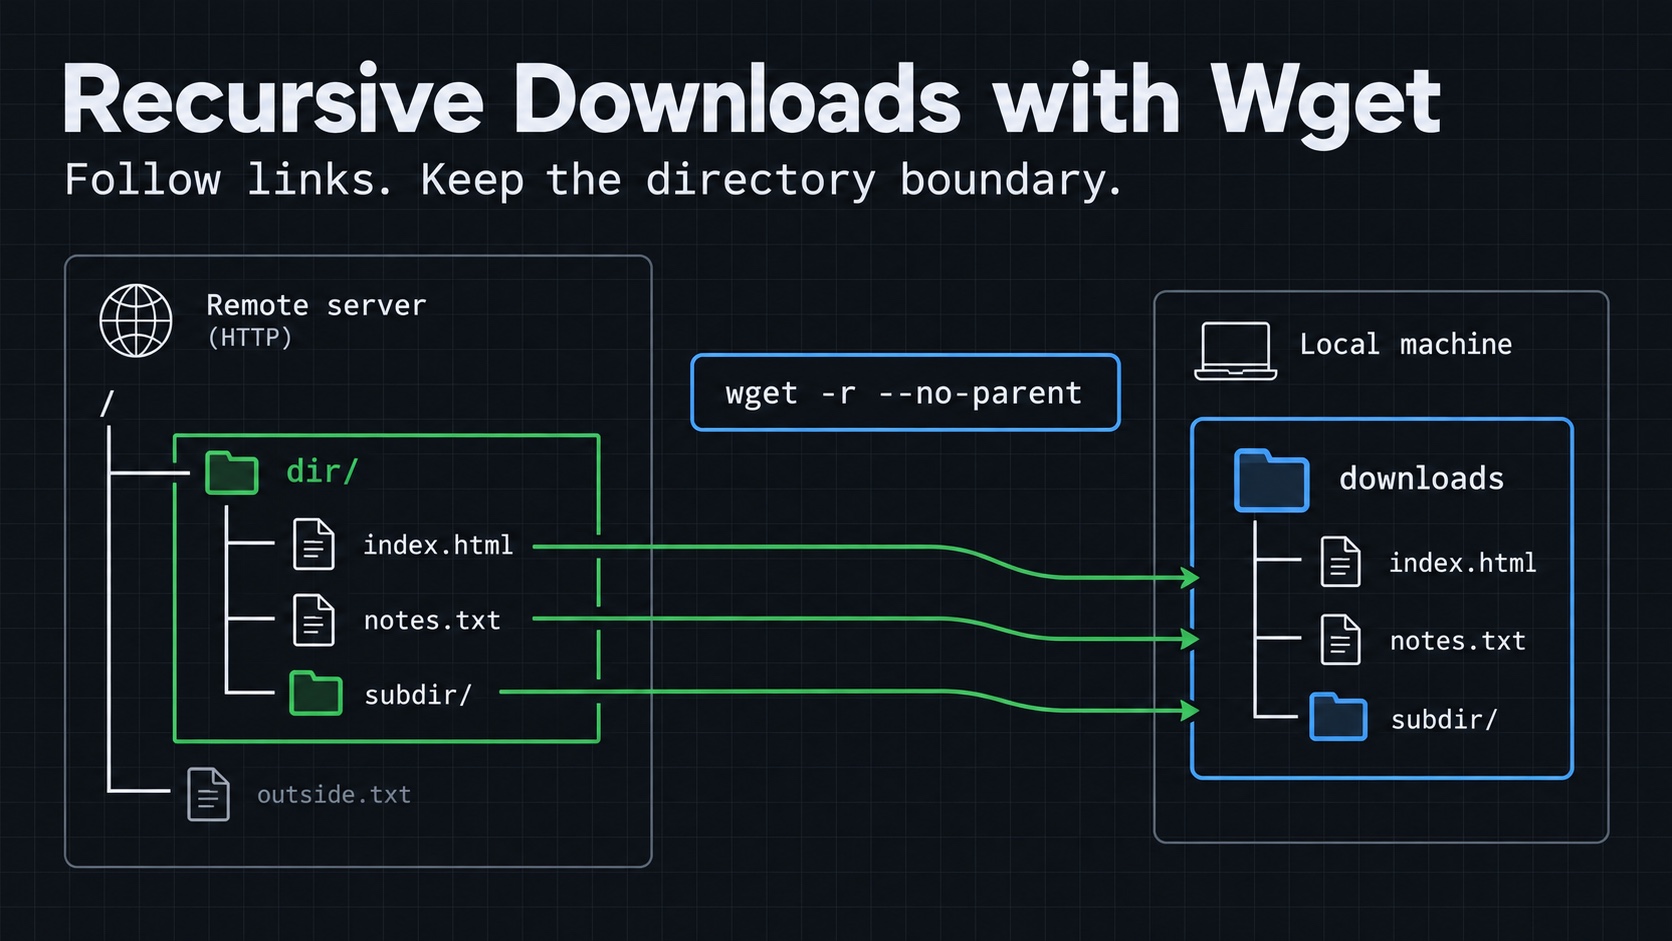
How I use Wget to download linked files under a web directory, control recursion, and check what was saved.
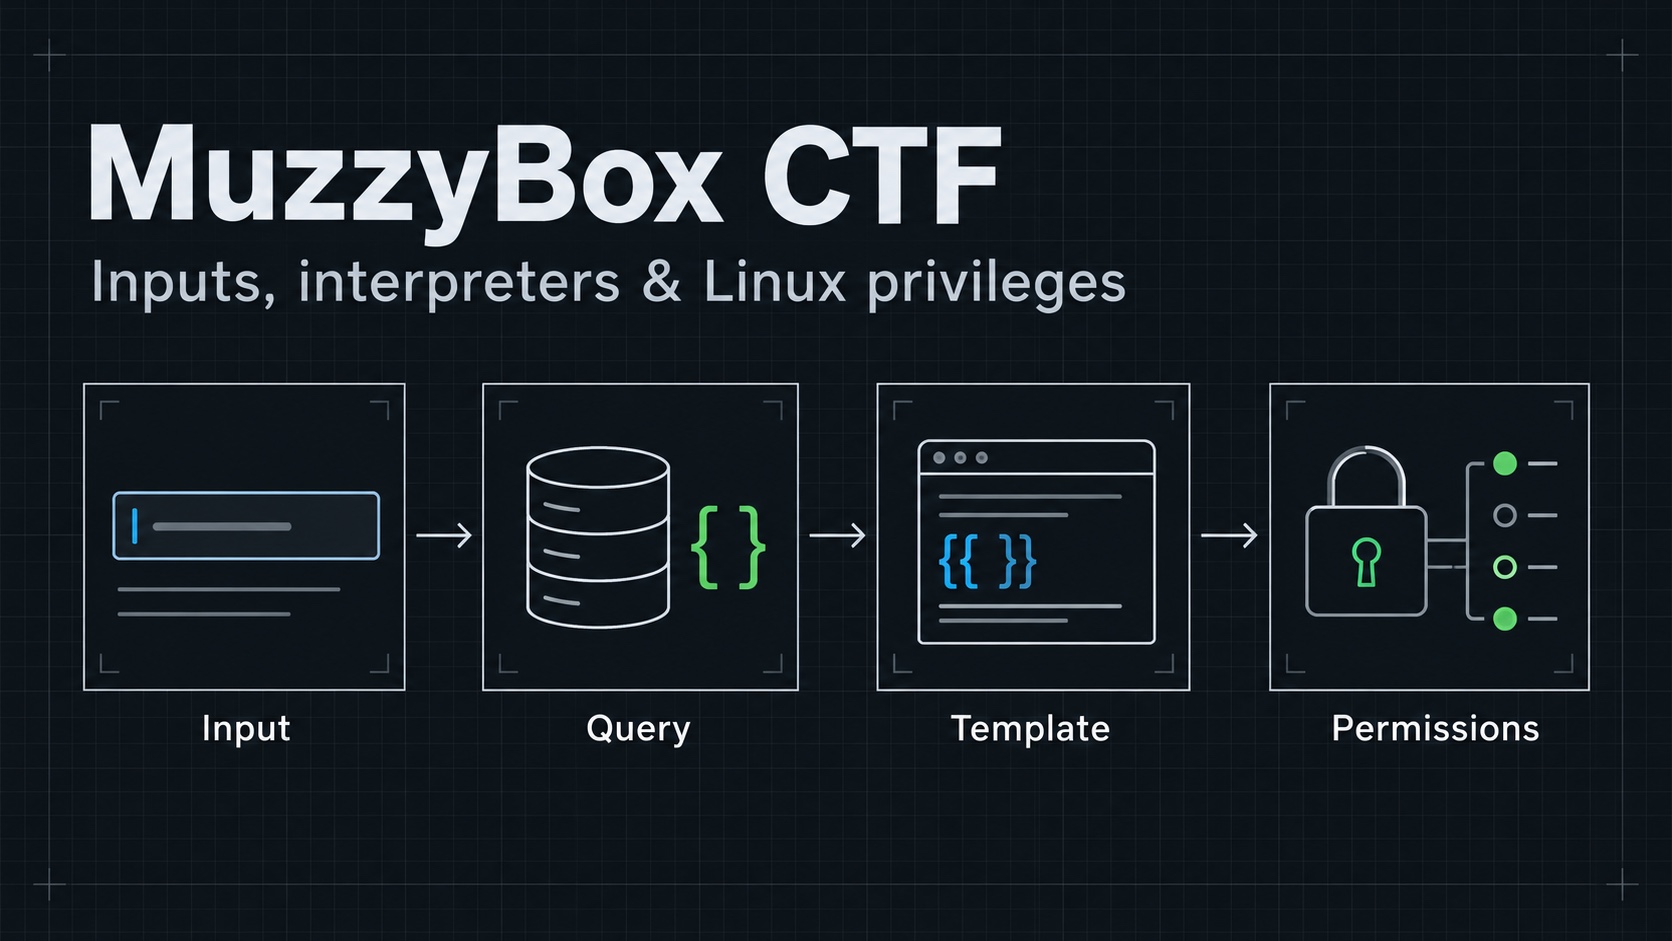
An introduction to my MuzzyBox CTF and the questions I use to investigate NoSQL injection, Python evaluation, SSTI, and Linux escalation.