Vulnerability
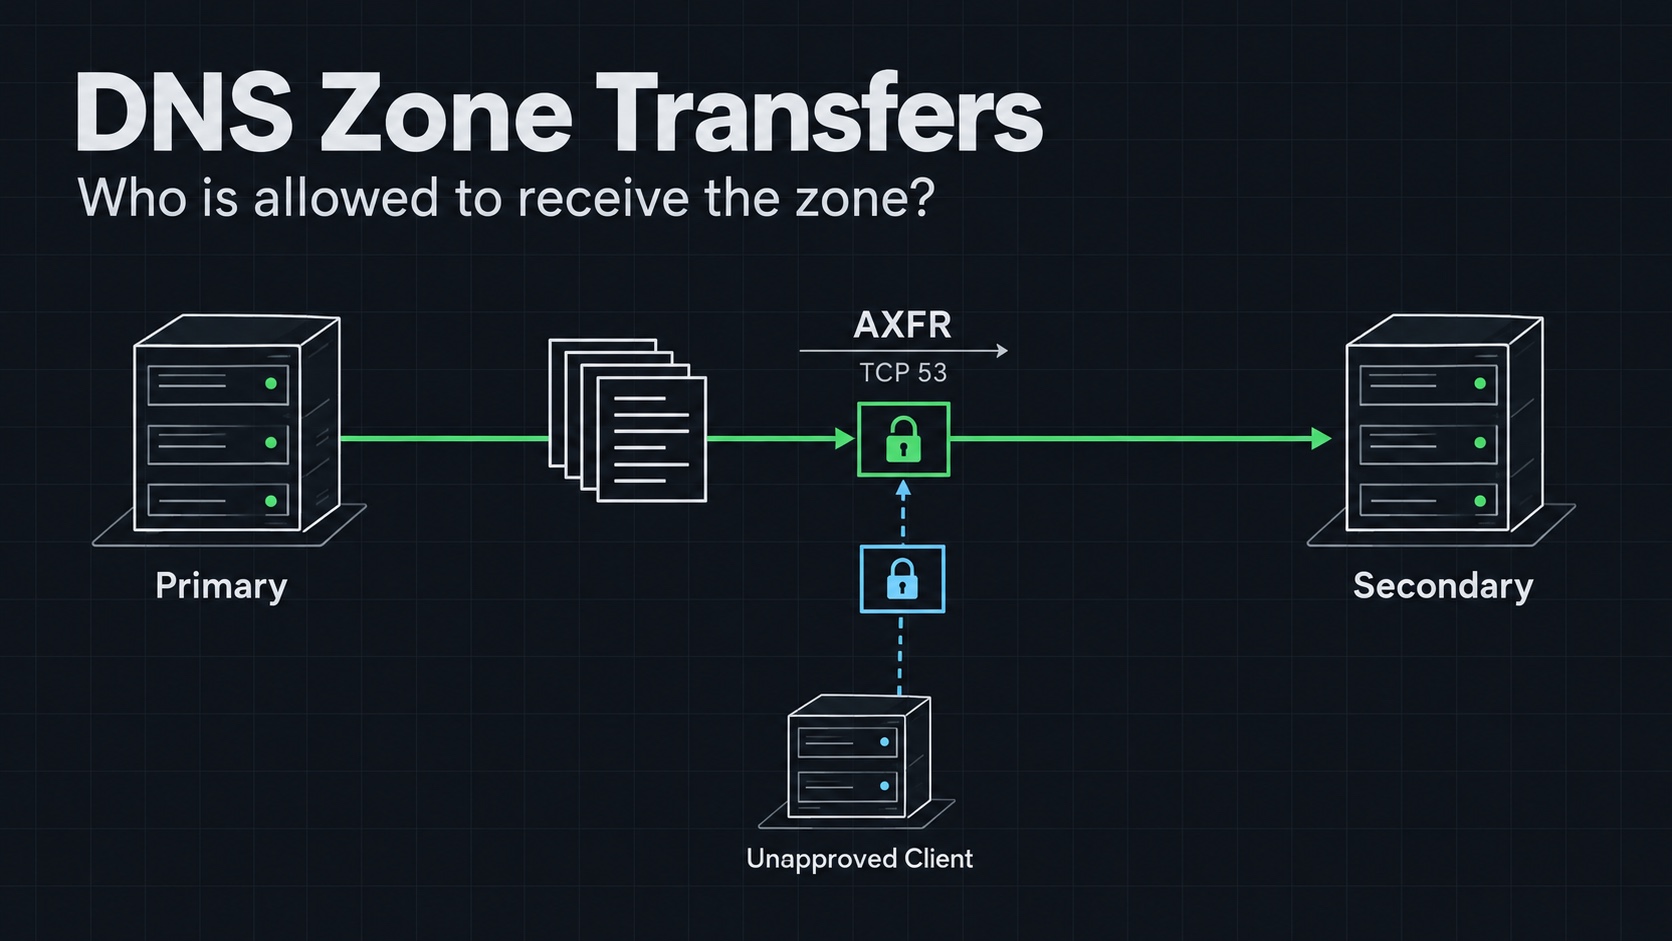
DNS Zone Transfers: Finding and Fixing Unrestricted AXFR
How I test DNS zone-transfer permissions, interpret the response, and restrict transfers without breaking secondary DNS servers.
How I test DNS zone-transfer permissions, interpret the response, and restrict transfers without breaking secondary DNS servers.
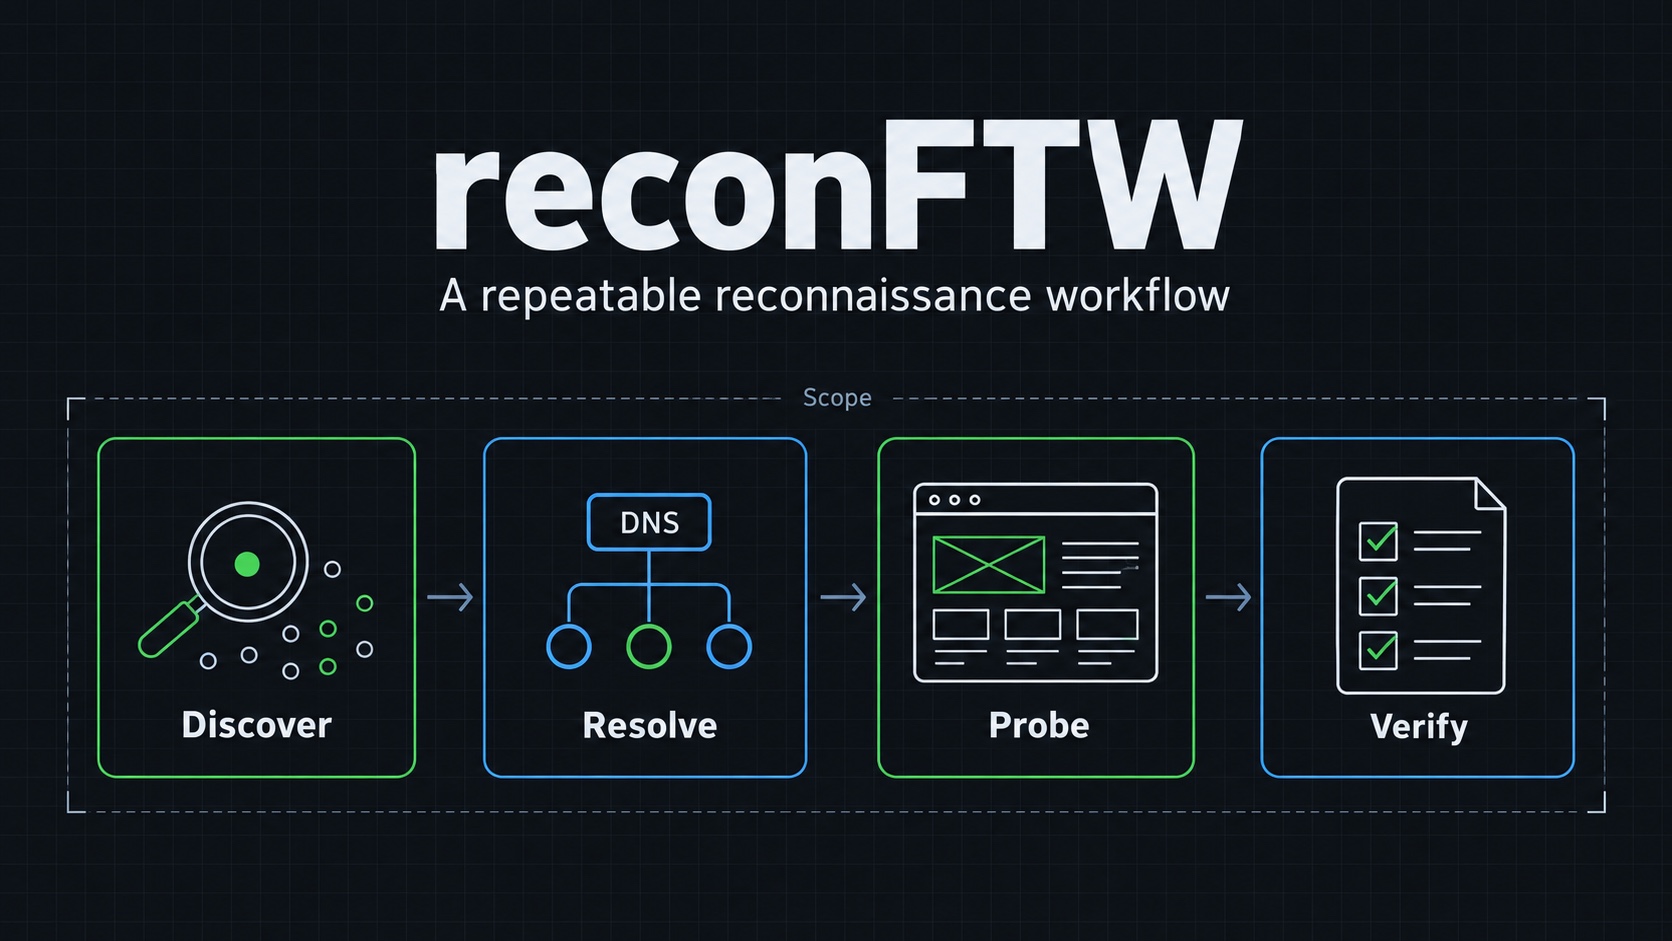
How I set up reconFTW, choose a bounded workflow, and turn collected reconnaissance data into findings I can verify.
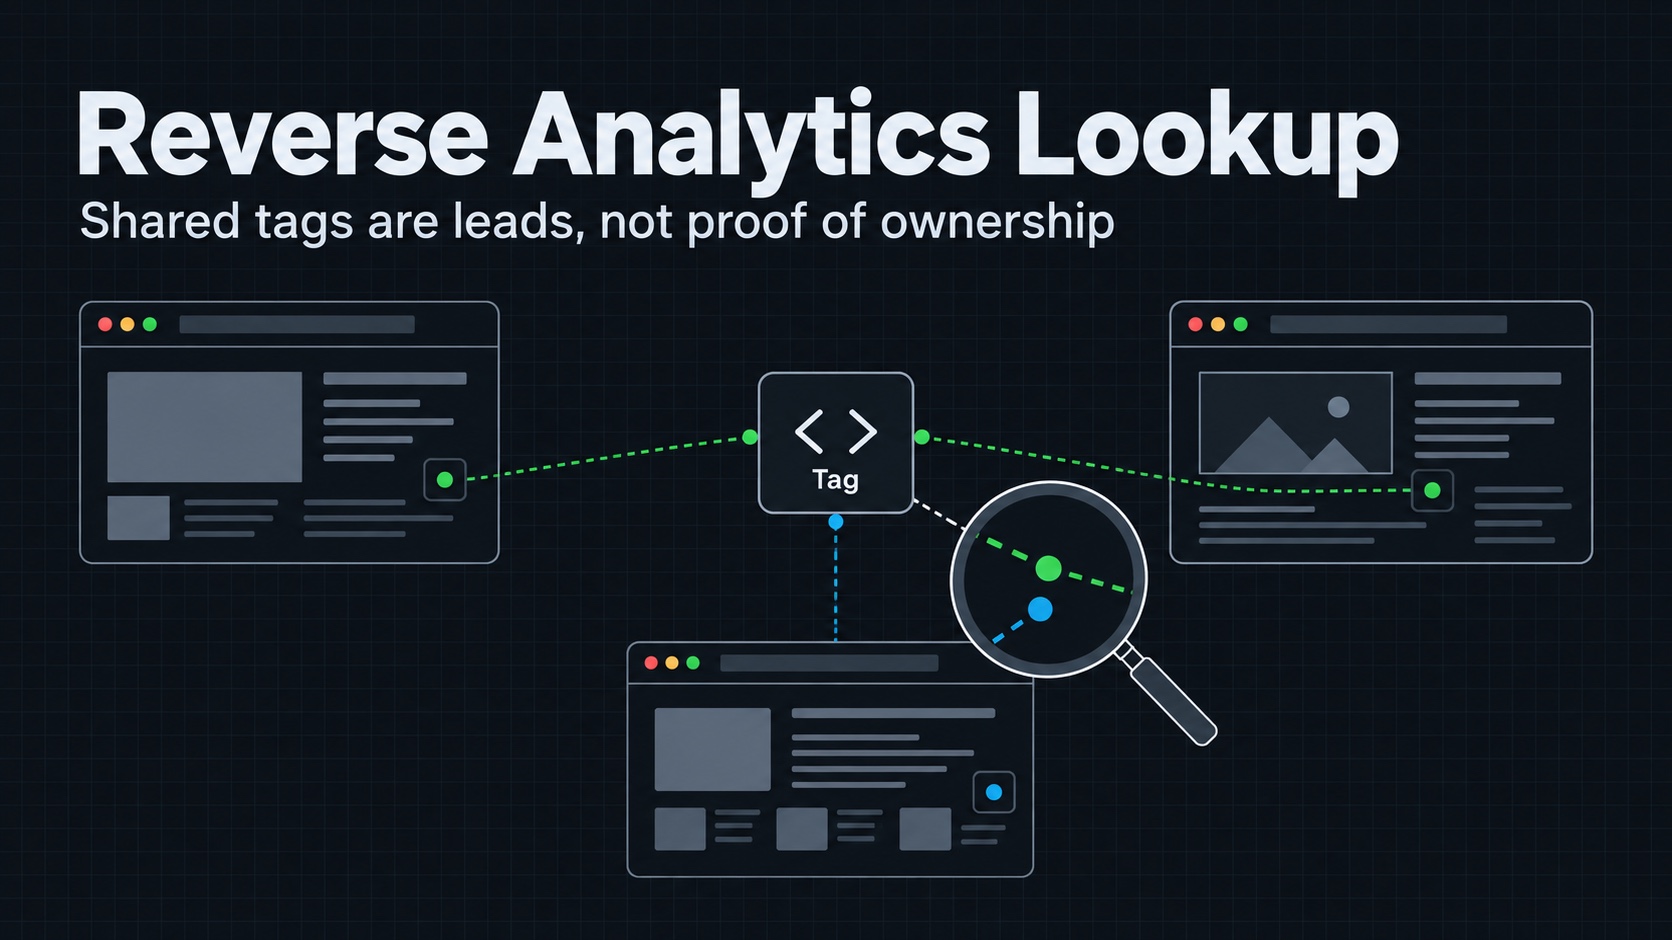
How I use shared analytics identifiers as OSINT leads, account for historical data, and avoid treating a common tag as proof of ownership.
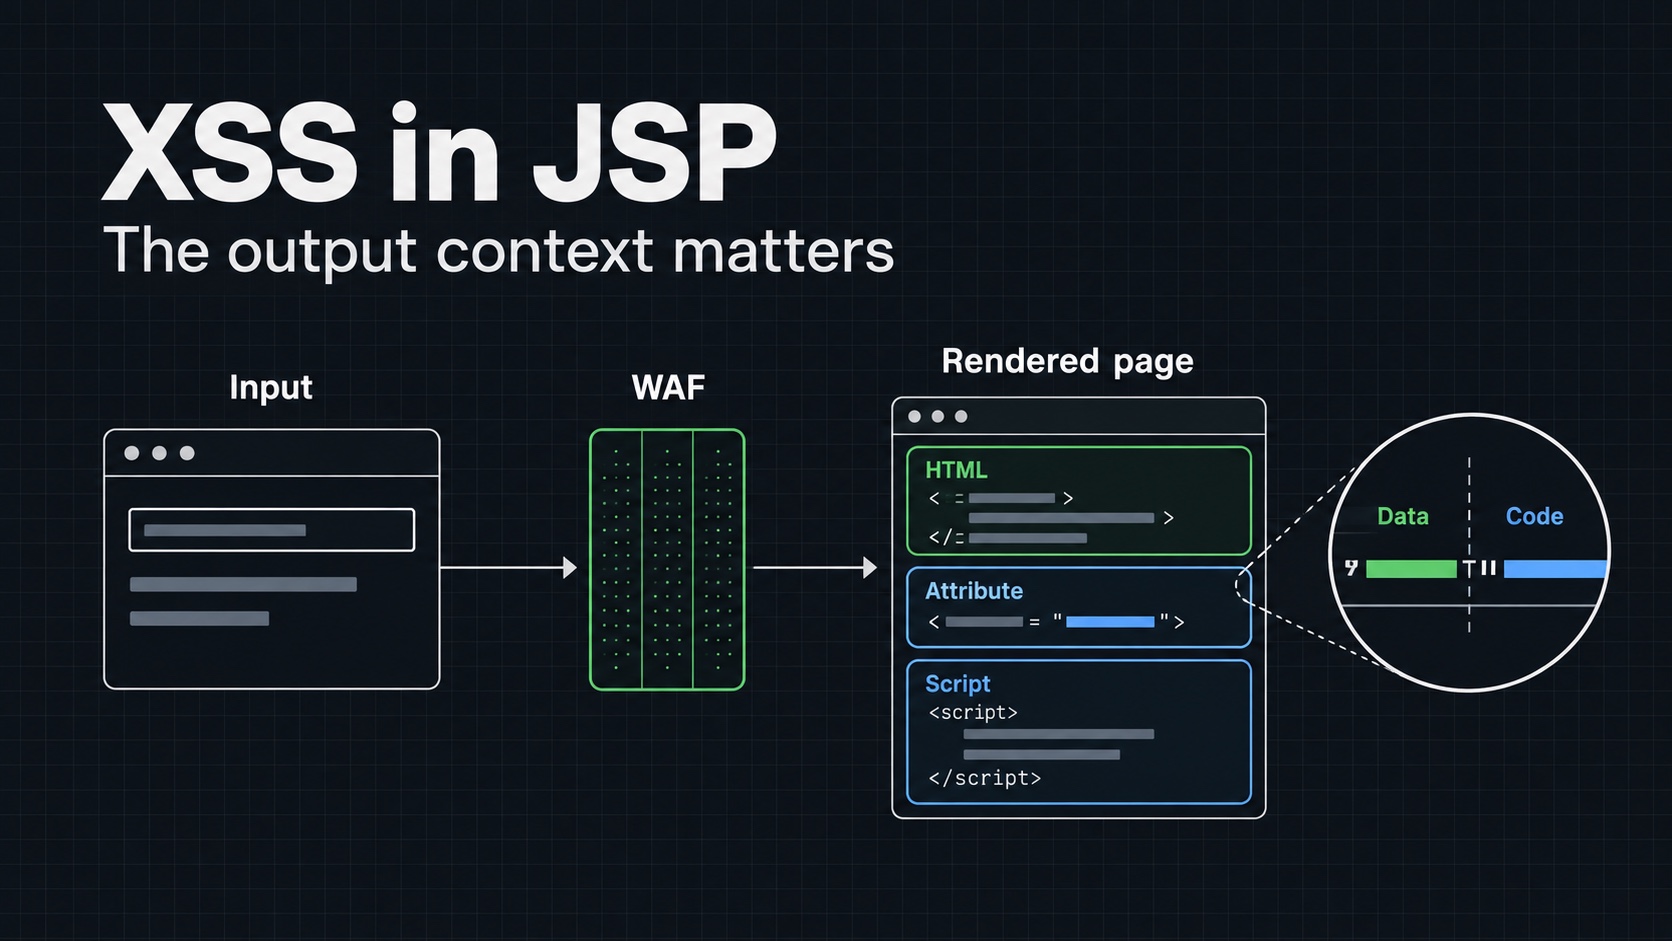
How I evaluate a small set of historical XSS probes and separate WAF behavior from a browser-confirmed application vulnerability.
A practical directory for infrastructure research, threat intelligence, code search, and historical context, with corrections to older entries.
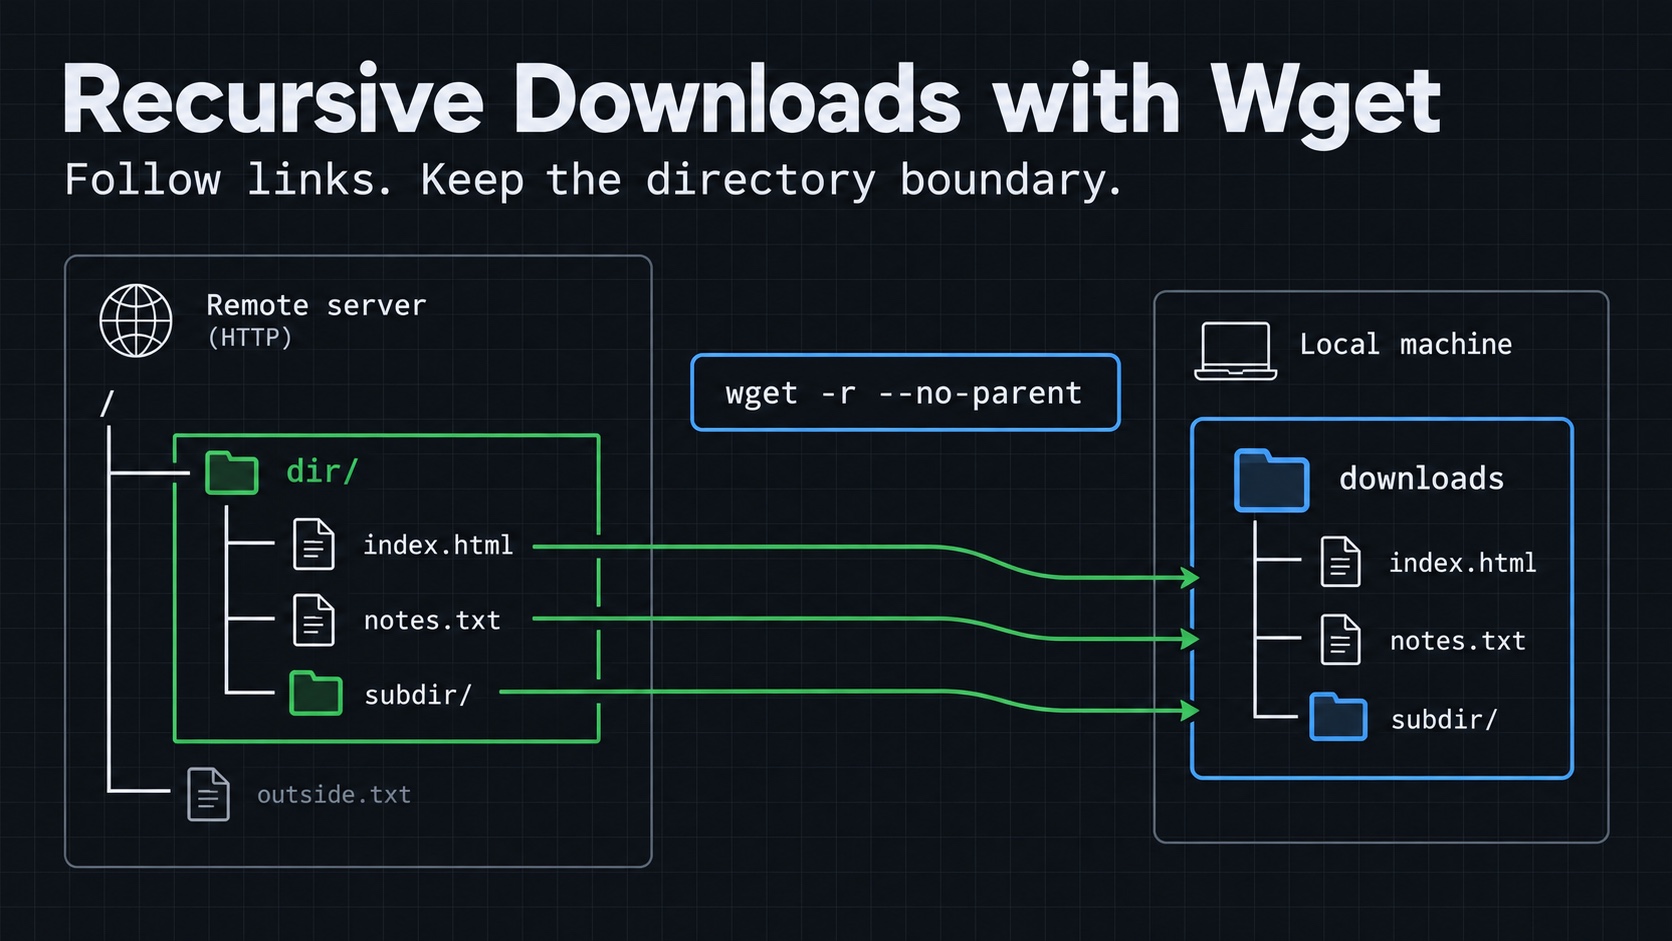
How I use Wget to download linked files under a web directory, control recursion, and check what was saved.
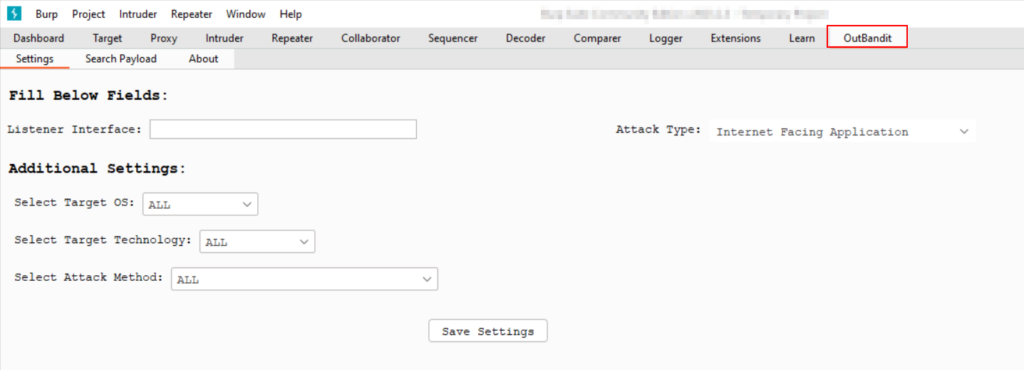
Why I built OutBandit for Burp Suite, how I approach callback testing, and what an HTTP or DNS interaction can actually prove.
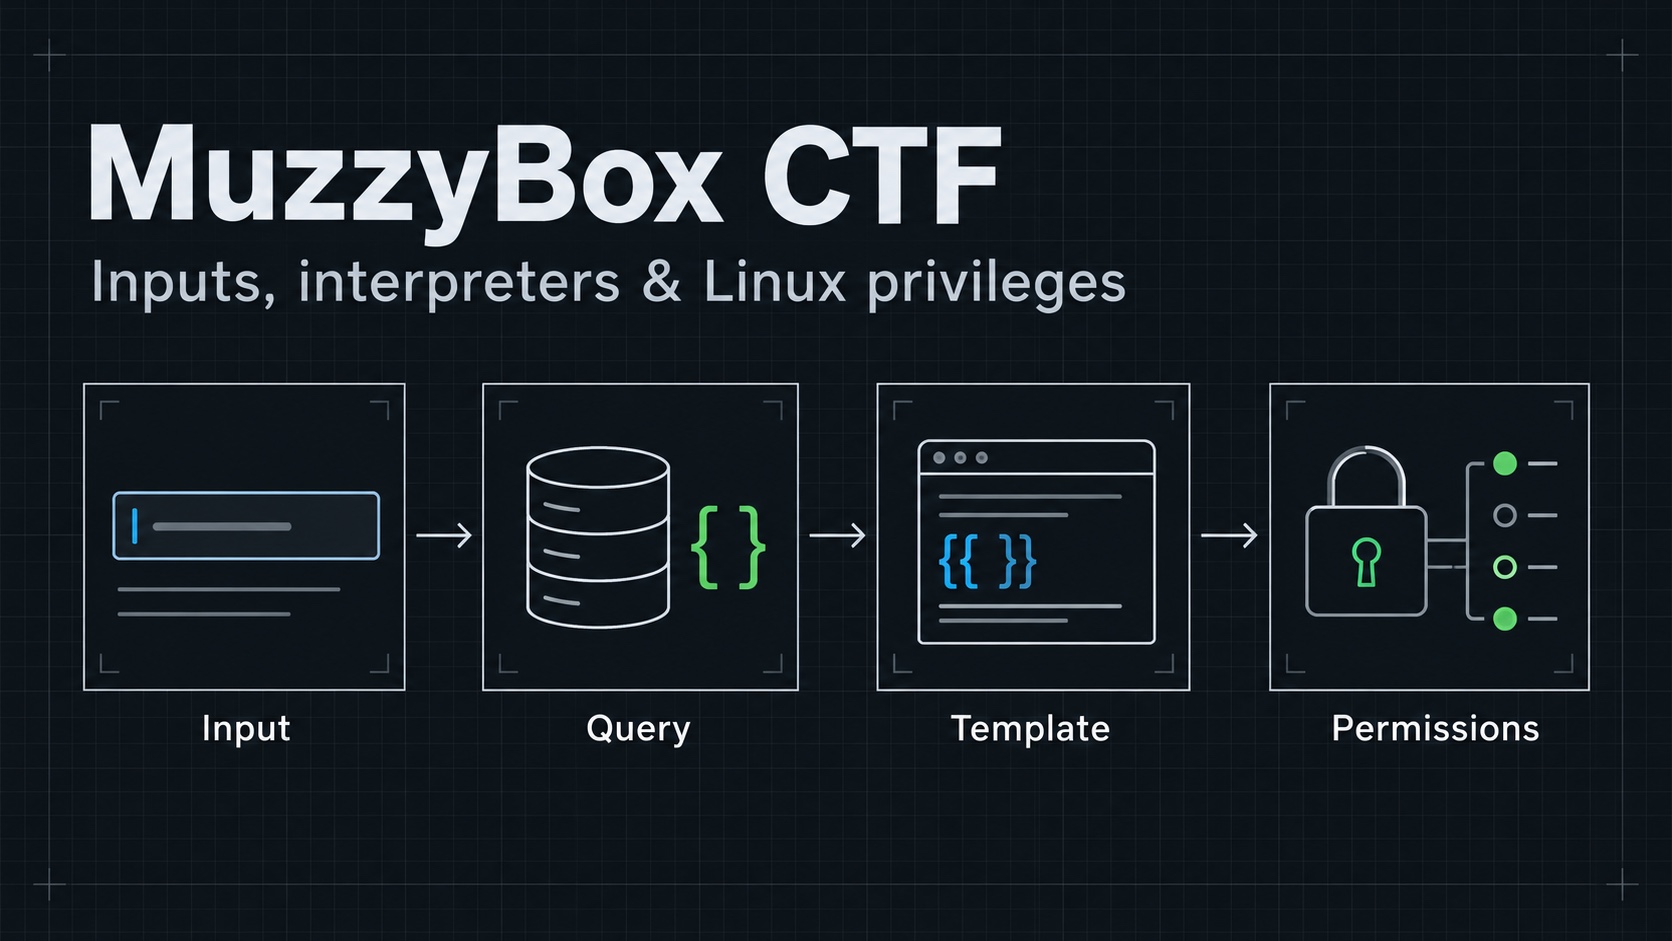
An introduction to my MuzzyBox CTF and the questions I use to investigate NoSQL injection, Python evaluation, SSTI, and Linux escalation.
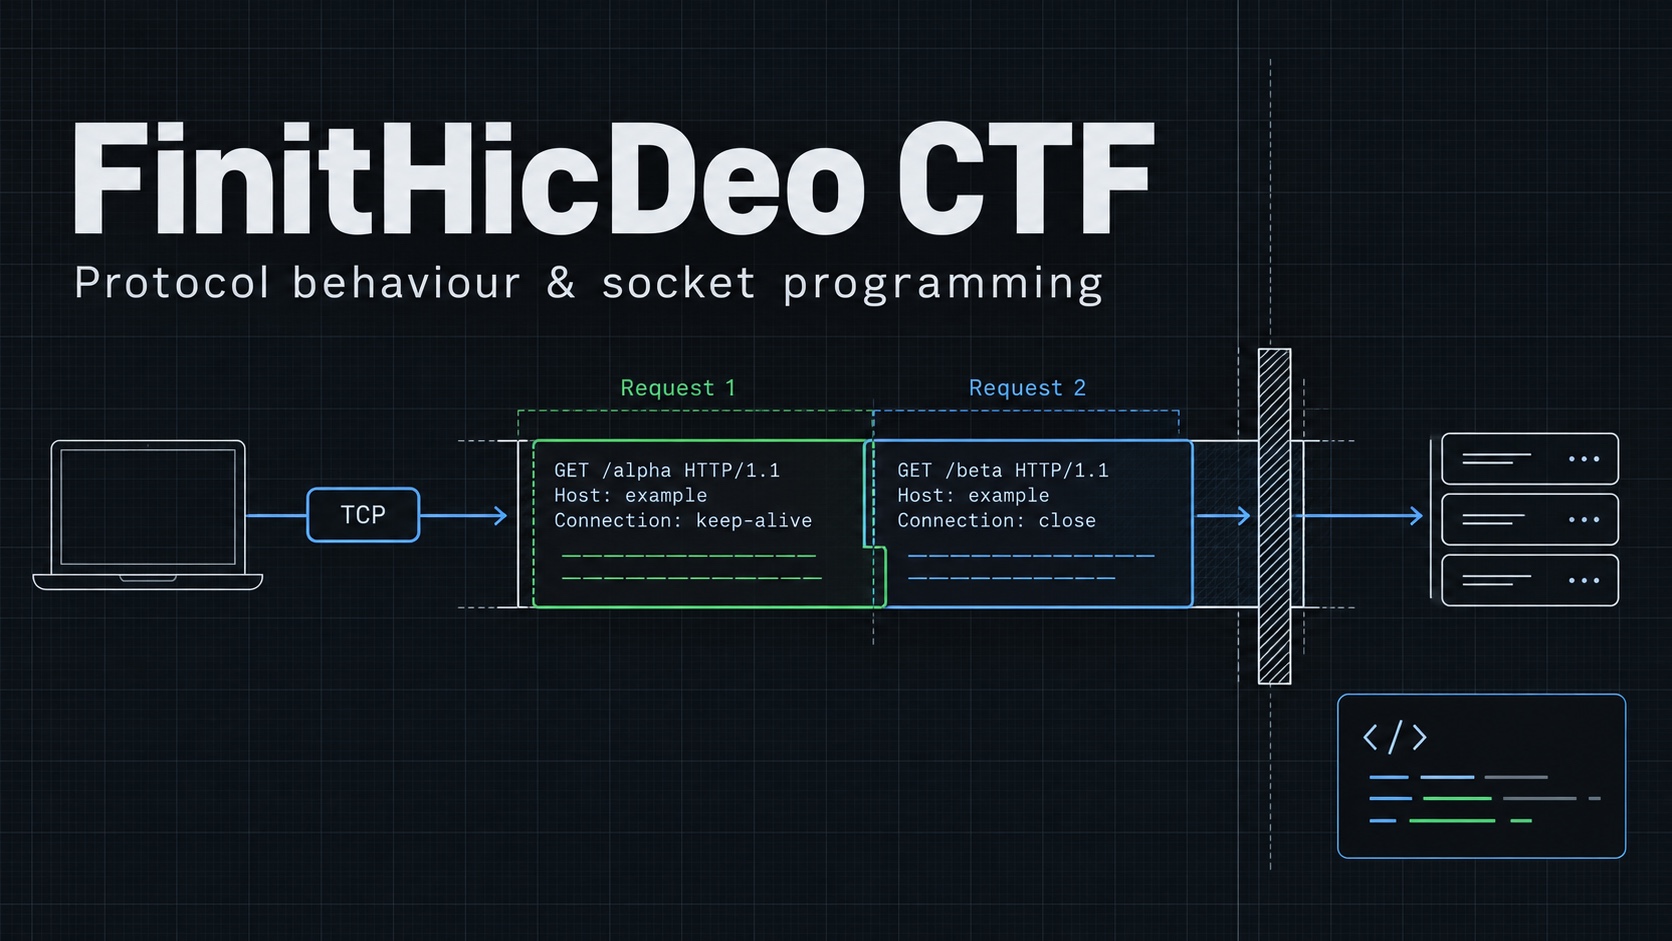
An introduction to FinitHicDeo, its programming and request-smuggling themes, and the evidence I would keep while solving the lab.
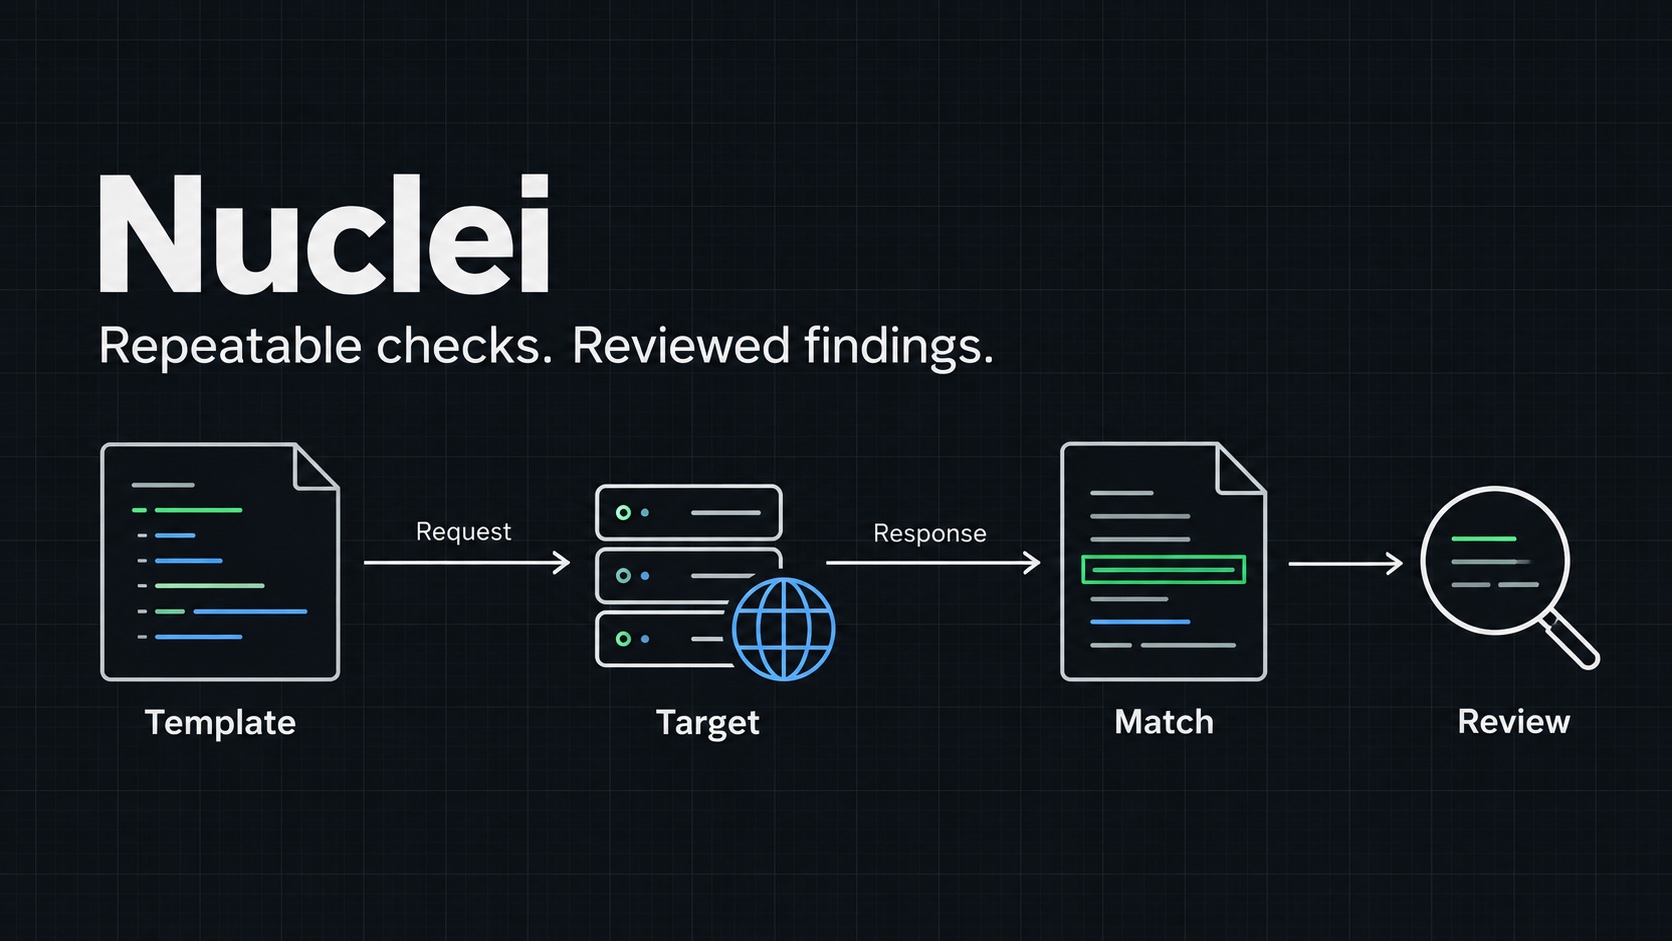
How I use Nuclei templates to run focused security checks, preserve evidence, and validate findings before reporting them.
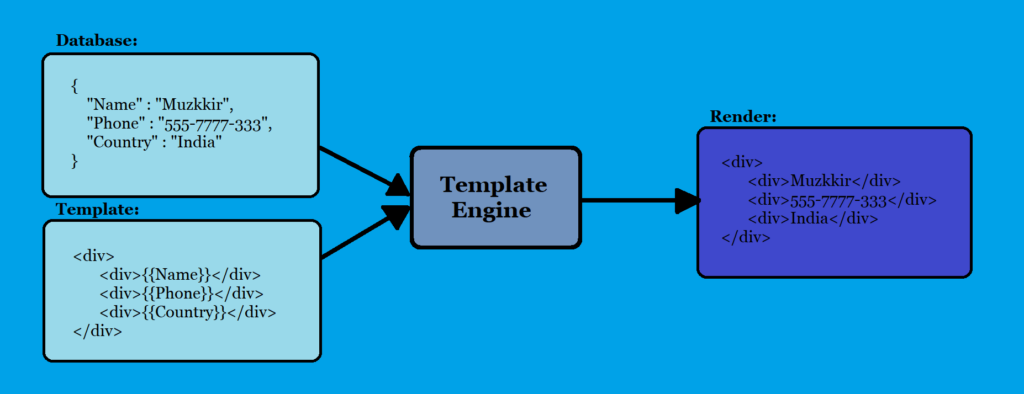
How I identify server-side template injection, reproduce it in a small Flask lab, and fix the separation between template source and data.